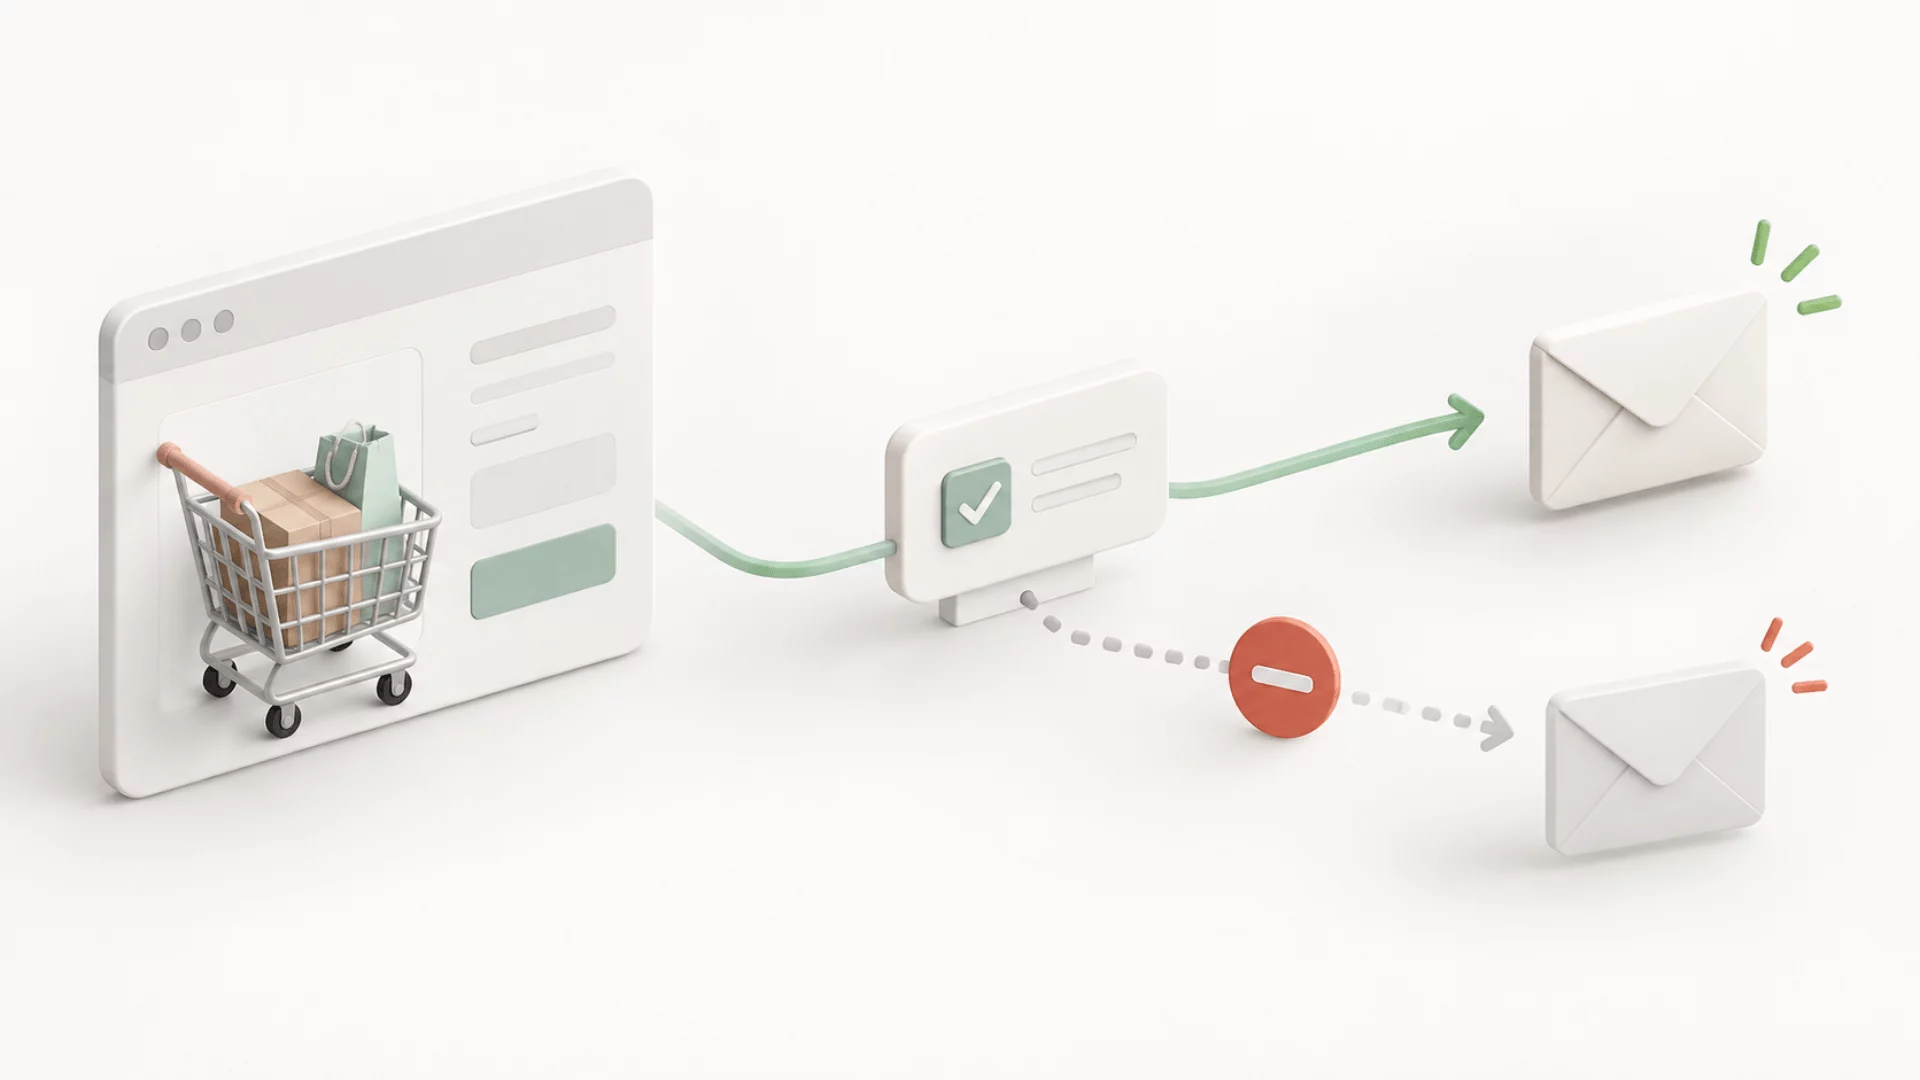
AMSTERDAM/WIESBADEN — For the vast majority of e-commerce professionals, the operational mechanics of the "abandoned cart" email were settled science years ago. A prospective buyer populates an online shopping basket, hesitates at the final billing stage, and closes the browser tab. Within a matter of hours, an automated sequence triggers, landing a friendly reminder in their inbox—often accompanied by a modest discount code—to lure them back to complete the transaction.
It is a staple of modern digital merchandising, built on the assumption that a partially completed checkout represents a warm lead crying out for a gentle nudge.
According to recent legal assessments and regulatory crackdowns, however, that assumption is not only legally untenable under European law; it is a direct violation of the ePrivacy Directive and the General Data Protection Regulation (GDPR).
In mid-September, legal experts at Dutch technology law firm ICTRecht revisited the issue, delivering a definitive answer to a question many digital marketing teams stopped asking long ago: Can you legally email someone who filled a shopping basket and abandoned it before purchasing?
The answer, unequivocal and sharp, is no—not without prior, explicit consent or a pre-existing customer relationship.
This position, reinforced by European data protection authorities and contextualized by recent rulings from the Court of Justice of the European Union (CJEU), threatens to upend standard direct marketing practices across the European Economic Area (EEA). More critically, it exposes a widespread compliance gap where technical convenience routinely supersedes legal obligation.
Main Facts: The Anatomy of a Regulatory Collision
At the core of the issue is a fundamental collision between marketing automation technology and European privacy frameworks.
Direct marketing rules within the EEA are governed strictly by the principle of permission. Under the ePrivacy Directive, electronic mail sent for commercial purposes—commonly known as direct marketing—requires the prior consent of the recipient (the classic "opt-in" model).
An exception exists for existing customers: if an individual has purchased a product or service, the vendor may send marketing communications concerning their own similar products or services, provided the customer was given a clear opportunity to opt out at the time their data was collected (the "soft opt-in").
Abandoned cart emails sit precariously at the intersection of these rules. Because these messages possess an undeniably commercial intent, they are classified as direct marketing. Consequently, they require an opt-in.
However, when a user abandons a checkout process, no commercial transaction has taken place. The "customer relationship exception" requires a completed purchase and a product category similar to the one being marketed. Because neither criterion is met when a browser drops off at the payment gateway, the legal justification for sending an unsolicited reminder vanishes.
Despite this clear legal boundary, the martech ecosystem has spent years optimizing for frictionless capture, frequently bypassing consent requirements in the pursuit of recovered revenue.
Chronology: How the Cart Recovery Crackdown Unfolded
To understand how the industry arrived at this enforcement impasse, it is necessary to trace the trajectory of recent regulatory developments and judicial clarifications.
Early Days: The Wild West of Conversion Rate Optimization
For well over a decade, cart abandonment software operated in a regulatory gray zone. As e-commerce platforms like Shopify, Magento, and WooCommerce matured, abandoned cart recovery became an out-of-the-box feature. Vendors pitched these tools as essential conversion rate optimization (CRO) tactics. Few questioned the legal provenance of the email addresses collected, provided they were entered into a form field during the checkout flow.
November 2023: The CJEU Clarifies the "Soft Opt-in"
The legal boundaries of direct marketing were further tightened by the Court of Justice of the European Union in the Inteligo Media ruling. The court examined whether a free account registration could count as obtaining contact details in the context of a sale, thereby allowing a freemium publisher to distribute its newsletter under the soft opt-in exemption without monetary consideration changing hands.
The CJEU ruled that a completed registration could indeed serve this purpose for free tiers. While the judgment provided a narrow pathway for digital publishers, it underscored a vital precondition: it requires a registration the user actually completed. An abandoned checkout, by definition, is an incomplete interaction. It lacks the formal contractual conclusion or account creation that characterizes the soft opt-in.
2024: The Hessian Data Protection Authority Drops the Hammer
The theoretical debate shifted to practical enforcement when the Hessian data protection authority in Germany (Der Hessische Beauftragte für Datenschutz und Informationsfreiheit) laid out its definitive position in its 2024 annual activity report.
The authority’s stance was prompted by a wave of consumer complaints targeting webshops that aggressively emailed individuals who had browsed, added items to a cart, entered an email address, but ultimately never completed a purchase.
The Hessian DPA clarified that these retargeting emails constitute direct marketing and are therefore unlawful without prior consent. The ruling established a clear precedent within Germany, signaling to other European supervisory authorities that cart abandonment sequences are a prime target for enforcement.
September 16, Harris and ICTRecht: Re-evaluating the Baseline
Bringing the conversation back to the Netherlands, ICTRecht published a comprehensive analysis on September 16, breaking down the technical and legal realities of retargeting mail. The publication served as a blunt wake-up call to Dutch e-commerce teams, confirming that the German enforcement logic applies universally across jurisdictions bound by the GDPR and ePrivacy frameworks.
Supporting Data: The Technical Architecture of Non-Compliance
While legal scholars debate the nuances of the ePrivacy Directive, the operational reality within e-commerce infrastructure reveals a deeper problem: the technical mechanics of modern webshops are frequently built to ignore the law.
1. The Broken Implementation of Consent Flags
Most legal commentary on the subject reduces the problem to a simple directive: "add a checkbox." Because of this, standard e-commerce implementations almost universally feature a marketing consent checkbox at checkout.
Platform giants like Shopify have built this natively into their architecture. In Shopify’s checkout ecosystem, the abandoned checkout API record includes a specific boolean data point: buyer_accepts_marketing, sitting right next to the customer’s email address.
Crucially, this value is frequently false—reflecting the user’s choice not to opt in, or their failure to check the box before abandoning the page.
The systemic failure does not lie in the data’s absence, but in its utilization. The checkout record is transmitted to downstream email marketing platforms like Klaviyo, Omnisend, or ActiveCampaign regardless of whether that boolean reads true or false. If the integration layer fails to read the buyer_accepts_marketing flag—or if the marketing team configures the automation flow to ignore it—the platform executes the abandoned cart sequence anyway, directly violating European law.
2. Pre-Submit Capture and Stealth Data Harvesting
The compliance crisis deepens when examining pre-submit data capture.
A lucrative industry of identity resolution and form-abandonment vendors now sells tracking scripts designed to bypass the traditional checkout barrier entirely. These tags utilize advanced DOM-scraping and browser events to read the email address field on "blur" (the exact moment a user clicks away from the input box), harvesting the address before the user ever clicks "Submit" or proceeds to the next page.
This is precisely how these vendors market their efficacy: they find carts you otherwise would have no record of because the user abandoned the form mid-stroke.
Under the EEA’s legal framework, this practice represents a severe compliance violation. The user never handed over the data for marketing purposes, nor did they complete the form. Consequently, there is no lawful basis for processing under GDPR Article 6.
Paradoxically, a close read of many identity resolution vendors’ own product documentation and terms of service reveals quiet disclaimers warning EEA-based clients about these exact restrictions—disclaimers that are frequently overlooked by desperate marketing teams hunting for marginal gains in conversion rates.
Official Responses and Deliverability Consequences
As regulatory scrutiny intensifies, the repercussions of unlawful cart recovery are expanding beyond regulatory fines and data protection audits into an arena that touches the bottom line immediately: email deliverability.
Major mailbox providers—most notably Google and Yahoo—have implemented stringent deliverability thresholds for bulk senders. Under current guidelines, senders must maintain a spam complaint rate well below 0.3%, with an ideal target of under 0.1%. Exceeding these thresholds results in automated filtering, throttling, or outright domain blacklisting.
This introduces a severe operational hazard for e-commerce operators who persist with non-compliant cart recovery campaigns.
Typically, cart recovery sequences are dispatched from the exact same primary sending domain utilized for transactional communications—order confirmations, shipping notifications, password resets, and customer service inquiries.
When automated systems blast unsolicited retargeting emails to users who never opted in, recipient friction skyrockets. Users who do not recognize or recall the brand—or who feel spied upon by aggressive pre-submit capture tools—frequently hit the "Mark as Spam" button.
Because spam complaints are calculated as a percentage of overall mail volume sent from a domain, a surge of complaints triggered by unlawful cart recovery emails poisons the domain’s reputation. The collateral damage is swift: legitimate transactional emails—order receipts and shipping updates destined for actual, paying customers—begin landing in spam folders, crippling customer support operations and eroding brand trust.
Implications: What E-Commerce Teams Must Do Now
The convergence of strict regulatory enforcement from authorities like the Hessian DPA, judicial clarifications from the CJEU, and tightening infrastructural rules from Google and Yahoo signals the end of an era for passive, consent-free conversion tactics.
E-commerce organizations operating within or targeting customers in the European Economic Area must undertake an immediate audit of their marketing automation pipelines. Key strategic shifts are now required:
- Audit the Data Pipeline: Marketing teams must verify that downstream customer relationship management (CRM) and email marketing platforms actively read and respect consent flags (such as Shopify’s
buyer_accepts_marketingboolean) before triggering any automated recovery sequence. - Purge Pre-Submit Trackers: Organizations must evaluate identity resolution and form-abandonment scripts operating on their checkout pages. If an email address is harvested before a user explicitly submits a form or grants marketing consent, its storage and utilization constitute an unlawful data processing activity under GDPR.
- Re-Architect Consent Workflows: To legally recover abandoned carts, brands must capture explicit, unbundled marketing consent prior to or at the exact moment contact data is captured for retargeting purposes—a difficult UX challenge that requires innovative, transparent form design rather than aggressive covert tracking.
- Isolate Sending Infrastructure: Brands that continue to flirt with aggressive retention strategies must separate their transactional and marketing domains to insulate critical customer service communications from the inevitable deliverability penalties associated with high spam complaint rates.
The era of treating the checkout funnel as a data vacuum—where every keystroke is fair game for commercial exploitation—is officially over. For European e-commerce teams, compliance is no longer a box to be checked; it is a fundamental design constraint that will dictate who survives in an increasingly regulated digital marketplace.