SYDNEY — In a stunning revelation that has sent ripples through Australia’s digital governance and cybersecurity communities, the nation’s corporate watchdog has admitted that official correspondence sent to Gmail users went undelivered for more than five months.
The Australian Securities and Investments Commission (ASIC), the country’s primary corporate, markets, and financial services regulator, disclosed late last month that a systemic technical glitch intercepted and blocked outbound emails originating from its @asic.gov.au domain to Google’s widely used consumer and business email platform. The failure, which quietly persisted through the autumn and winter months, has raised urgent questions regarding institutional oversight, automated monitoring systems, and the vulnerability of government-to-citizen digital infrastructure.
While the regulator maintains that the underlying issue has been identified and neutralized, the fallout from the blackout is only beginning to unfold. With millions of Australians relying on Gmail for personal and professional communications, the inability of a key economic regulator to reach citizens via electronic mail for over 150 days highlights critical vulnerabilities in how public sector agencies manage and audit their digital communication pipelines.
1. Main Facts: The Scope and Nature of the Outbreak
The core of the incident centers on a silent communication blackout between one of Australia’s most critical regulatory authorities and one of the world’s largest email service providers.
According to official disclosures released by ASIC, outbound communications originating from the domain asic.gov.au failed to reach their intended destinations within the Google Gmail ecosystem. The disruption was not a momentary server hiccup or a brief DNS outage; rather, it was a persistent delivery failure that spanned nearly half a year, operating completely undetected by the sender’s internal technical teams.
- Affected Domain:
@asic.gov.au - Target Platform: Google Gmail (including both free
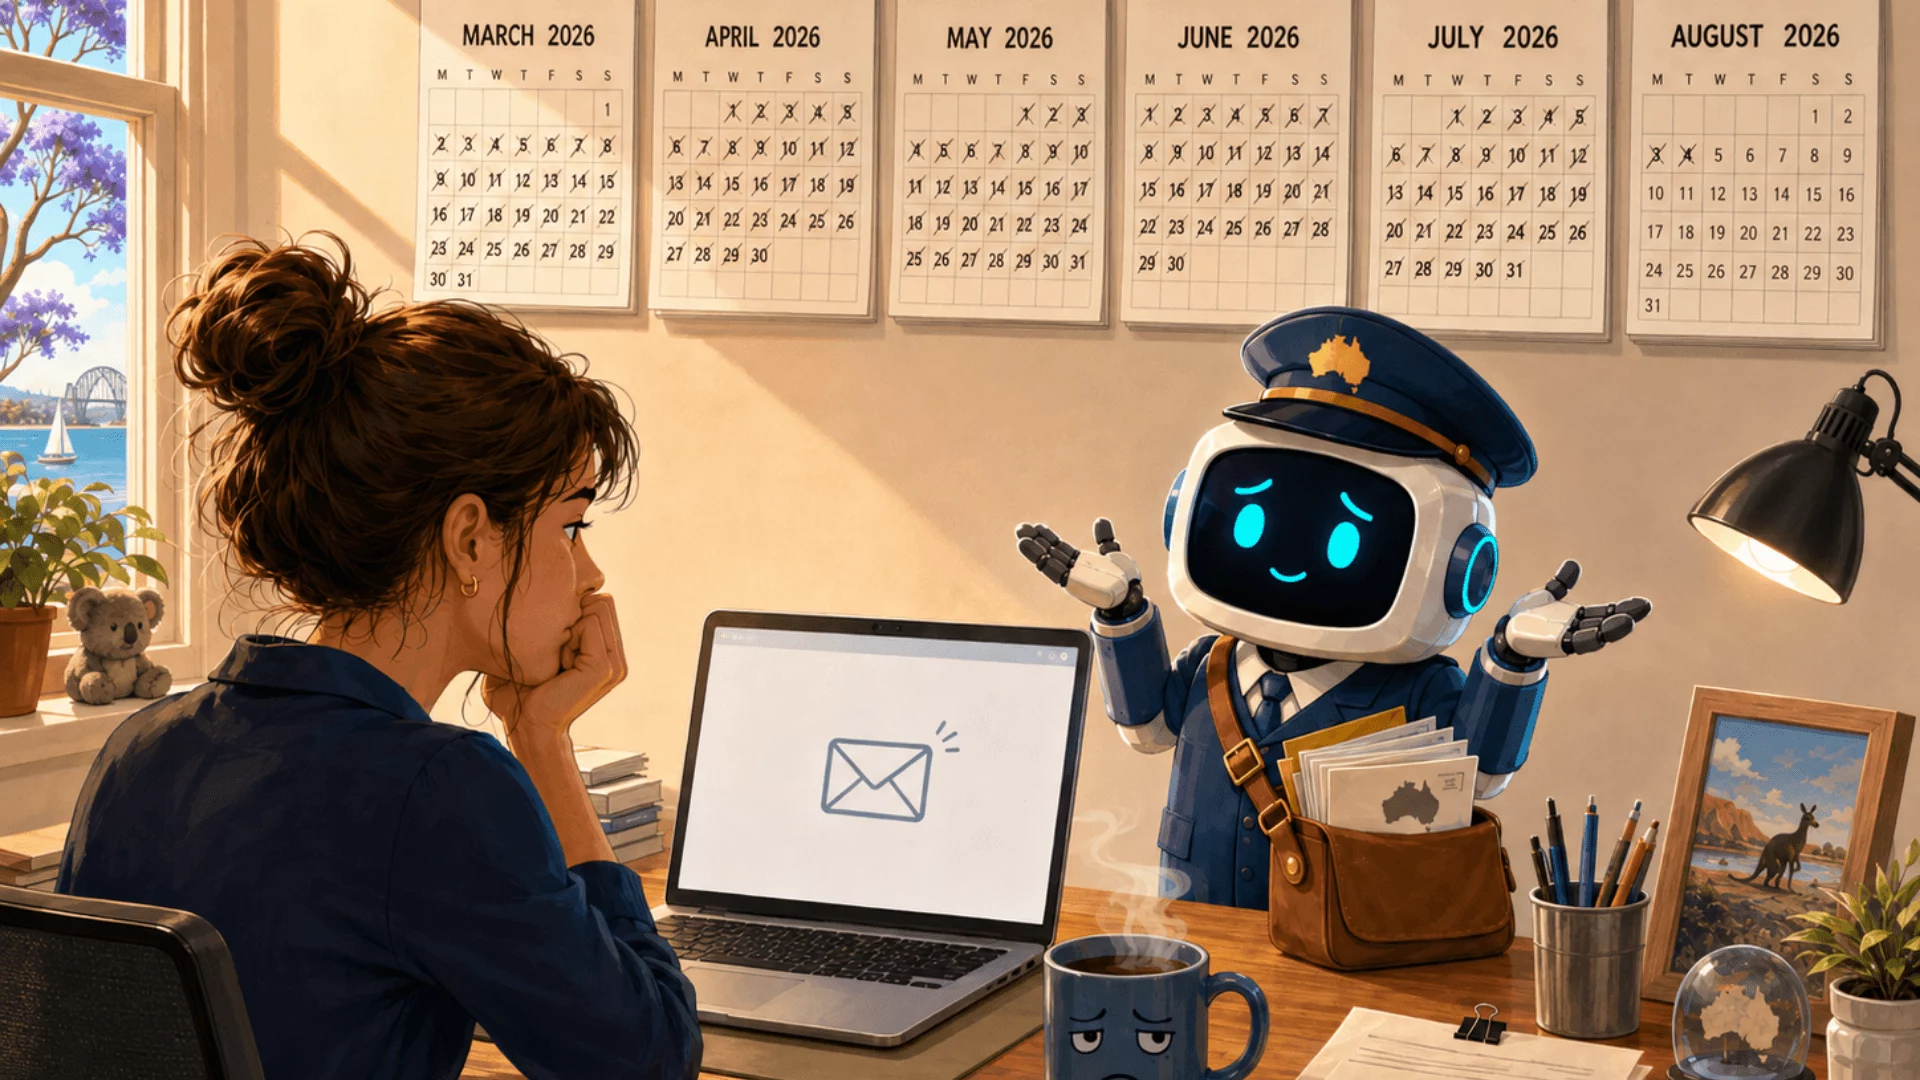
@gmail.comaccounts and Google Workspace domains utilizing Gmail infrastructure). - Duration: March 1, 2026, through August 3, 2026.
- Disclosure Date: August 27, 2026.
- Remediation Status: ASIC claims the technical root cause has been isolated and resolved, with outreach campaigns planned for impacted entities where subsequent actions—such as regulatory filings or renewals—are legally mandated.
Despite the gravity of the disclosure, major gaps remain in the public record. ASIC has steadfastly declined to quantify the exact volume of missed messages, nor has it released a comprehensive breakdown of the functional categories of correspondence that failed to transit. Whether the blocked dispatches included routine administrative notices, urgent compliance warnings, or sensitive legal correspondence remains obscured behind a veil of regulatory discretion.
2. Chronology of Events: From Silent Failure to Public Disclosure
Reconstructing the timeline of the ASIC-Gmail delivery failure reveals a troubling lag between operational failure, internal discovery, and public transparency.
March 1, 2026: The Silence Begins
Without public warning or internal alarm, the technical barrier between ASIC’s mail servers and Google’s intake filters drops. Outbound messages from @asic.gov.au addressed to Gmail accounts begin failing. Whether these emails were outright rejected at the gateway via SMTP bounce-backs, silently dropped into void queues, or flagged as severe spam anomalies remains unconfirmed by the regulator.
March – July 2026: The Invisible Gap
For 152 days, the silent drop persists. During this window, tens of thousands of Australian businesses, directors, and consumers interact with ASIC’s digital ecosystem. They submit corporate queries, await registration updates, and anticipate renewal prompts that never materialize. Because modern digital users have come to expect near-instantaneous electronic communication, the absence of mail is often misattributed to bureaucratic processing delays rather than a complete breakdown in network transit.
August 3, 2026: The Silent Resolution
According to ASIC’s technical logs, the underlying configuration or authentication issue is quietly rectified. Outbound mail to Gmail accounts successfully resumes its normal flow. However, no immediate public statement is issued, leaving stakeholders entirely unaware that a five-month communication vacuum had just been plugged.
August 27, 2026: Official Disclosure
Nearly four weeks after fixing the issue, ASIC breaks its silence. The commission publishes a concise notice on its online services support portal, admitting to the five-month delivery blackout. The announcement is minimalist, lacking technical specifics, volume metrics, or granular details regarding the root cause.
Late August – Present: The Aftermath
ASIC initiates internal audits to identify high-risk accounts impacted by the outage. Plans are drawn up to contact affected customers directly, particularly those who may have missed statutory deadlines due to the missing notices. Independent digital security experts and IT professionals begin picking apart the announcement, demanding deeper accountability from public sector IT leadership.
3. Supporting Data and Technical Context: The Anatomy of an Email Blackout
To understand how a government agency could lose contact with a major email provider for five months, industry analysts must examine the complex mechanics of modern email authentication, domain reputation, and server-side filtering.
The Black Box of Public Sector IT
Government agencies like ASIC handle millions of digital touchpoints annually. Their mail transfer agents (MTAs) are tasked with dispatching a staggering array of automated notifications, ranging from simple password resets to complex, legally binding regulatory decrees.
When configuring enterprise email systems, organizations rely heavily on three foundational email authentication protocols to prove their identity to receiving servers like Google:
- SPF (Sender Policy Framework): Specifies which mail servers are authorized to send email on behalf of a domain.
- DKIM (DomainKeys Identified Mail): Adds a cryptographic digital signature to emails, verifying that the email was genuinely sent by the domain owner and was not altered in transit.
- DMARC (Domain-based Message Authentication, Reporting, and Conformance): Tells the receiving server what to do if SPF or DKIM fails (e.g., monitor, quarantine, or outright reject the message).
In recent years, major tech giants like Google and Yahoo have dramatically tightened their DMARC and spam enforcement policies. Unauthenticated or misconfigured bulk senders face immediate penalties, ranging from aggressive throttling to total domain blacklisting.
While ASIC has not disclosed the exact technical catalyst, infosec analysts suggest several plausible scenarios:
- DMARC/SPF Misconfiguration: A routine update to ASIC’s corporate DNS records or third-party mailing vendors could have broken its SPF alignment, causing Google’s strict security filters to reject incoming mail en masse.
- IP Reputation Decay: If ASIC’s outbound mail servers shared a pool of IP addresses that experienced a sudden spike in spam-like behavior or triggered spam traps, Google’s automated defense systems would have automatically severed trust with those specific IPs.
- TLS Handshake and Encryption Failures: Mismatched security certificates or outdated cipher suites between ASIC’s gateway and Google’s mail ingestion nodes could have caused persistent session termination errors.
The Monitoring Deficit
The most alarming aspect of the technical data—or lack thereof—is the absence of internal telemetry. Enterprise-grade mail servers typically generate robust delivery reports, including bounce logs (NDRs – Non-Delivery Reports) and feedback loops from major providers like Google (Postmaster Tools).
For a delivery failure to persist for over 150 days without internal alarms being triggered suggests a severe blind spot in ASIC’s continuous monitoring infrastructure. If automated scripts or system administrators failed to track bounce rates for specific domain clusters (such as @gmail.com), it points to a systemic failure in proactive IT governance.
4. Official Responses and Institutional Accountability
The reaction from regulatory observers, legal professionals, and the corporate sector has been marked by a mixture of frustration and demand for transparency.
ASIC’s Stance: Remediation Over Rhetoric
In its published statements, ASIC has struck a defensive yet pragmatic tone. The regulator emphasizes that it has successfully diagnosed the fault and is actively working to mitigate collateral damage.
"ASIC has identified and fixed a technical issue that affected some emails sent from our @asic.gov.au domain to Gmail accounts between 1 March and 3 August 2026," the commission stated in its official release. "We are actively identifying affected customers where further regulatory or administrative action may be required as a result of this disruption."
However, the commission has faced criticism for withholding critical metrics. By refusing to disclose the total number of bounced messages or the exact percentage of Gmail users impacted, ASIC has made it difficult for independent auditors to assess the true scale of the administrative breakdown.
Industry and Expert Backlash
Email delivery specialists and cybersecurity advocates have been vocal in their critique of the incident’s timeline. Speaking on condition of anonymity, several enterprise messaging consultants pointed out that automated monitoring tools are readily available to detect sudden drops in delivery success rates within hours—not months.
"If an enterprise mail server suddenly stops successfully delivering mail to the world’s largest consumer email provider, alarms should be ringing within minutes," noted one senior systems architect. "For this to persist for five months means nobody was watching the metrics, or worse, the telemetry data was being ignored."
Furthermore, consumer advocacy groups have raised concerns regarding liability. In Australia, corporate entities and registered business names are subject to strict, legally mandated renewal timetables. Failure to respond to notices within statutory timeframes can result in late fees, business deregistration, or the inadvertent loss of trademarked corporate names.
Legal experts warn that if businesses suffer financial harm or operational paralysis due to missed ASIC notices—such as delayed deregistration warnings—the regulator could face complex liability questions. While government immunity shields agencies from certain types of civil litigation, administrative law principles require public bodies to exercise reasonable care in executing their statutory duties.
5. Broader Implications: Cybersecurity, Governance, and Citizen Trust
Beyond the immediate administrative headache, the ASIC-Gmail delivery failure serves as a cautionary tale for public sector digitization across the globe. As governments increasingly transition their operations to cloud-native platforms and automated digital portals, the fragility of underlying communication infrastructure becomes a matter of national importance.
1. The Vulnerability of Monocultures in Communication
Modern digital communication is heavily centralized. A handful of corporate giants—principally Google, Microsoft (Outlook/Office 365), and Apple—control the vast majority of consumer and corporate email consumption. When a government regulator suffers a disconnect with just one of these pillars (in this case, Google), a significant portion of the population is instantly cut off from official state communications. This highlights the inherent risks of relying on centralized webmail infrastructure for essential civic discourse.
2. The Erosion of Public Trust in Digital Governance
Citizens are repeatedly urged by governments to adopt paperless, digital-first interactions. From tax filings to corporate renewals, the state demands that individuals and enterprises conduct their affairs electronically.
However, incidents like the ASIC email blackout expose a jarring double standard: while citizens face strict penalties for missing digital deadlines, state agencies are afforded months of grace when their own digital infrastructure fails. This asymmetry risks eroding public trust in e-government initiatives, breeding cynicism regarding the reliability of automated state machinery.
3. A Wake-Up Call for Enterprise Email Auditing
For Chief Information Officers (CIOs) and Chief Information Security Officers (CISOs) across both public and private sectors, the ASIC incident is a stark reminder to audit their outbound mail hygiene.
Best practices moving forward must include:
- Real-Time Delivery Analytics: Implementing continuous monitoring tools that track SMTP delivery success rates segmented by major destination domains (Google, Microsoft, Yahoo).
- Active Feedback Loops: Utilizing Google Postmaster Tools and Microsoft Smart Network Data Services (SNDS) to monitor IP reputation, encryption compliance, and spam complaint rates.
- Redundancy and Fallback Channels: Establishing secondary, out-of-band communication methods (such as SMS notifications or physical mail follow-ups) for critical, time-sensitive regulatory notices when electronic delivery fails or is unconfirmed.
Conclusion: Looking Ahead
As ASIC works through its backlog of remediation efforts and attempts to reconcile accounts impacted by the five-month blackout, the broader lessons of the incident must not be ignored.
The silence between Australia’s corporate regulator and its citizens has laid bare the invisible friction points of digital bureaucracy. While the technical glitch has been patched, restoring absolute confidence in the reliability of public sector electronic communications will require far greater transparency, rigorous auditing, and a renewed commitment to infrastructural resilience.
For now, Australian businesses and Gmail users are advised to proactively check their ASIC portals, review their corporate registry statuses, and ensure that their compliance obligations are fully up to date—remaining mindful that in the modern digital age, silence from the regulator does not always mean everything is well.
For ongoing updates or to check if your account was impacted, affected parties are directed to visit the official ASIC Customer Support Portal.