ROME — In a stern reminder that data privacy compliance extends far beyond front-end preference toggles, Italy’s data protection authority—the Garante per la protezione dei dati personali—has slapped the Italian branch of Spanish banking giant BBVA with a hefty €5.508 million fine.
The penalty, formalized in a decision published on September 3, 2026, stems from a seemingly mundane operational failure: a single customer who repeatedly opted out of promotional messaging through the bank’s mobile app and via direct customer service channels, only to find that marketing alerts continued to flood their device for months.
While the underlying technical glitch affected just one individual, the regulatory fallout has sent shockwaves through the compliance and marketing operations departments of financial institutions across Europe. The ruling highlights a critical vulnerability in modern tech stacks—the dangerous gap between what a customer requests in a preference center and how data propagates across downstream customer relationship management (CRM) systems.
Main Facts of the Case
At the heart of the Garante’s ruling is a foundational tenet of the European Union’s General Data Protection Regulation (GDPR): the absolute right of an individual to object to direct marketing, and the corresponding obligation of a data controller to honor that objection swiftly and seamlessly.
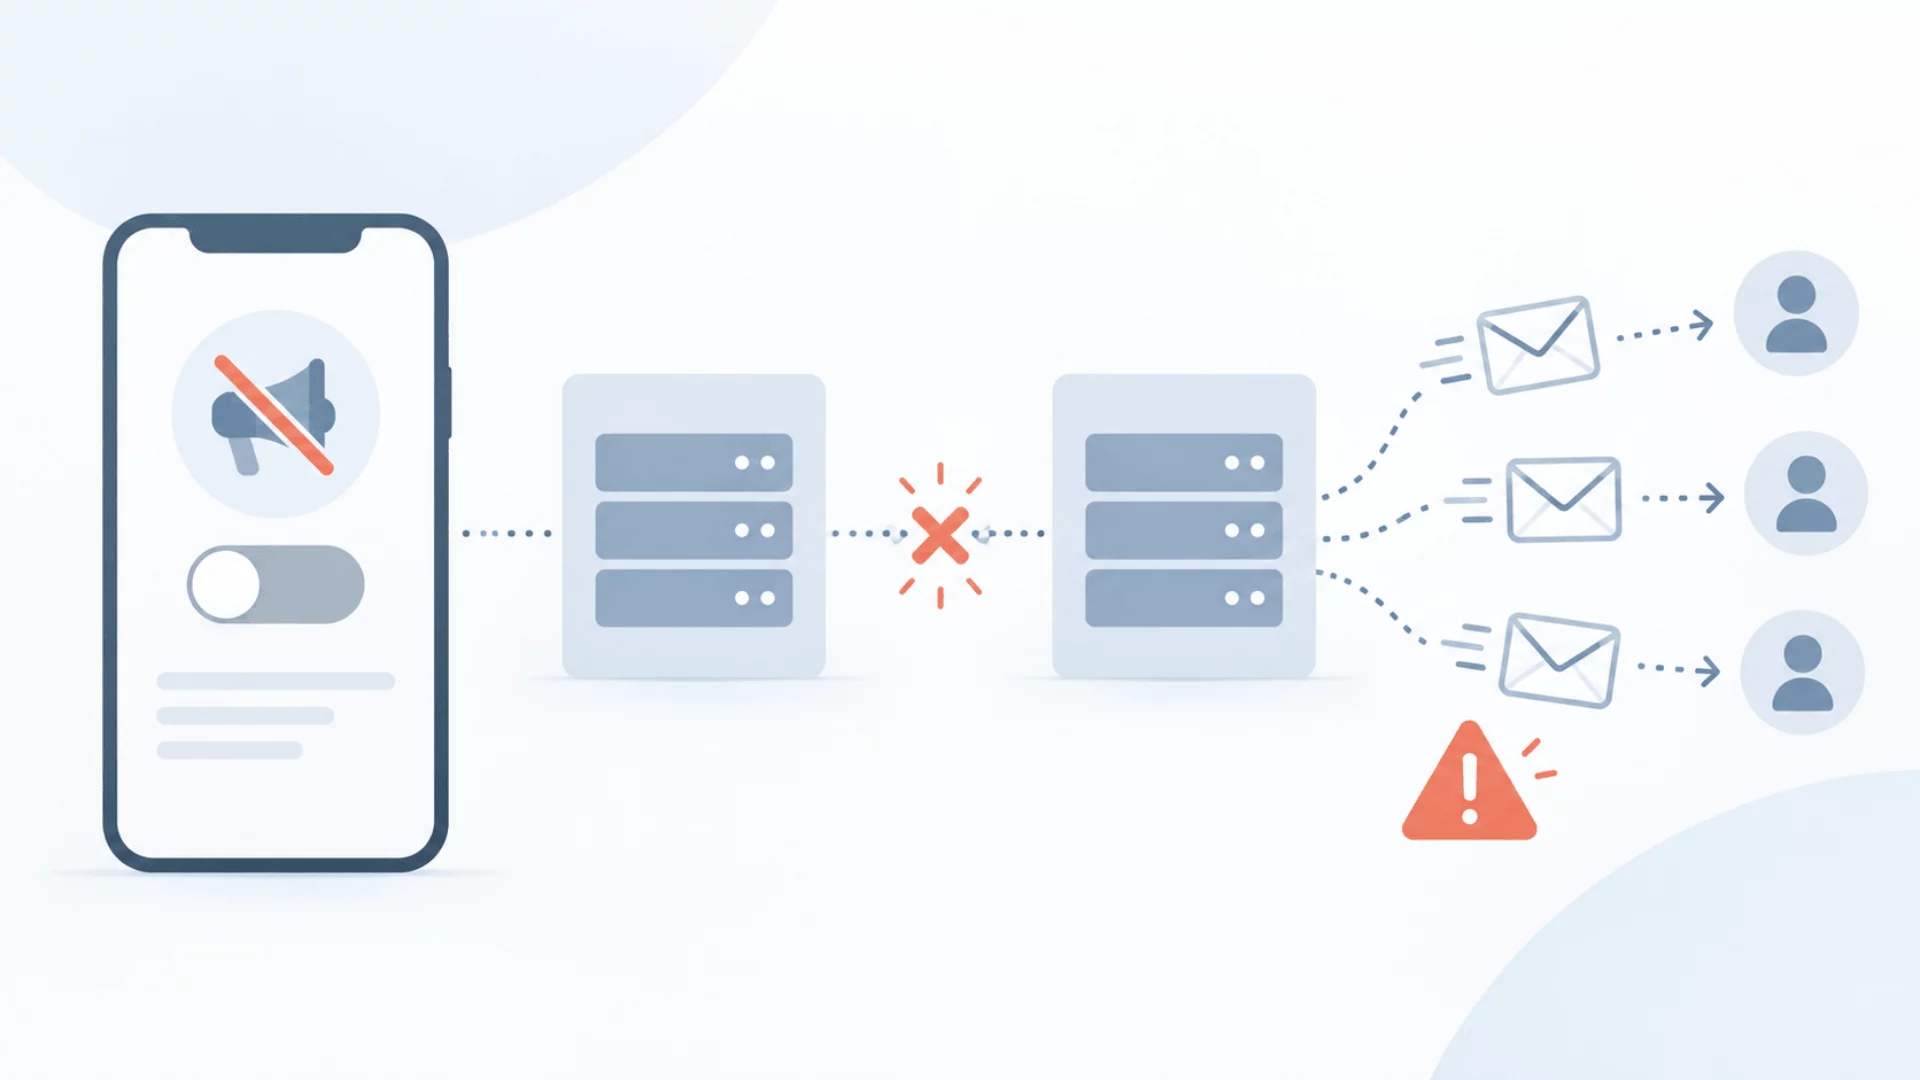
The ordeal began when a BBVA customer in Italy decided they no longer wanted to receive promotional notifications. The customer utilized the bank’s official mobile application to register their opt-out preference. Believing the matter settled, the customer was surprised when commercial notifications continued to appear.
In an effort to resolve the issue, the customer escalated the matter directly with BBVA’s customer service department on two separate occasions—October 2 and December 9, 2025. Despite these explicit instructions to cease marketing communications, the barrage of promotional alerts persisted.
The Garante’s investigation revealed that over a seven-month period, the customer received at least ten unwanted promotional notifications. Worse still, when the customer sought assistance on December 10, 2025, a BBVA customer service representative bizarrely informed them that the in-app promotional pop-ups could not actually be turned off and advised the customer to simply ignore them.
The regulator ultimately found BBVA in violation of multiple articles of the GDPR, including:
- Article 5: Principles relating to processing (fairness and transparency).
- Article 12: Transparent information, communication, and modalities for exercising the rights of the data subject.
- Article 21: The right to object to direct marketing.
- Article 24: Responsibility of the controller (the duty to implement appropriate technical and organizational measures).
Despite the bank arguing that the technical error was isolated to a single customer and carried a low severity regarding the core data breach, the Garante levied the multi-million-euro penalty. The final figure was influenced heavily by BBVA’s substantial turnover—surpassing €500 million—inadequate customer service training, and an aggravating factor: a prior ruling against the bank in July 2025 concerning a separate, sluggish response to a data access request.
Chronology of Events
To understand how a routine customer service inquiry escalated into a multimillion-euro regulatory penalty, it is necessary to examine the timeline of events that unfolded between late 2025 and mid-2026.
- October 2, 2025: Following an initial opt-out attempt via the BBVA mobile app, the customer contacts customer service to formally register their objection to receiving promotional messages. The marketing alerts, however, continue unabated.
- December 9, 2025: Frustrated by the persistence of the notifications, the customer contacts BBVA’s support team a second time to reiterate their demand to stop all commercial messaging.
- December 10, 2025: A BBVA customer service representative provides incorrect guidance, telling the customer that in-app promotional pop-ups cannot be disabled and instructing them to simply ignore the notifications.
- Early 2026 (Investigation Phase): Following a formal complaint, the Italian Garante launches an official inquiry into BBVA’s data handling practices and marketing compliance.
- Spring 2026: Prompted by the Garante’s intervention, BBVA finally conducts a comprehensive review of the customer’s profile, identifies the root cause of the synchronization failure, and successfully halts the promotional notifications.
- May 2026: The persistent stream of unwanted commercial notifications finally comes to a permanent halt, roughly seven months after the customer first registered their initial opt-out.
- September 3, 2026: The Garante officially publishes its exhaustive decision, detailing the GDPR violations and issuing the €5.508 million fine against BBVA’s Italian branch.
Supporting Data and Technical Breakdown
The core technical defense offered by BBVA during the proceedings was as intriguing as it was damning. The bank did not deny that the customer had attempted to opt out. Instead, BBVA explained that the opt-out preference had been recorded correctly and securely within the bank’s own core database systems.
However, a critical failure occurred: the data never synchronized with the separate database utilized by the CRM team to manage and execute commercial campaigns. In essence, the left hand of the bank’s digital infrastructure did not know what the right hand was doing.
Furthermore, BBVA attempted to deflect responsibility by arguing that the customer had failed to use the specific, dedicated email addresses and communication channels outlined in the bank’s official privacy policy for exercising data protection rights.
The Garante decisively dismantled this defense. The regulatory authority ruled that a corporation cannot simply ignore a clearly expressed objection to marketing just because it arrived through an alternative, yet equally legitimate, channel. The customer had utilized the native settings within BBVA’s own mobile application and subsequently reinforced that request through the bank’s primary customer service hotline—the most direct and natural touchpoint for any consumer interacting with a financial institution.
When the Garante factored in the financial weight of the penalty, it looked closely at three main elements:
- Corporate Turnover: Because BBVA’s Italian operations generate annual turnovers exceeding €500 million, the baseline potential for regulatory fines under the GDPR was substantial.
- Aggravating History: The bank’s recidivism played a decisive role. The Garante took strict note of a separate administrative penalty issued against BBVA just months prior (July 2025), which penalized the bank for unacceptably slow responses to customer data access requests. This established a concerning pattern of institutional sluggishness regarding data rights compliance.
- Mitigating Factors: BBVA was granted some leniency—and avoided a heavier financial penalty—due to its cooperation once the investigation was underway, and the fact that it rapidly patched the synchronization fault and updated its internal protocols.
Official Responses and Remediation
Faced with a public reprimand and a multimillion-euro sanction, BBVA moved quickly to address both the public relations fallout and the structural vulnerabilities exposed by the Garante.
In statements following the publication of the September 2026 decision, representatives for BBVA emphasized that the glitch was an isolated technical coordination issue that had affected only a single user out of its vast customer base. The bank underscored that it takes data privacy and consumer rights with the utmost seriousness.
To prevent a recurrence of the incident, BBVA announced that it has implemented a robust package of remediation efforts:
- System Synchronization Fixes: The technical bridge between the bank’s core user profiles and its downstream CRM database has been entirely overhauled to ensure real-time data propagation.
- Organizational Overhauls: Cross-departmental protocols between IT, data governance, and marketing operations have been tightened to eliminate data silos.
- Intensive Staff Training: Recognizing the failure of its support staff—who mistakenly told the customer that pop-ups could not be disabled—BBVA has rolled out mandatory, specialized data protection and privacy compliance training for all customer service representatives. This ensures that frontline staff can accurately guide consumers on privacy rights and correctly escalate technical complaints.
Implications for Marketing Operations and GDPR Compliance
While the case originated from a single consumer’s frustration, the regulatory ripple effects extend far beyond BBVA. The Garante’s decision serves as a mandatory wake-up call for marketing operations, chief compliance officers, and IT architects across the European Union.
1. The Fallacy of the "Isolated Opt-Out"
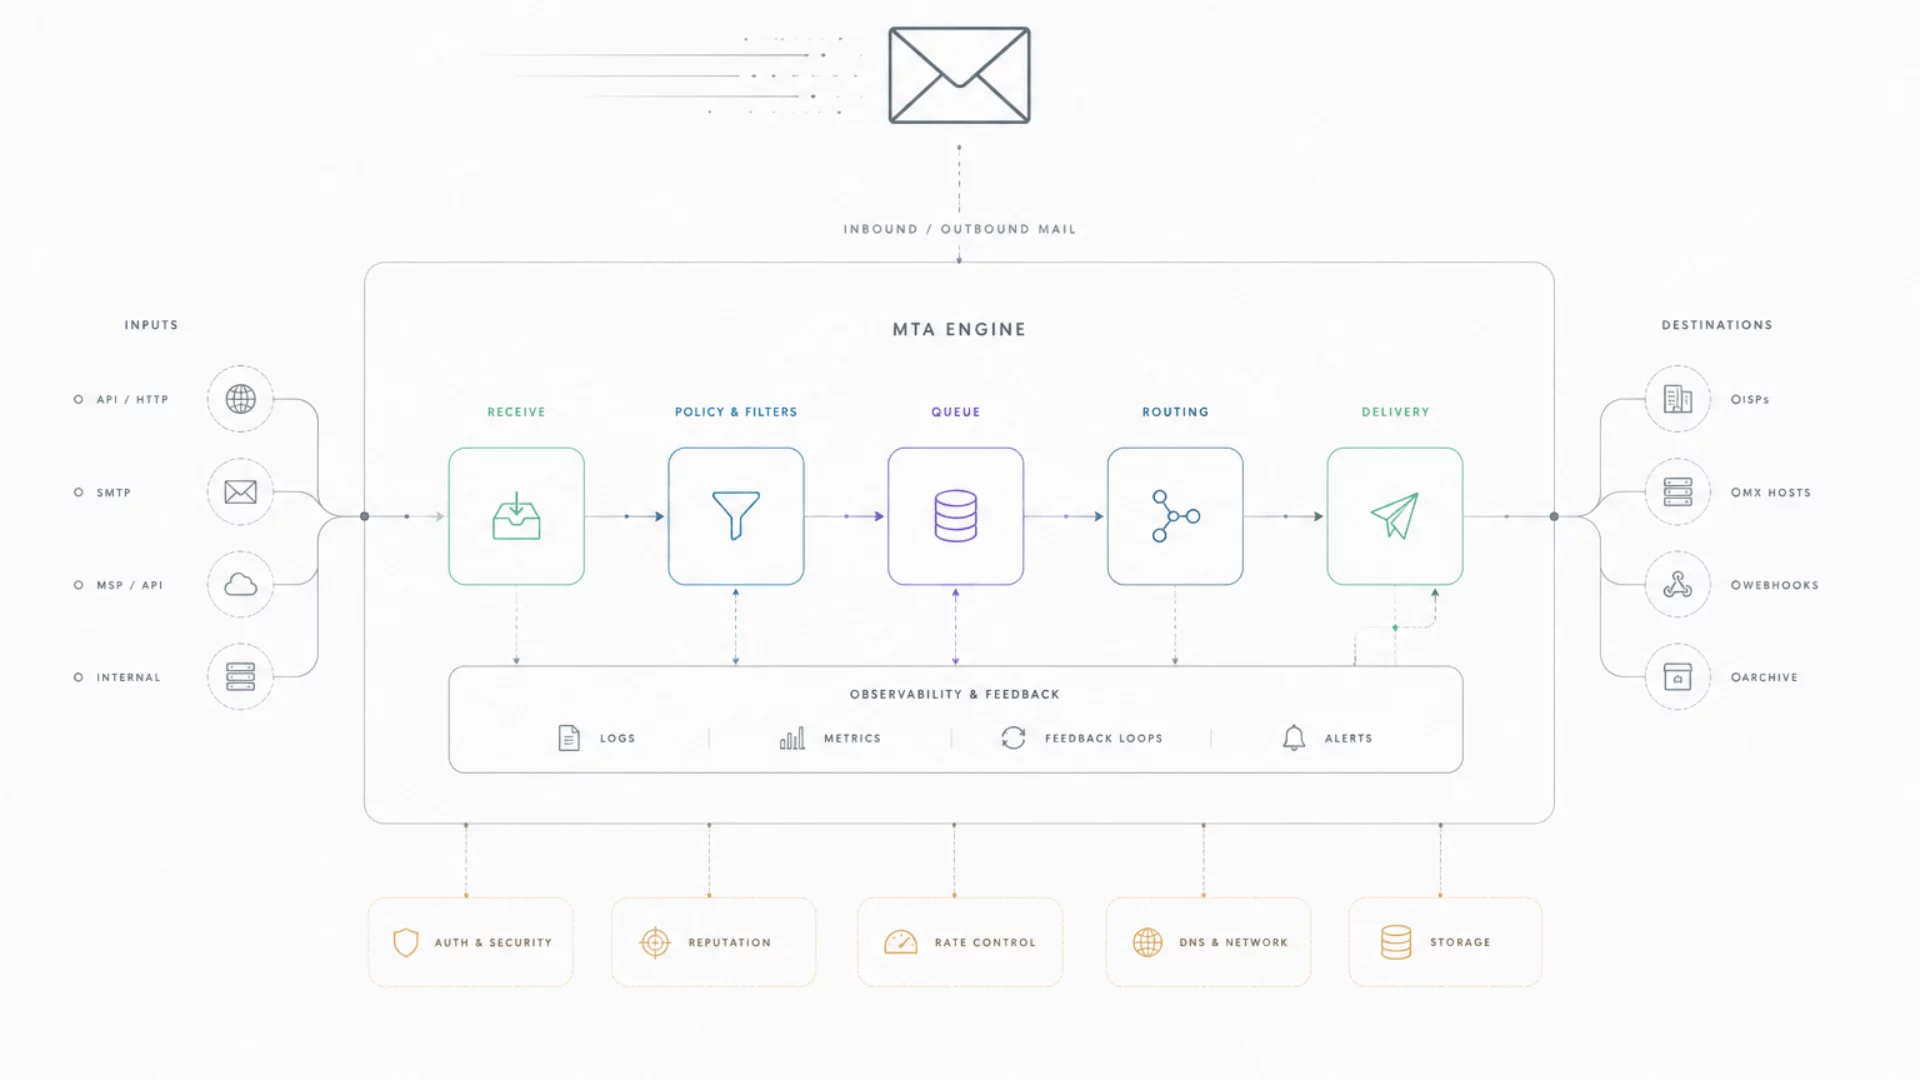
Capturing an opt-out preference on a front-end mobile app or a website preference center is deceptively simple. However, this case proves that collecting the data is only half the battle. That suppression signal must travel reliably and instantaneously across the entire enterprise technology stack—reaching CRM platforms, email marketing software, mobile push notification servers, automated call-center scripts, and third-party advertising integrations. If a preference center says "no" while a downstream marketing tool still says "yes," the organization has failed to deliver a legally compliant opt-out.
2. Suppression Data is Operational Data
Companies often treat privacy preferences—such as consent logs and suppression lists—as passive compliance archives. The Garante’s ruling reframes these metrics as high-priority operational data. If consent and suppression data cannot move reliably across complex enterprise tech stacks, the resulting compliance failure will quickly cascade out of the preference center and onto the desk of corporate legal counsel.
3. Frontline Personnel Are the Front Line of Defense
The BBVA case underscores the immense risk posed by inadequately trained customer service teams. When a consumer contacts support to report that privacy controls are failing, frontline agents represent the final safety net. Telling a customer to "ignore" unwanted marketing notifications is not just poor customer service; it is a clear operational failure that signals a systemic disregard for data protection rights to regulators.
Conclusion
As data privacy regulators across Europe continue to mature in their enforcement strategies, cases like Garante v. BBVA demonstrate that theoretical compliance policies on paper are no longer enough. Regulators are increasingly scrutinizing the messy, behind-the-scenes engineering realities of how customer data flows—or fails to flow—within corporate databases. For financial institutions and consumer brands alike, the message from Rome is clear: streamline your tech stack, train your people, and ensure that when a customer says "stop," the entire enterprise listens.