Global Release Marks a Strategic Evolution in How Organizations Handle Third-Party Sending Sprawl, DNS Drift, and Brand Impersonation.
Executive Summary & Main Facts
In a significant strategic pivot for the email security sector, EasyDMARC formally announced the release of version 3.0 of its platform on September 23. Alongside the major version update comes a comprehensive rebranding: the company is shedding its identity as a pure-play DMARC reporting tool and is positioning itself globally as an Email Trust Platform.
While foundational protocols—DomainKeys Identified Mail (DKIM), Sender Policy Framework (SPF), and Domain-based Message Authentication, Reporting, and Conformance (DMARC)—remain at the core of the architecture, version 3.0 expands outwards. It integrates these standards with four distinct operational modules: Authentication, DNS Manager, Sender Insights, and Threat Intelligence. Together, this quartet of features is engineered to offer continuous oversight of global authentication postures, rapid DNS changes, shifting sender behaviors, domain reputations, and active threat vectors, including sophisticated lookalike domain spoofing.
Underpinning these modules is a newly introduced agentic intelligence layer. This layer correlates data points across disparate operational siloes, mapping configuration changes in DNS records directly to downstream authentication failures, and intelligently prioritizing issues based on actual business risk.
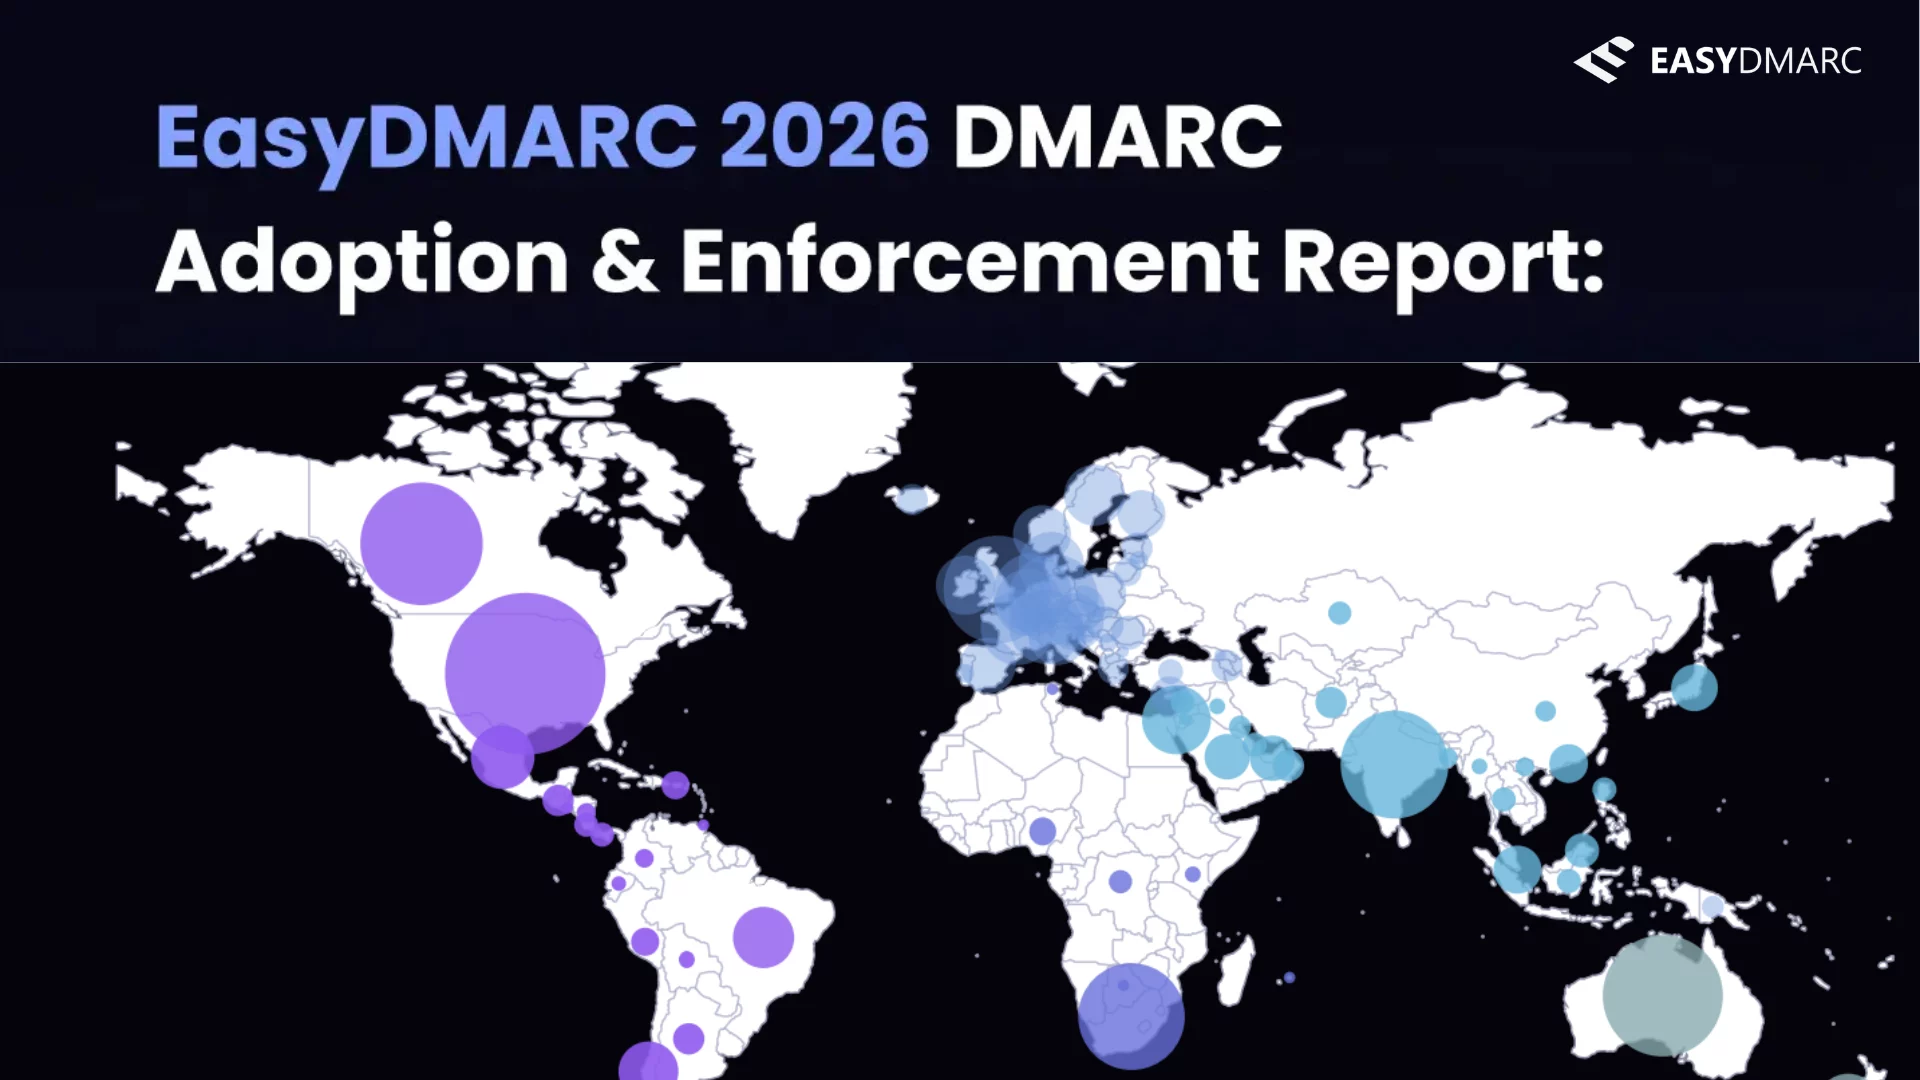
Serving over 90,000 organizations spanning more than 130 countries, EasyDMARC’s V3 release addresses a modern enterprise nightmare: shadow IT, fragmented communication stacks, and the operational exhaustion of maintaining corporate email hygiene across decentralized corporate departments.
Chronology of the Release and Strategic Evolution
To understand the weight of EasyDMARC V3, it is useful to contextualize the historical trajectory of email authentication and the company’s own journey through the cybersecurity landscape.
The Rise and Stall of Traditional DMARC
When DMARC was introduced as an RFC standard in 2015, it was hailed as a watershed moment for combating domain spoofing and phishing. Organizations rushed to implement DMARC policies (p=none, moving gradually to p=quarantine, and ultimately aiming for the gold standard of p=reject). However, cybersecurity practitioners quickly discovered a harsh reality: achieving p=reject is not a permanent state; it is a moving target.
As enterprises grew, marketing departments adopted new customer success platforms, finance automated invoicing through third-party vendors, and product teams integrated automated transactional email engines. Without centralized oversight, DNS records fractured. Authentication broke quietly, leaving IT teams scrambling to troubleshoot complex XML reports that defied easy interpretation.
EasyDMARC’s Iterative Growth
- Phase 1 (The Compliance Tool): EasyDMARC originally entered the market as a reliable engine for parsing DMARC XML reports, giving IT administrators visibility into who was sending email on behalf of their domains.
- Phase 2 (The Remediation Era): Recognizing that visibility alone was insufficient, the company expanded into wizard-driven setups, monitoring alerts, and rudimentary DNS record tracking to help companies bridge the gap from passive monitoring to active enforcement.
- Phase 3 (The Email Trust Platform – September 23): With version 3.0, EasyDMARC synthesizes these disparate needs into a unified ecosystem. By bundling authentication oversight with proactive DNS tracking, sender behavioral analysis, and threat intelligence into a single pane of glass, the company is redefining how organizations think about inbound and outbound email integrity.
Supporting Data and Platform Architecture
The architecture of EasyDMARC V3 is deliberately structured around four core modules supported by an overarching intelligence layer. The company describes this product design using a traditional enterprise triptych: a system of record, a system of intelligence, and a system of action.
[ EasyDMARC V3 Platform Architecture ]
 ├── System of Record        --> Core Protocols: SPF, DKIM, DMARC
 ├── System of Intelligence  --> Four Modules:
 │                             - Authentication
 │                             - DNS Manager
 │                             - Sender Insights
 │                             - Threat Intelligence
 └── System of Action        --> Agentic Intelligence Layer (Correlation & Prioritization)
1. The Four Operational Modules
- Authentication Module: Maintains real-time status visibility over SPF, DKIM, and DMARC posture across all corporate domains, ensuring that organizational sending pipelines remain compliant with major mailbox providers like Google and Yahoo.
- DNS Manager: Monitors DNS infrastructure for unvouched changes, tracking records that directly impact mail flow. This module bridges the traditional gap between network administrators and email operations teams.
- Sender Insights: Evaluates the behavioral patterns of outbound mail streams. It provides visibility into sending volumes, IP reputation shifts, and third-party vendor activity, helping organizations identify unauthorized services using their infrastructure.
- Threat Intelligence: Proactively scans the broader digital ecosystem for threats directed at customer domains, focusing heavily on lookalike domain creation, typo-squatting, and targeted phishing campaigns designed to spoof corporate brands.
2. The Agentic Intelligence Layer
Perhaps the most notable technical addition in V3 is the deployment of an agentic intelligence layer. In modern enterprise environments, email failures rarely happen in a vacuum. A marketing specialist might update a SendGrid or Mailchimp subdomain record on a Friday afternoon without updating internal documentation. By Monday morning, customer invoices are bouncing, and support tickets are piling up.
The agentic layer sits above the four modules, continuously monitoring inputs and outputs. If a DNS record changes, the engine automatically checks whether that modification breaks an existing DKIM selector or compromises an SPF alignment. Crucially, the system ranks these anomalies, separating critical mail-halting failures from low-priority informational alerts.
Official Responses and Industry Perspectives
The announcement of EasyDMARC V3 has drawn commentary from company executives, industry analysts, and cybersecurity practitioners alike.
Leadership Vision
Gerasim Hovhannisyan, CEO and co-founder of EasyDMARC, framed the release around the changing nature of corporate infrastructure.
"DMARC solved a critical piece of email security," Hovhannisyan noted. "However, as businesses decentralize and distribute their operations across dozens of third-party SaaS providers, running email securely has evolved from a one-time project into a permanent operational job."
Hovhannisyan emphasized that version 3.0 is designed to lift the administrative burden off IT teams who are constantly forced to investigate email delivery failures originating from systems they neither purchased nor directly control.
Practitioner and Analyst Reception
Industry observers have welcomed the evolution, noting that security tooling must adapt to the reality of modern enterprise shadow IT. Publications such as Expert Insights and ChannelVision highlighted the platform’s focus on agentic automation as a timely response to alert fatigue among cybersecurity professionals.
Security engineers point out that while achieving a p=reject DMARC policy is a major milestone for any organization, maintaining that policy requires constant vigilance. Authentication, DNS management, deliverability, and threat defense are fundamentally aspects of the exact same underlying problem: trust.
However, industry analysts stress that the ultimate success of EasyDMARC’s new AI-driven agentic layer will not be measured by its marketing terminology, but by its practical utility. Specifically, it must translate complex authentication failures into clear, plain-language explanations that can be swiftly acted upon by the exact staff member—technical or non-technical—who caused the configuration drift in the first place.
Enterprise Implications: Why "Email Trust" Matters Now
The transition from a DMARC reporting tool to an Email Trust Platform carries broad implications for enterprise risk management, compliance, and brand equity.
1. The Proliferation of Third-Party SaaS Risk
Modern organizations rarely send all their emails from an on-premises Microsoft Exchange or Google Workspace server. Instead, a typical mid-to-large enterprise utilizes:
- CRM & Marketing Automation: HubSpot, Salesforce, Marketo, Mailchimp.
- Customer Support: Zendesk, Intercom, Freshdesk.
- Financial Operations: Stripe, QuickBooks, Workday.
- HR & Recruiting: Workday, Greenhouse, Lever.
Each of these third-party platforms requires DNS integration (SPF includes, DKIM CNAME records, and custom return-paths) to send emails that look like they originate legitimately from the corporate domain. This decentralized management creates a fertile ground for human error. When a vendor updates their infrastructure requirements, corporate DNS records must be updated in lockstep. Failure to do so results in broken communication pipelines, missed revenue, and damaged customer trust.
2. The Escalation of Phishing and Business Email Compromise (BEC)
Cybercriminals continually refine their tactics, shifting away from sloppy, easily detectable phishing templates toward highly targeted lookalike domain attacks. By registering domains that mimic corporate entities (using homoglyphs, subtle typos, or deceptive TLDs), threat actors launch convincing Business Email Compromise campaigns targeting supply chains, financial departments, and unwary consumers.
An Email Trust Platform attempts to counter this by moving past reactive defense. By combining internal authentication posture monitoring with external threat intelligence scanning, organizations gain a holistic shield against both accidental self-sabotage (misconfigurations) and malicious external actors (domain spoofing).
3. Compliance and Regulatory Pressures
Major email service providers (ESPs) such as Google and Yahoo have tightened their bulk-sender requirements, making robust DMARC, SPF, and DKIM enforcement mandatory rather than optional. Organizations that fail to meet these thresholds face immediate deliverability penalties, with legitimate customer communications routinely dumped into spam folders or rejected outright. In this environment, continuous email trust monitoring ceases to be a luxury checkbox and becomes a core requirement for business continuity.
Conclusion
EasyDMARC’s launch of version 3.0 reflects a maturing market. As email infrastructure grows increasingly complex and threat actors leverage sophisticated impersonation techniques, standalone compliance reporting is no longer sufficient. By unifying authentication, DNS management, sender behavioral insights, and threat intelligence under an agentic intelligence layer, EasyDMARC is redefining what organizations should expect from their email security stack.
For the 90,000+ organizations currently utilizing the platform across more than 130 countries, V3 promises relief from the perpetual cycle of configuration drift and alert fatigue. Whether the platform’s new intelligence layer delivers on its operational promises will ultimately be decided in the trenches—by IT administrators and security analysts tasked with keeping corporate communication channels secure, compliant, and open.