Main Facts
On September 4, 2026, a significant email delivery disruption impacted Microsoft Exchange Online users worldwide, throwing corporate communications into brief disarray. The incident, officially tracked and cataloged by Microsoft as EX1467029, was triggered by the enforcement of an overly aggressive anti-spam model. This automated security misconfiguration directly targeted external message traffic, resulting in frustrating delivery bottlenecks, prolonged message delays, and intermittent error notifications for organizations relying on the cloud-based productivity suite.
Public extracts of Microsoft’s internal service-health record indicate that the disruption spanned a six-hour and fifteen-minute window, active globally between 09:00 and 15:15 UTC. During this timeframe, a substantial subset of Exchange Online users experienced notable friction when attempting to transmit or receive electronic mail involving external domains. Rather than delivering messages seamlessly to destination inboxes, the email transport pipeline began rejecting or deferring inbound and outbound traffic, showering mail administrators with recurring "Server busy" notifications across multiple enterprise mailboxes.
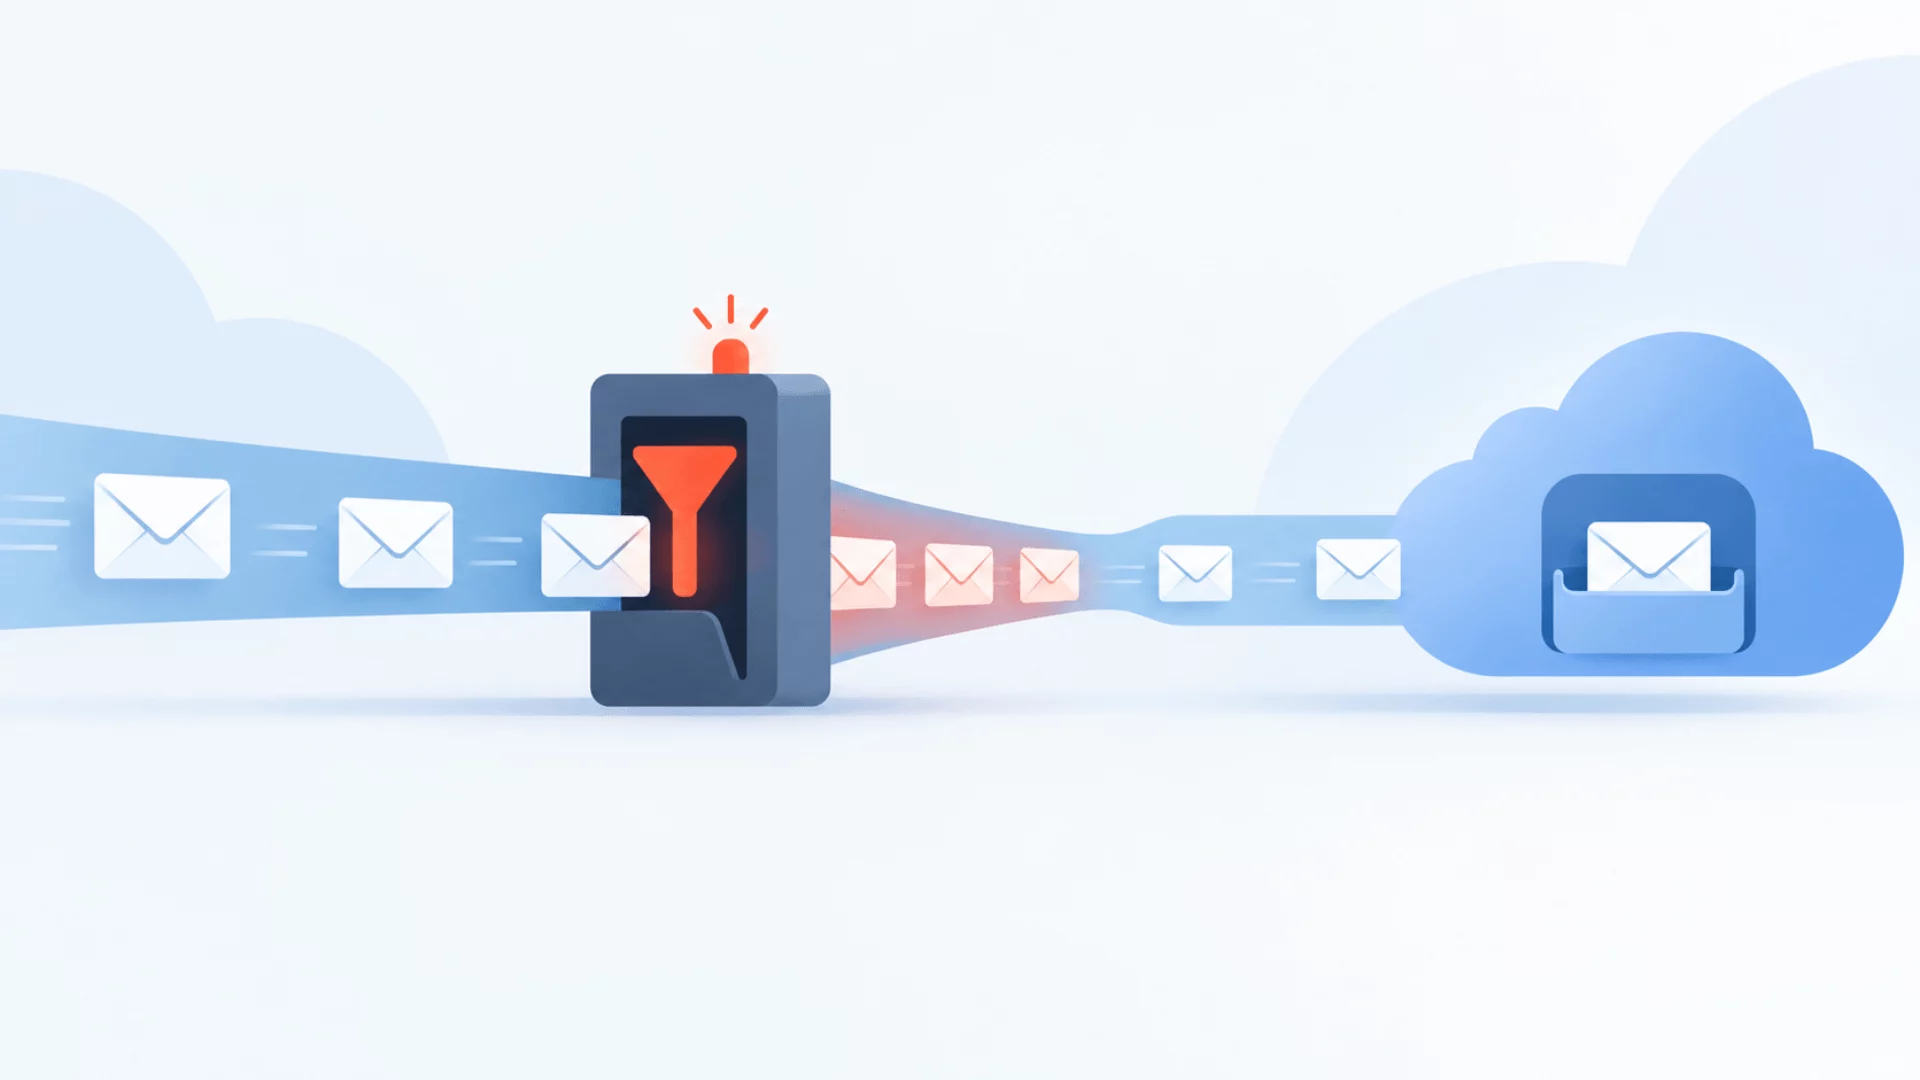
The core mechanism behind the disruption was traced to a newly enforced anti-spam security model designed to intercept malicious payloads. However, the model’s classification thresholds malfunctioned, misinterpreting legitimate, routine external correspondence as suspicious traffic. As mail servers across the globe attempted to negotiate handshakes with Microsoft’s Exchange Online Protection (EOP) infrastructure—primarily operating through the protection.outlook.com gateway—they were met with temporary SMTP deferrals carrying the exact status code:
451 4.7.500 Server busy
Under the governing standards of Internet mail architecture defined in RFC 5321 (Section 4.2.1), a 4yz SMTP response code represents a transient or temporary failure. Unlike permanent 5yz delivery rejections (which typically bounce messages back to the sender immediately), a 451 code signals that the receiving server is temporarily unable to process the transaction, instructing the originating SMTP client to hold the message in its local queue and periodically retry transmission. While this mechanism prevents data loss during legitimate network outages, the sheer volume of deferred messages during the September 4 incident created massive processing backlogs. Senders witnessed prolonged outbox wait times, while receiving organizations faced erratic message delivery schedules that crippled time-sensitive corporate workflows.
Chronology of the Incident
Reconstructing the timeline of incident EX1467029 reveals a cascading technical failure that required multiple layers of intervention by Microsoft’s engineering teams to fully remediate.
Phase 1: Onset and Initial Impact (09:00 UTC)
At approximately 09:00 UTC, Microsoft’s automated security infrastructure enforced a newly updated anti-spam evaluation model across its global Exchange Online clusters. Almost immediately, external mail routing nodes began encountering unexpected bottlenecks. Senders utilizing enterprise email platforms and independent mail servers started reporting sudden delivery deferrals.
Phase 2: Public Detection and Third-Party Reports (09:30 – 11:30 UTC)
As the disruption widened, independent monitoring services and enterprise communication platforms began noticing anomalous patterns. At 10:15 UTC, communications technology provider Poppulo publicly flagged a sharp, abnormal increase in mail deferrals for traffic routed through protection.outlook.com. Concurrently, system administrators participating in the high-profile Mailop mailing list began sharing notes regarding sudden spikes in delivery failures, isolating identical error suffixes (S77714, S77717, and S77719) attached to the standard 451 4.7.500 Server busy response.
Phase 3: Microsoft Triage and Initial Mitigation (11:30 – 13:30 UTC)
Microsoft’s incident response teams acknowledged telemetry showing abnormal transport-layer queues and initiated diagnostic procedures. Recognizing that the newly deployed anti-spam model was throttling legitimate traffic, engineers began executing emergency remediation steps. As an immediate stopgap measure to restore mail flow, Microsoft began adding affected external sending IP addresses to a temporary global allow-list while simultaneously initiating the complex process of disabling the faulty anti-spam model.
Phase 4: Secondary Throttling Discoveries and Final Recovery (13:30 – 15:15 UTC)
Although disabling the primary anti-spam model alleviated the vast majority of delivery bottlenecks, telemetry indicated that residual throttling was still occurring. Upon deeper investigation, Microsoft engineers uncovered a secondary, underlying machine-level throttling rule embedded deep within their anti-spam architecture. This legacy rule continued to restrict a small, residual subset of external messages. Microsoft quickly disabled this secondary rule and entered an extended monitoring phase. By 15:15 UTC, telemetry confirmed that message delivery queues had stabilized to normal operational parameters, prompting Microsoft to formally mark the incident as resolved.
Supporting Data and Technical Analysis
A deep dive into the technical fingerprints of incident EX1467029 offers valuable insights into how cloud-scale email filtering systems can occasionally backfire against the very users they are engineered to protect.
The Anatomy of the SMTP 451 Error
The disruption was communicated primarily via the 451 4.7.500 Server busy SMTP reply. To understand the operational impact on corporate mail servers, it is essential to examine the technical definition provided by the Internet Engineering Task Force (IETF) in RFC 5321:
- The "4" Class (Transient Negative Completion Reply): The command was not accepted, but the error condition is temporary. The sending client is explicitly encouraged to re-attempt the command at a later time.
- The "5" Sub-class (Mail System Status): Indicates a persistent or transient status issue relating to the receiving mail system’s operational readiness.
- The "500" Detail Code: Points directly to a server-side capacity or policy constraint (in this case, triggered defensively by an overly restrictive anti-spam classifier).
Third-Party Visibility and Diagnostic Evidence
The severity of the incident was independently verified across multiple enterprise touchpoints:
- Poppulo’s Infrastructure Status: Poppulo, a prominent enterprise employee communications platform, registered significant performance degradation logs. Their telemetry highlighted abnormal deferral rates specifically bottlenecked at Microsoft’s gateway endpoints (
protection.outlook.com). - Mailop Operator Dispatches: Network and email administrators communicating via the Mailop listserv isolated specific tracking tags accompanying the
451errors. Suffix codesS77714,S77717, andS77719served as crucial diagnostic signatures, confirming that the rejections were originating from centralized Exchange Online Protection filtering layers rather than recipient-side mailbox rules. - Correlated Infrastructure Pressures: The disruption occurred against a backdrop of heightened scrutiny regarding cloud security filtering. Industry observers noted parallel telemetry trends, such as fluctuating block rates (ranging between 10% and 15%) observed across major third-party relay networks like SendGrid when communicating with Microsoft 365 environments during early September.
Official Responses and Post-Incident Accountability
Microsoft’s formal incident post-mortem communication highlighted the multi-layered complexity of modern cloud security systems. In its initial service-health advisories, the company explicitly pointed to the enforcement of a preliminary anti-spam model as the primary root cause of the widespread mail delays.
However, transparency advocates and enterprise IT administrators have scrutinized the speed and depth of Microsoft’s documentation. According to independent checks conducted by industry analysis publication emailexpert on September 10—six days after the initial outage—the public service health record for incident EX1467029 had still not been updated with the comprehensive Post-Incident Report (PIR) that Microsoft traditionally promises following high-severity availability events.
In preliminary statements released to enterprise tenants, Microsoft outlined a multi-pronged internal review aimed at preventing recurrence. The corrective action plan includes:
- Model Classification Audits: A thorough re-evaluation of how machine learning models score and classify external sender reputation metrics.
- Rule Configuration Overhauls: Implementing stricter validation gates for automated security rules to ensure secondary machine-level throttling mechanisms cannot activate independently of primary safety checks.
- Upstream Data Pipeline Refinements: Enhancing the telemetry loops that feed threat intelligence data into real-time filtering layers, minimizing the risk of false positives during routine security model updates.
Despite these assurances, enterprise messaging teams continue to demand greater real-time transparency and tighter safety margins when automated AI and machine learning models are deployed directly into core messaging transport pipelines.
Broader Implications for Enterprise Email Operations
The Exchange Online incident of September 4, 2026, serves as a timely cautionary tale for the modern enterprise ecosystem, highlighting several critical lessons regarding cloud dependency, email resilience, and security automation.
1. The Perils of Over-Automation in Security Filtering
As sophisticated threat actors deploy automated phishing kits and zero-day malware at unprecedented scale, cloud providers like Microsoft have become heavily reliant on advanced machine learning models and artificial intelligence to filter traffic at line-speed. However, incident EX1467029 demonstrates the inherent fragility of these systems. When an autonomous security model suffers from a classification bias or misinterprets baseline traffic parameters, it can inadvertently act as a self-inflicted Denial of Service (DoS) attack, halting legitimate business operations faster than any external threat actor could.
2. The Critical Importance of Mail Queue Resilience
For small-to-medium enterprises and large multinational corporations alike, the incident underscored the necessity of robust on-premises and secondary relay mail queue management. Because RFC 5321 mandates that a 451 error must be treated as a temporary failure, properly configured mail transfer agents (MTAs)—such as Postfix, Exim, or Exchange Server hybrids—automatically queued outbound messages. Organizations with poorly provisioned local mail queues, however, risked dropping messages entirely or experiencing massive administrative overhead as queues filled to capacity.
3. Vendor Transparency and Cloud Accountability
The delay in publishing Microsoft’s comprehensive Post-Incident Report touches on a broader friction point within the Software-as-a-Service (SaaS) industry: the tension between proprietary cloud architecture and enterprise operational transparency. When mission-critical infrastructure like Microsoft 365 experiences availability or performance degradation, downstream IT departments require instantaneous, deeply granular technical data to assure their internal stakeholders and regulatory compliance boards. Moving forward, cloud service providers will face mounting pressure to accelerate their root-cause disclosures and provide granular diagnostic tooling to help administrators independently isolate gateway-level filtering anomalies.
Ultimately, incident EX1467029 stands as a stark reminder that in an era of hyper-automated cloud security, the boundary between blocking malicious email and inadvertently blocking business-critical communication remains razor-thin.