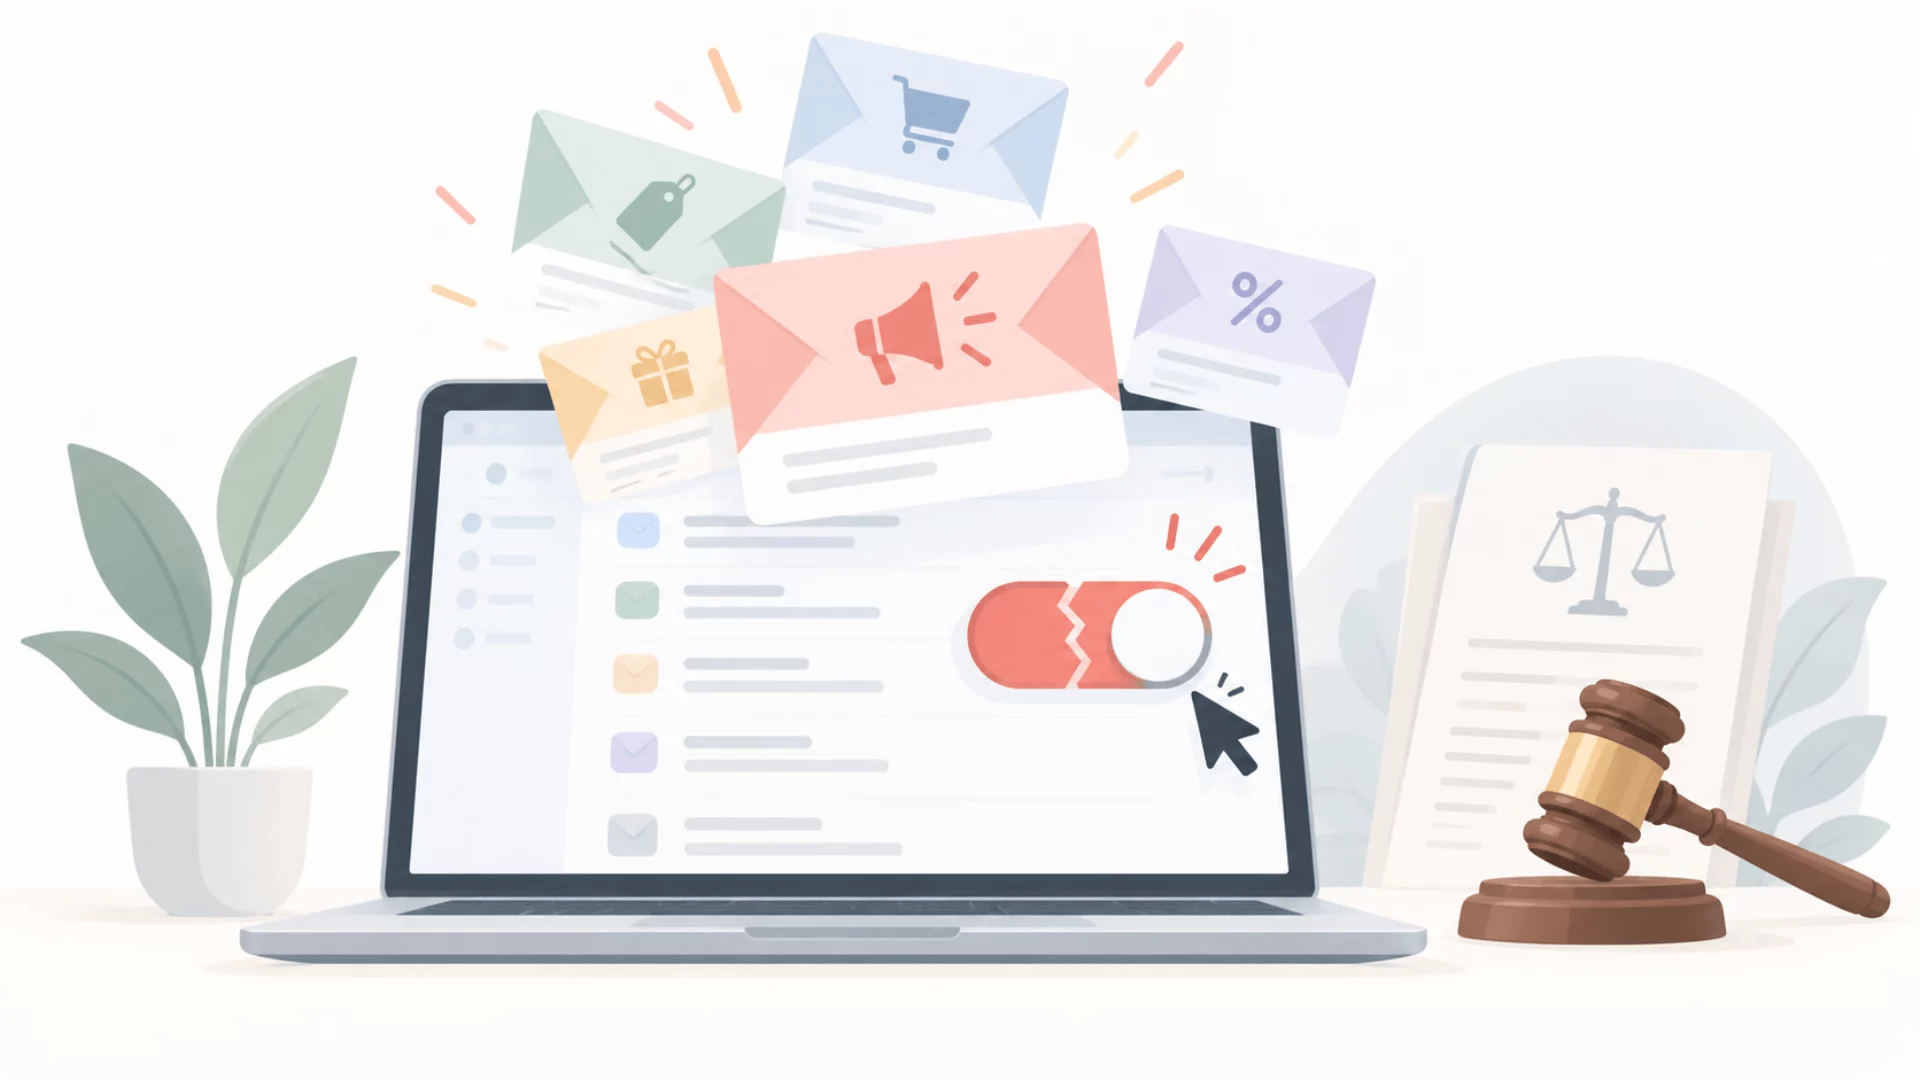
BRUSSELS / AMSTERDAM / WIESBADEN — For years, the automated abandoned cart email has been treated as a fundamental building block of modern digital retail. A prospective customer browses an online store, selects a few items, adds them to their digital shopping basket, and leaves the site before completing the transaction. Minutes or hours later, a friendly reminder drops into their inbox, often accompanied by a small discount code to incentivize completion.
To digital marketers, it is a standard retention and conversion tool. To European data protection regulators, however, it is increasingly viewed as an unlawful, invasive form of unsolicited direct marketing.
Recent legal clarifications from Dutch legal experts at ICTRecht and formal enforcement stances from data protection authorities in Germany have re-ignited a debate that many e-commerce teams thought was settled years ago. The consensus, grounded strictly in the European Union’s ePrivacy Directive and General Data Protection Regulation (GDPR), is unambiguous: you cannot email someone who abandoned their shopping cart unless you have prior, explicit consent or a pre-existing customer relationship.
As regulatory scrutiny intensifies and major email inbox providers crack down on spam complaints, the technical shortcuts and aggressive pre-submit data harvesting strategies relied upon by countless online retailers are facing an existential reckoning.
Main Facts: The Legal Reality of Abandoned Carts
At the heart of the issue is the legal classification of the abandoned cart email. Under EU law, specifically the ePrivacy Directive (transposed into national laws across member states), electronic mail sent for direct marketing purposes requires the prior consent of the recipient—the classic "opt-in" model.
There is, however, a narrow statutory exception known as the "soft opt-in." This exception allows companies to send direct marketing emails to existing customers regarding their own similar products or services, provided those customers were given a clear and free opportunity to object to such use at the time their contact details were collected.
According to data protection authorities and legal analysts, an abandoned shopping cart fails to meet these criteria on two foundational counts:
- Commercial Intent and Direct Marketing: A retargeting email sent to recover a lost sale is, by definition, commercial communication designed to promote goods or services. Consequently, it sits squarely behind the requirement for an explicit opt-in.
- The Absence of a Customer Relationship: The soft opt-in exception explicitly requires a completed purchase and a connection to a similar product. When a prospective buyer walks away from a checkout before finalizing the transaction, no sales contract has been concluded, and no legal customer relationship has been established.
Furthermore, recent jurisprudence from the Court of Justice of the European Union (CJEU)—such as the Inteligo Media ruling handed down in November—has helped clarify the boundaries of data acquisition. The CJEU held that free account registrations can sometimes count as obtaining details in the context of a sale, allowing freemium publishers to rely on the soft opt-in for newsletters without money changing hands. Crucially, however, this mechanism still requires a completed registration that the user actively executed. An uncompleted, abandoned checkout bears no legal resemblance to a finished registration.
Chronology: How the Regulatory Noose Tightened
The collision between aggressive e-commerce marketing tactics and European privacy law has evolved through a distinct timeline of regulatory warnings, compliance reports, and court rulings.
- May 2018 (GDPR Implementation): When the General Data Protection Regulation took full effect across the European Economic Area (EEA), businesses rushed to update their privacy policies and cookie banners. While explicit consent became the gold standard for tracking cookies, many e-commerce brands assumed that transactional telemetry—such as capturing email addresses typed into multi-step checkout fields—remained exempt from strict direct marketing rules.
- November 2023 (The Inteligo Media Judgment): The CJEU issued a pivotal ruling on direct marketing rules under the ePrivacy Directive. While the court provided breathing room for digital publishers operating freemium models by validating free account sign-ups as a basis for soft opt-ins, it simultaneously reinforced the principle that lawful contact details must be deliberately and actively surrendered by the user within a completed process.
- Throughout 2024 (The Hessian Data Protection Authority Report): The debate shifted from theoretical compliance to active enforcement when the Hessian data protection authority in Germany published its 2024 activity report. The authority spotlighted abandoned shopping cart emails following a wave of consumer complaints from webshop visitors who had items in their carts, never finalized a purchase, and subsequently received unrequested marketing follow-ups. The Hessian DPA declared the practice illegal without a prior opt-in, establishing a precedent that other regional European authorities are rapidly adopting.
- September 16, Scholarly and Legal Consensus: Dutch legal tech publisher ICTRecht published a comprehensive analysis revisiting the question of cart recovery emails. Their findings cut through industry denial, confirming that sending automated recovery pings to non-consenting users violates European e-privacy rules—a stance that immediately reverberated across digital marketing circles in the Benelux region and beyond.
Supporting Data: The Technical Breakdown and Compliance Failures
For most online retailers, the legal friction is compounded by a profound disconnect between legal requirements and technical implementation.
The Broken Opt-In Checkbox
Much of the mainstream marketing coverage surrounding EU privacy compliance advises retailers simply to "add a checkbox" to their checkout pages. Because of this advice, checkboxes are now ubiquitous across European e-commerce sites. However, the mere presence of a checkbox does not guarantee legal compliance; the underlying data pipeline must respect the user’s choice.
Consider platforms like Shopify. The platform’s native checkout includes a marketing consent checkbox. The resulting abandoned checkout record—accessible via administrative APIs—includes a specific boolean data point: buyer_accepts_marketing.
In many cases, this value evaluates to false because the user either left it unchecked or explicitly declined. Yet, the raw abandoned checkout record remains accessible within the system dashboard regardless of that boolean value. When third-party marketing automation platforms—such as Klaviyo, Omnisend, or custom CRM integrations—pull these records to trigger recovery flows, they frequently fail to parse or respect the buyer_accepts_marketing flag. Consequently, automated emails are blasted out to individuals who legally withheld their consent.
The Dangers of Pre-Submit Data Capture
An even more aggressive technical vector involves "pre-submit identity resolution" tags. Offered by specialized vendor networks, these scripts leverage advanced tracking to read the email address field on "blur"—meaning the exact moment a user clicks away from or finishes typing their email address into a form field, before they ever hit the final submit button.
This is how vendors claim they can recover carts that retailers previously had no record of: they harvest the data mid-stroke.
From an EEA regulatory standpoint, this practice is indefensible. The user never handed over their data for marketing purposes; they merely typed it into a provisional form field during an abandoned session. Under the GDPR, there is no lawful basis for processing data harvested in this manner. Curiously, even the product descriptions and technical documentation of some identity resolution vendors implicitly acknowledge these limitations—if a compliance officer reads the fine print carefully enough.
Official Responses and Industry Repercussions
Data protection authorities across the EU are facing mounting pressure from consumer protection organizations to transition from educational warnings to punitive enforcement.
German regulators have taken an early lead, signaling that online shops utilizing automated retargeting without explicit opt-ins face potential audits and administrative fines under both the GDPR and national telecommunications privacy laws. Regulators in France (CNIL) and the Netherlands (AP) are reportedly monitoring similar patterns of consumer grievances.
Meanwhile, the email ecosystem itself is imposing strict operational penalties on non-compliant senders. Major inbox providers, most notably Google and Yahoo, implemented stringent bulk-sender requirements designed to protect users from unwanted clutter. Under these rules, domain-level spam complaint rates must remain strictly below 0.3%, with an ideal threshold of under 0.1%.
This technical enforcement mechanism creates a compounding crisis for e-commerce operators:
- Cart recovery emails are typically sent from the exact same primary sending domain used for mission-critical transactional notifications, such as order confirmations, shipping updates, and password resets.
- Because abandoned cart emails sent without consent are perceived by recipients as unsolicited spam, they generate exceptionally high rates of user complaints (i.e., users clicking the "Report Spam" button).
- High spam complaint rates tank the sender reputation of the primary domain, causing vital transactional emails to miss the inbox entirely and land in the spam folder, crippling normal business operations.
Implications for E-Commerce Strategy
The legal and technical realities surrounding abandoned cart emails demand an immediate strategic overhaul for digital marketing and e-commerce development teams operating within or targeting the European Economic Area.
- Audit Data Pipelines Immediately: Retailers must audit how customer data flows from checkout interfaces to marketing automation platforms. It is no longer sufficient to merely have a consent checkbox; technical safeguards must be enforced to ensure that records where
buyer_accepts_marketingis false are completely quarantined from automated marketing sequences. - Abandon Pre-Submit Harvesting: Any reliance on identity resolution scripts that harvest email addresses prior to explicit form submission must be dismantled. The short-term lift in recovered revenue cannot justify the immense regulatory liability and potential GDPR fines.
- Redefine the Conversion Funnel: E-commerce teams must pivot toward permission-first acquisition models. This includes incentivizing account creation or newsletter sign-ups earlier in the browsing journey—such as offering a discount for signing up prior to adding items to the cart—thereby securing valid, documented opt-ins before the user ever reaches the checkout phase.
- Isolate Sending Infrastructure: Brands that continue to experiment with aggressive retention strategies must separate their marketing sending domains from their transactional sending infrastructure. A spike in cart-recovery spam complaints must not be allowed to compromise the delivery of order confirmations and shipping notices.
The era of frictionless, aggressive cart-recovery marketing in Europe is drawing to a close. As data protection authorities align their enforcement actions with statutory privacy frameworks, e-commerce brands must choose between respecting user consent or facing severe regulatory penalties and catastrophic inbox deliverability failures.