BALI — The ongoing evolution of internet governance and domain security took center stage last week at ICANN87, where cybersecurity researchers, registry operators, and anti-abuse experts convened to address a fundamental limitation in modern threat mitigation. Building on discussions that began earlier this year regarding associated domain checks, the global internet community is increasingly shifting its focus away from reactive whack-a-mole tactics and toward the identification and neutralization of entire abusive domain portfolios.
However, as advanced telemetry and predictive analytics give defenders unprecedented visibility into upcoming cyber campaigns, a formidable roadblock remains: the friction between actionable threat intelligence and the stringent, evidence-based thresholds required to suspend infrastructure before a single victim is compromised.
Main Facts: The Shift Toward Portfolio-Level Detection
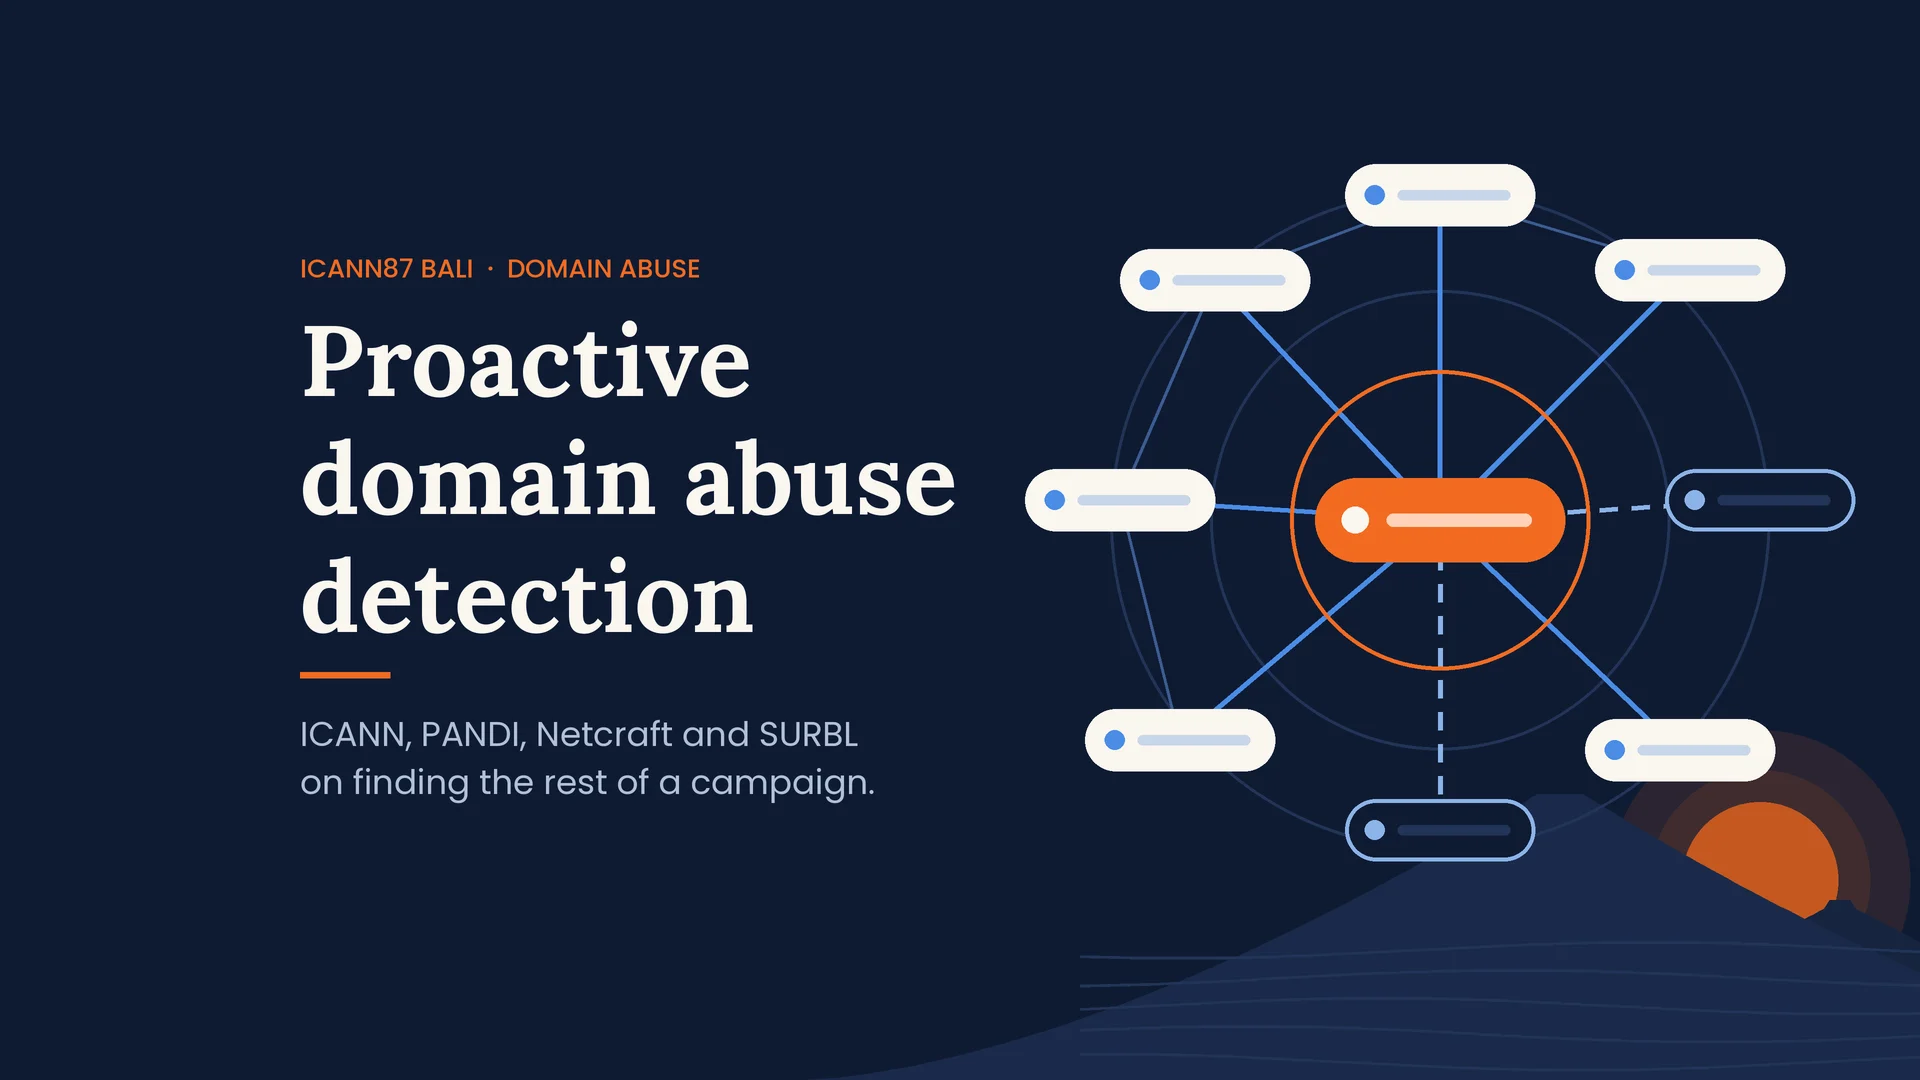
The central theme of the ICANN87 session, Approaches to Proactive Domain Abuse Detection at Scale, was clear: looking beyond the individual domain reported for abuse to investigate what else is connected to it. The panel featured a coalition of global experts, including representatives from ICANN, Indonesia’s .id registry PANDI, threat intelligence firm Netcraft, and the Spamhaus URL Blocklist project (SURBL).
For years, abuse desks have operated primarily on a transactional basis. A phishing page goes live, a user or security filter reports the specific URL, and an investigator requests a takedown. By the time the registrar processes the request, the damage has often been done.
Proactive domain portfolio detection changes this paradigm. By analyzing registration dates, shared nameservers, unique DNS patterns, and linguistic or structural similarities within domain names, researchers can map out an attacker’s infrastructure in advance. Rather than waiting for a malicious site to launch, security professionals are increasingly capable of connecting disparate dots to expose coordinated, multi-domain operations while they are still in the staging phase.
Chronology: From Early 2024 Theories to ICANN87 Realities
- June 2024: The cybersecurity community began broadly discussing ICANN’s expanding initiatives around associated domain checks. The concept focused on examining the broader ecosystem of an attacker rather than treating each reported URL as an isolated incident.
- October / November 2024 (ICANN87, Bali): The conversation matured from theoretical frameworks to empirical demonstrations. Researchers presented tangible case studies proving that domains can be flagged as malicious weeks before they actively host phishing content.
- Present Day: Industry stakeholders are grappling with the operational, legal, and ethical consequences of these findings. While the technology to predict attacks exists, the policy and evidentiary frameworks required to act on pre-emptive intelligence are lagging behind.
Supporting Data and Technical Realities: Inside the Threat Landscape
The technical presentations at ICANN87 highlighted both the sophistication of modern attackers and the clever methods researchers use to unmask them.
Predictive Identifiers and Staged Infrastructure
Sam Cheadle of ICANN walked attendees through the mechanics of discovering related domains. Attackers rarely register a single domain for a campaign; instead, they often procure batches of domains using automated scripts. While some threat actors make mistakes—registering dozens of domains simultaneously with sequential naming conventions and identical infrastructure—others are far more deliberate. Advanced groups spread registrations over weeks or months, weaving them seamlessly into background noise alongside legitimate domain registrations.
Despite these evasive maneuvers, Netcraft’s Luke Wood demonstrated that predictive identification is yielding real-world results. In one notable case study shared during the session, Netcraft identified a suspicious domain a full week before it hosted an active phishing attack.
However, Wood emphasized the critical need for methodological rigor. Investigators must account for shared hosting environments; millions of entirely unrelated websites share the same IP addresses, meaning shared hosting alone can never serve as definitive proof of malicious coordination. High-quality reports require multi-layered indicators, ensuring that registrars and registries receive data they can legally and technically investigate.
Phishing Kits and Zero-Hour Intelligence
Taking the technical analysis a step further, Raymond Dijkxhoorn of SURBL illustrated how researchers extract configuration data from captured phishing kits. By analyzing the backend code of these kits, analysts can frequently discover hardcoded lists of domains intended for subsequent campaigns.
Furthermore, by monitoring Certificate Transparency (CT) logs, security systems can track SSL/TLS certificate issuances for newly generated domains, connecting nascent infrastructure to known threat actors long before the attack web pages are populated.
Evasion Tactics: Traffic Distribution Systems and Cloaking
The session also addressed why traditional reactive methods so frequently fail. Attackers increasingly rely on Traffic Distribution Systems (TDS) and advanced cloaking techniques. When a victim clicks a malicious link disseminated via email, they are directed to the scam landing page. However, if a known security investigator or automated crawler clicks that exact same link, the TDS detects their digital footprint—analyzing location, browser characteristics, IP reputation, and behavioral signals—and redirects them to an entirely benign website.
This dynamic creates a frustrating loop for abuse handlers. An email security gateway flags a malicious message, but when an investigator follows up later, the landing page appears clean, or the DNS records have temporarily vanished, only to reappear when the campaign officially launches. Dijkxhoorn stressed that this does not invalidate the original report; rather, it underscores the immense value of preserving original message headers, timestamps, URLs, and recipient-side telemetry.
Official Responses and Perspectives
The Registry’s Burden: PANDI’s Operational Reality
Representing the registry perspective, Indonesia’s PANDI offered a sobering reminder of what happens after a domain is flagged. Managing a country-code Top-Level Domain (ccTLD) involves far more than generating a spreadsheet of bad actors.
PANDI’s workflow encompasses comprehensive intake of reports and signals, rigorous verification of evidence, formal notifications to relevant parties, execution of enforcement actions, and—crucially—mechanisms to reverse erroneous suspensions. PANDI also noted that its operations intersect with local Indonesian legal requirements, such as stringent national regulations targeting online gambling. Officials cautioned that these regional legal obligations must be distinguished from standard technical DNS abuse mitigation when evaluating global applicability.
The False Positive Dilemma
Throughout the session, open forum discussions and chat logs reflected a healthy degree of skepticism regarding automated portfolio takedowns. Legitimate corporate entities—particularly multinational brands engaging in defensive domain registration, global product launches, or digital asset protection—frequently register large batches of domains. Their portfolio footprints can look remarkably similar to the infrastructure staging of a cybercriminal syndicate.
Participants raised critical questions: What constitutes "bulk registration"? What level of evidence justifies pre-emptive intervention? And how quickly will threat actors adapt their registration patterns once defensive AI models become ubiquitous?
The stakes of getting this wrong are exceptionally high. Prematurely suspending a domain can inadvertently knock out a legitimate business website, disrupt critical email communications, or trigger severe collateral damage that outweighs the intended prevention.
Implications: The Pre-Emptive Paradox in Cybersecurity
The core dilemma emerging from ICANN87 can be summarized as the Pre-Emptive Paradox: If security researchers and threat intelligence analysts can definitively identify a cyberattack operation before it goes live, should the digital ecosystem be forced to wait for real-world victims to suffer losses before defensive action can be taken?
During the session, Dijkxhoorn shared harrowing examples from financial sector engagements, where individual campaign domains drained thousands of dollars from victims within minutes of going live. When minutes equate to catastrophic financial losses, the requirement to wait for an active, publicly accessible phishing screenshot feels agonizingly archaic to operational security teams.
Yet, abandoning evidentiary standards in favor of speed risks opening the floodgates to systemic abuse, censorship, and administrative chaos.
The Path Forward for Email Security and Infrastructure Disruption
For the email security and abuse prevention community, the takeaways from ICANN87 point toward a necessary evolution in strategy:
- Look Upstream: Stopping a single domain is an isolated victory; understanding the overarching operational infrastructure can neutralize the next hundred domains before they launch.
- Target the Core Systems: As Dijkxhoorn suggested, shifting focus toward disrupting Traffic Distribution Systems and shared infrastructural dependencies can yield a much wider suppressive effect than chasing individual landing pages.
- Elevate Evidence Sharing: Email telemetry provides unique visibility that traditional web crawling misses. By preserving and sharing recipient-side artifacts, headers, and contextual indicators, email defenders can help bridge the evidentiary gap that plagues registry abuse desks.
Ultimately, the cybersecurity industry stands at a technological crossroads. The capability to see the storm forming on the horizon is no longer in question. The challenge for ICANN, registries, registrars, and security researchers alike is building the collaborative trust and flexible frameworks required to weather that storm without tearing down the house in the process.