AMSTERDAM — In what legal experts are calling a watershed moment for European data privacy enforcement, a Dutch court has struck a definitive blow against the weaponization of the General Data Protection Regulation (GDPR). The District Court of Noord-Holland has dismissed a series of data access claims brought by a serial litigator against four prominent retailers, ruling that the legal maneuvers were not genuine exercises of privacy rights, but rather part of a calculated, industrialized scheme to extract financial settlements.
The late-July rulings—encompassing separate cases against retailers Suitable, Scapino, At Home, and interior design firms Wolters Wonen and Fundesign—mark the first time a Dutch court has applied the landmark European Court of Justice (CJEU) Brillen Rottler v TC judgment. By determining that even initial data access requests can be deemed "manifestly excessive" when weaponized for financial gain, the court has provided businesses with a potent shield against bad-faith compliance shakedowns while clarifying the boundaries of legitimate data subject rights.
Main Facts: Anatomy of a Compliance Shakedown
The mechanics of the operation were as systematic as they were predatory. According to legal analyses of the judgments by the tech-law firm ICTRecht, the applicant orchestrated a carbon-copy playbook across dozens of Dutch enterprises.
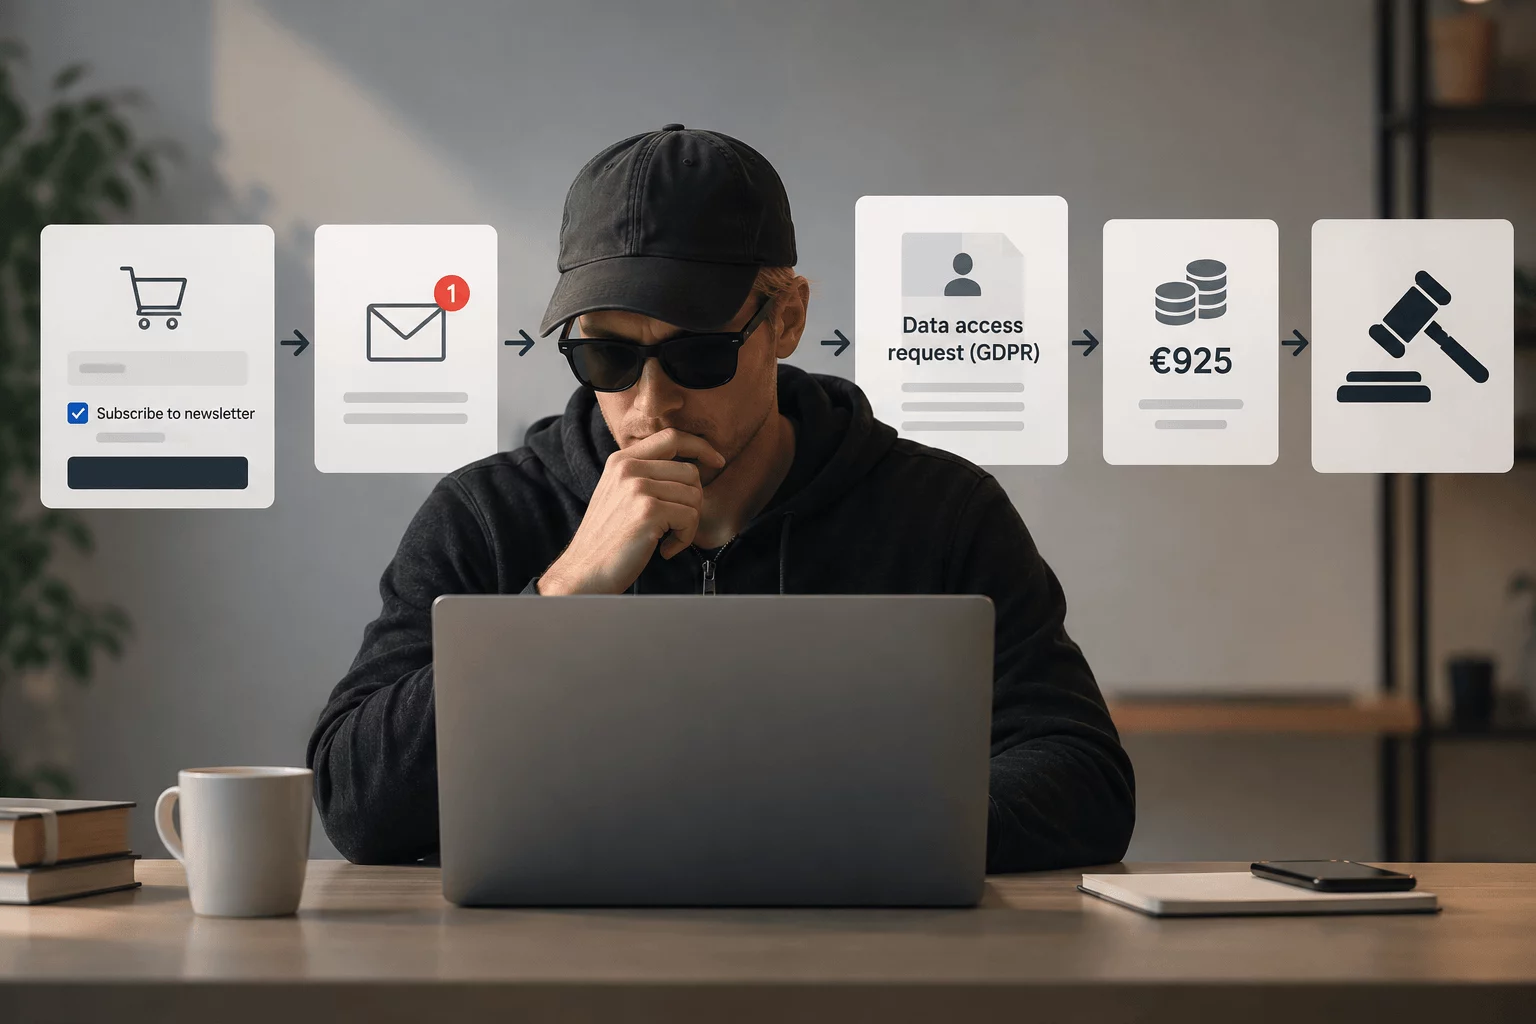
The strategy unfolded in tightly timed phases:
- The Catalyst: The applicant would execute a low-friction interaction with a target retailer’s digital ecosystem, typically by placing a modest online retail order or signing up for a promotional marketing newsletter to establish a baseline data footprint.
- The Access Demand: Shortly after completing the digital handshake, the individual would file a formal Article 15 GDPR Subject Access Request (SAR), demanding comprehensive details regarding the processing of their personal data.
- The Financial Squeeze: Within weeks of submitting the SAR, the narrative shifted abruptly from privacy to profit. The applicant—or representatives acting on his behalf—would issue a demand for €925 in purported extrajudicial costs.
- The Settlement Trap: This demand was swiftly followed by a formal settlement proposal delivered under the immediate threat of legal proceedings.
- The Judicial Bait-and-Switch: When cases proceeded to litigation, the summonses routinely demanded substantial statutory damages alongside legal costs. However, in a telling tactical pivot designed to evade scrutiny, the applicant would abruptly scale back his demands immediately prior to the court hearings, reducing the claim exclusively to a bare-bones request for data access—all while offering zero substantive explanation for the sudden shift.
During court proceedings, the scale of the operation was laid bare. The applicant openly admitted to filing approximately 90 distinct access requests over an 18-month window. At the time of the Noord-Holland hearings, roughly 20 of these cases were actively pending within that specific district, while parallel litigation matrices were winding their way through dockets in Rotterdam and Midden-Nederland.
Compounding the court’s skepticism was the ghost-like presence of the applicant’s legal representation. Judges repeatedly noted deep doubts regarding the actual existence of the representatives named in the filings, observing that not a single representative ever materialized in person or virtually at a court hearing.
In its scathing assessment, the District Court of Noord-Holland held that the litigant had knowingly engineered artificial circumstances specifically to exploit the GDPR for financial enrichment. The bench observed that the individual was deliberately capitalizing on businesses’ widespread unfamiliarity with the nuances of European data protection regulations, combined with an inherent corporate fear of incurring exorbitant regulatory fines or massive litigation awards.
Chronology: The Timeline of a Legal Precedent
To understand the weight of the Noord-Holland rulings, one must trace the timeline of European case law and how it intersected with this specific Dutch litigation campaign.
March 19, 2026: The CJEU Sets the Standard
The foundation for the Dutch court’s intervention was laid on March 19, 2026, when the European Court of Justice handed down its critical ruling in Brillen Rottler v TC (Case C-624/24). Mirroring the exact pattern seen in the Dutch cases, the European dispute had also originated from an innocuous newsletter sign-up followed immediately by an aggressive Article 15 access request.
In Brillen Rottler, the CJEU established a vital interpretive principle regarding Article 12(5) of the GDPR: even a first-time data access request can be classified as "manifestly excessive" if the data subject has artificially and manipulatively created the underlying conditions solely to secure an unfair financial advantage.
July 2026: The Dutch Judgments
Barely four months after the European high court’s decision, the District Court of Noord-Holland became the primary testing ground for the doctrine in the Netherlands. Handing down its decisions in late July, the court formally declared all four claims—against Suitable, Scapino, At Home, and Wolters Wonen/Fundesign—completely inadmissible.
The timeline of the legal fallout highlighted critical procedural lessons for corporate defendants:
- The Scapino Exception: In the case involving Scapino, the retailer’s defense team had not formally argued an "abuse of rights" defense. Nevertheless, the court exercised its judicial prerogative, identifying and ruling upon the abusive nature of the claim ex officio (of its own motion).
- Cost Recovery Disparities: The post-judgment cost awards underscored the necessity of meticulous legal accounting. Suitable walked away having successfully recovered €7,047.97 in actual legal costs because its counsel meticulously submitted a detailed budget. Conversely, Wolters Wonen and Fundesign submitted no formal cost projections and were restricted to a standard-rate award of €2,230. Meanwhile, counterclaims filed by the retailers for corporate damages were uniformly rejected because the businesses failed to adequately quantify their financial losses.
Supporting Data: The Scale of the Phenomenon
The litigation campaign managed by the unnamed Dutch individual is symptomatic of a broader, troubling trend across the European Union where compliance mechanisms are treated as profit centers.
- 90+: The approximate number of formal GDPR access requests filed by the single individual across an 18-month period.
- 20: The number of active, concurrent cases pending solely within the jurisdiction of the District Court of Noord-Holland at the time of the rulings.
- €925: The standard extrajudicial cost demand levied within weeks of every initial data access request.
- €7,047.97: The maximum legal cost recovery achieved by a defendant (Suitable) through the submission of a verified legal expense budget.
- €2,230: The standard-rate cost award granted to defendants who failed to submit detailed legal cost budgets.
Official Responses and Legal Analysis
Legal scholars and data protection authorities have welcomed the rulings as a much-needed restoration of common sense within the GDPR ecosystem. For years, compliance officers have voiced concerns that the stringent enforcement mechanisms designed to protect fundamental human rights were being co-opted by bad actors seeking quick payouts.
Jorn van der Wiel, a senior privacy analyst at ICTRecht, emphasized that the rulings establish a vital boundary line. "The court has made it clear that the GDPR is a shield for personal privacy, not a sword for financial extortion," van der Wiel noted in the firm’s August 2026 jurisprudence review. "However, the judiciary has been careful not to swing the pendulum too far in the opposite direction."
Indeed, legal experts stress that businesses must interpret these rulings narrowly. The bar for proving an "abuse of rights" remains exceptionally high. The District Court of Noord-Holland explicitly reiterated that its decision was predicated upon an extreme and verifiable pattern of bad faith.
A single, awkward, or inconvenient data access request originating from an unknown or recently registered subscriber cannot simply be ignored under the assumption that it is fraudulent. Controllers remain legally obligated to provide a proper, timely, and comprehensive response to legitimate data subjects, regardless of how commercially inconvenient the inquiry may be.
Implications: What This Means for Data Controllers and Compliance Officers
For businesses operating in the Netherlands and the broader European Economic Area (EEA), the Noord-Holland rulings offer both profound relief and a definitive operational roadmap. Defending against predatory litigation requires more than just good intentions; it demands airtight administrative hygiene.
1. The Importance of Comprehensive Data Logging
To successfully invoke the Brillen Rottler precedent and demonstrate that an access request is part of an abusive scheme, controllers must be able to prove intent and pattern. This requires maintaining granular, immutable logs of every digital interaction. Essential evidentiary data points include:
- Signup Source and Timestamp: Exact documentation of how, when, and where a user entered the database (e.g., specific landing pages, promotional checkboxes, or checkout funnels).
- Consent Records: Verifiable audit trails showing the context of data collection.
- Lifecycle Tracking: A centralized log documenting every step of how an access request was handled, including timestamps of receipt, internal escalations, and communication histories.
2. Spotting the Red Flags
Compliance teams must train customer service and legal intake personnel to identify the behavioral markers of serial litigators. Key indicators include:
- Immediate transitions from low-value commercial interactions (newsletter signups, €10 purchases) to complex legal demands.
- Standardized, copy-paste demands for extrajudicial costs within a strict 14-to-30-day window following an SAR.
- Summonses that mirror filings submitted across multiple unrelated corporate entities.
3. Rigorous Defense Budgeting
The stark contrast between Suitable’s cost recovery (€7,047.97) and the lesser awards handed to retailers who failed to submit budgets serves as a cautionary tale. When forced into litigation by bad-faith actors, corporate defense teams must meticulously document and present itemized legal budgets to maximize cost recovery from unsuccessful claimants.
Conclusion
The Noord-Holland District Court has drawn a sharp line in the sand. By validating the principles of the Brillen Rottler judgment, Dutch jurisprudence has signaled that while corporate accountability under the GDPR remains absolute, the judiciary will no longer tolerate the transformation of European privacy law into a private lottery for bad actors. For businesses, the message is clear: maintain pristine compliance records, scrutinize incoming patterns, and do not hesitate to challenge abusive claims in court.