GLOBAL CYBERSECURITY REPORT — The first fortnight of September has delivered a stark reminder to security architects and threat hunters worldwide: cybercriminals are no longer attempting to break through the front door of enterprise defenses. Instead, they are quietly picking the locks from the inside, leveraging trusted platforms, legitimate application programming interfaces (APIs), and native browser behaviors to bypass traditional perimeter security.
Three distinct pieces of research published during the first two weeks of September have laid bare a new generation of evasion techniques. While each campaign relies on a different mechanism of delivery or deception, they all share a singular, highly effective strategy: authentication remains entirely intact, and the malicious payloads route directly through infrastructure, protocols, or endpoints that the recipient—and the security filter—already implicitly trust.
Main Facts: The Anatomy of Modern Evasion
Modern phishing has evolved far beyond the clumsy, typo-ridden emails of the past. Today’s threat actors operate with the precision and infrastructure of legitimate software-as-a-service (SaaS) providers. The September disclosures highlight a coordinated shift toward weaponizing trust:
- ASCII Smuggling via ActiveCampaign: Threat actors utilized invisible Unicode characters to slip past keyword-matching filters, leveraging reputable mail-delivery platforms and pre-established IP ranges to obscure malicious intent.
- The Serverless Phishing Page: Barracuda uncovered a campaign that abandons traditional hosting entirely, utilizing browser-native
blobURLs and legitimate Microsoft OAuth and Teams redirects to construct phishing pages dynamically inside the victim’s local memory—leaving no static artifacts for web scanners to index or block. - Phishing-as-a-Service (PaaS) Innovation: CloudSEK gained administrative visibility into "BigBear 2.0," an Evilginx2-backed PaaS platform. The panel revealed how threat actor affiliates are actively using custom JavaScript injection to systematically disable robust authentication factors like FIDO2, forcing victims toward weaker, interceptable MFA methods.
Crucially, in all three scenarios, SPF, DKIM, and DMARC checks routinely pass because the traffic originates from legitimate corporate routing mechanisms, trusted cloud services, or authenticated sessions.
Chronology of Disclosures (September 1–14)
The convergence of these distinct attack vectors within a tight fourteen-day window suggests an industry-wide evolution in threat actor tactics, techniques, and procedures (TTPs).
September 3: Microsoft Exposes ASCII Smuggling
Microsoft’s security research division published an exhaustive analysis detailing how threat actors successfully migrated a technique previously confined to AI prompt-injection research—ASCII smuggling—over into mass phishing evasion. Splicing invisible Unicode tag characters directly into email lure words, the attackers systematically hoodwinked keyword filters while ensuring the human eye perceived entirely normal business vocabulary.
September 7: CloudSEK Exposes the "BigBear 2.0" Panel
CloudSEK researchers published intelligence gathered from direct administrative access to BigBear 2.0, a sophisticated Phishing-as-a-Service infrastructure built atop the Evilginx2 framework. The compromised panel exposed thousands of harvested credentials and demonstrated how modern turnkey phishing kits actively manipulate browser environments to defeat advanced authentication protocols.
September 9: Barracuda Unveils Serverless Phishing
Barracuda disclosed a novel attack chain that sidesteps traditional web-based threat intelligence. By pairing a seemingly benign DocuSign-themed calendar invite with sophisticated Microsoft OAuth and Teams redirect chains, the campaign directed victims to load external resources that spontaneously materialized as temporary blob URLs within the victim’s browser memory.
Supporting Data and Technical Breakdown
To fully grasp the ingenuity of these September campaigns, security professionals must examine the underlying mechanics driving each vector.
1. The Mechanics of ASCII Smuggling
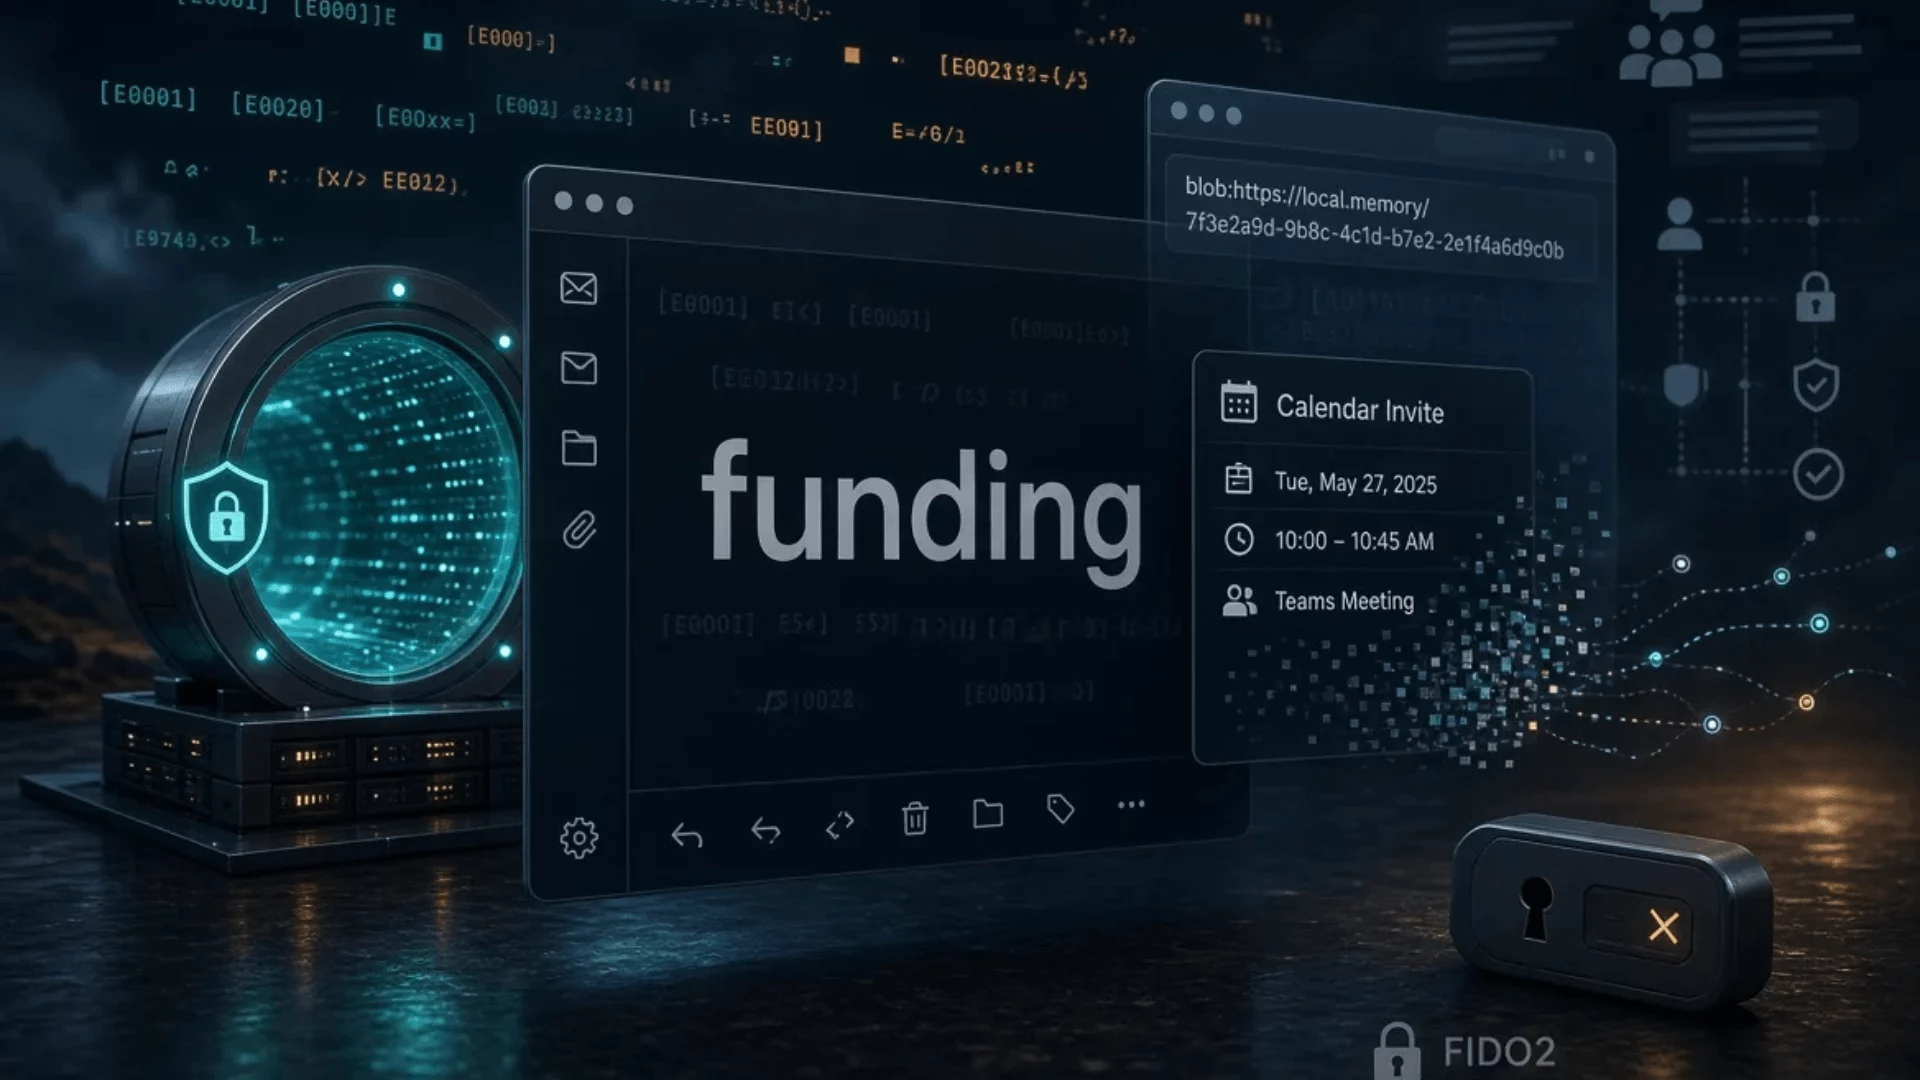
Dissected by Microsoft, the ASCII smuggling campaign relied on invisible Unicode tag characters—specifically code points U+E0000 to U+E007F. When deployed, an attacker can write a word like "fun", insert an invisible TAG SPACE (U+E0020), and follow it with "ding".
To a naive keyword-matching security filter scouring the payload for terms like "funding," no match is found. Yet, the human visual cortex automatically bridges the gap, reading the composite string as a single, coherent word.
[Target Word Segment: "fun"] + [Invisible Unicode Tag: U+E0020] + [Target Word Segment: "ding"]
= Filter Sees: Broken string (No Match)
= Human Sees: "funding" (Successful Lure)
Infrastructure Footprint:
- Volume: Weekday message volumes consistently ranged between 1 million and 2.37 million messages, peaking sharply on February 26, before going virtually dormant over weekends. This rhythm mirrors corporate batch-sending schedules.
- Domains: On February 9, researchers cataloged 148 finance-themed sender domains—systematic recombinations of a narrow lexicon (e.g., guardiangrowthfunding and 147 linguistic variations).
- Delivery Routing: Messages were relayed through the legitimate email marketing platform ActiveCampaign. Envelope senders followed a uniform structure (
em-<digits>.<brand-domain>), spreading a small pool of account numbers across hundreds of brand domains. Approximately 92% of measured volume traced back to a single/24network block owned by the platform. Links within the emails were automatically rewritten to point to ActiveCampaign’s legitimate tracking domains.
2. The Anatomy of a Serverless Phishing Attack
Barracuda’s September 9 report detailed an attack flow that completely eliminates the need for an attacker-controlled hosting server:
- The Hook: An email bearing a DocuSign theme arrives, complete with an attached calendar invite designed solely to normalize the correspondence in the eyes of the recipient.
- The Redirect: A carefully crafted redirect parameter steers the user through legitimate Microsoft OAuth flows into Microsoft Teams.
- The Resource Fetch: Teams loads an external, attacker-controlled resource hosted on infrastructure such as
cdn.bloom[.]io. - The Blob Generation: The victim’s web browser intercepts this resource and converts it into a
blobURL—a temporary, locally scoped address pointing exclusively to content held within the browser’s transient memory. - In-Browser Assembly: The credential harvesting interface is dynamically synthesized entirely inside the victim’s local browser environment. A service worker is registered, establishing a direct command-and-control bridge back to the operator’s backend.
Because no static webpage ever exists on an external server for a security scanner to fetch, and because the initial links point directly to unassailable Microsoft endpoints, traditional domain blocklists and URL reputation engines are rendered completely blind.
3. BigBear 2.0 and the War on FIDO2
CloudSEK’s infiltration of the BigBear 2.0 Evilginx2-powered PaaS platform revealed the inner workings of an enterprise-grade criminal enterprise. Leased out to at least five distinct affiliate operators, the administrative panel held:
- 5,137 total harvested credential records.
- 474 fully completed Multi-Factor Authentication (MFA) bypass sessions.
The platform’s success relied heavily on custom JavaScript modules injected during the man-in-the-middle proxy session. These scripts actively searched for browser capabilities and deliberately disabled modern, phishing-resistant FIDO2 hardware keys or passkeys, forcing targets to fall back on weaker, interceptable mechanisms such as SMS OTPs or standard push notifications.
Official Responses and Platform Accountability
The exploitation of reputable platforms like ActiveCampaign highlights a profound tension in modern cybersecurity: the delicate balance between robust email deliverability, platform usability, and defense against malicious abuse.
- ActiveCampaign’s Response: Ahead of Microsoft’s publication, ActiveCampaign issued a formal statement. The platform reported that it had rigorously tested the ASCII smuggling technique against its internal content moderation engines. Their findings indicated that messages containing invisible Unicode characters trigger the exact same baseline verdicts as their plain-text equivalents. However, ActiveCampaign confirmed that high-volume, anomalous utilization of these characters is actively flagged as a suspicious behavioral indicator.
-
Microsoft’s Defensive Guidance: Microsoft cautioned defenders against blindly blocking infrastructure indicators associated with the attack. Because the tracking domains and the
/24subnet blocks are actively shared by thousands of legitimate enterprise customers utilizing ActiveCampaign, hard-blocking these assets will inadvertently disrupt critical corporate newsletters and legitimate marketing communications.Instead, Microsoft advises security teams to normalize email payloads before running signature matches. Security filters should be configured to automatically strip tag-block and zero-width characters from both message subject lines and bodies prior to executing signature evaluations, treating the mere presence of these hidden characters as a high-fidelity anomaly signal.
Implementation Caveat: Rule-writing engineers must exercise caution; naive parsing regexes that broadly sweep for tag characters will inadvertently disrupt legitimate text containing the official flag emojis for England, Scotland, and Wales, which are natively encoded using Unicode tag characters.
Strategic Implications for Enterprise Security
The convergence of ASCII smuggling, serverless browser blobs, and PaaS-driven MFA downgrades forces a fundamental reassessment of how organizations protect their digital perimeters.
1. The Obsolescence of Perimeter-Only Trust
When threat actors route malicious payloads through trusted SaaS providers, rewrite links to legitimate tracking domains, and synthesize phishing pages within browser memory, traditional email security gateways (SEG) relying solely on reputation scoring and static URL blocklists will inevitably fail.
2. The Imperative of Phishing-Resistant Authentication
As demonstrated by the BigBear 2.0 intelligence, attackers are actively engineering around legacy MFA constraints. Organizations that continue to rely on push notifications, SMS, or software-based OTPs are operating with a dangerously false sense of security. Enterprises must aggressively accelerate their migration toward phishing-resistant MFA, specifically hardware-backed FIDO2 security keys and passkeys that cryptographically bind the authentication session to the legitimate origin domain, rendering adversary-in-the-middle (AiTM) proxy kits ineffective.
3. Platform Compliance and Self-Service Risks
For SaaS providers and email-sending platforms, the ActiveCampaign incident serves as a definitive wakeup call. Platforms featuring friction-free, self-service signups paired with shared IP pools remain prime targets for threat actors seeking instant IP reputation laundering. Providers must implement rigorous behavioral analytics—scrutinizing senders for automated weekday-only scheduling, linguistic vocabulary cycling across hundreds of disposable domains, and anomalous payload structures—before malicious campaigns ever reach the broader email ecosystem.
Conclusion
The September disclosures prove that cybercriminals have mastered the art of weaponizing digital trust. Defending against these sophisticated vectors requires an industry-wide pivot: away from fragile boundary blocklists, and toward deep payload normalization, advanced browser telemetry, and uncompromising, cryptographic zero-trust architectures.