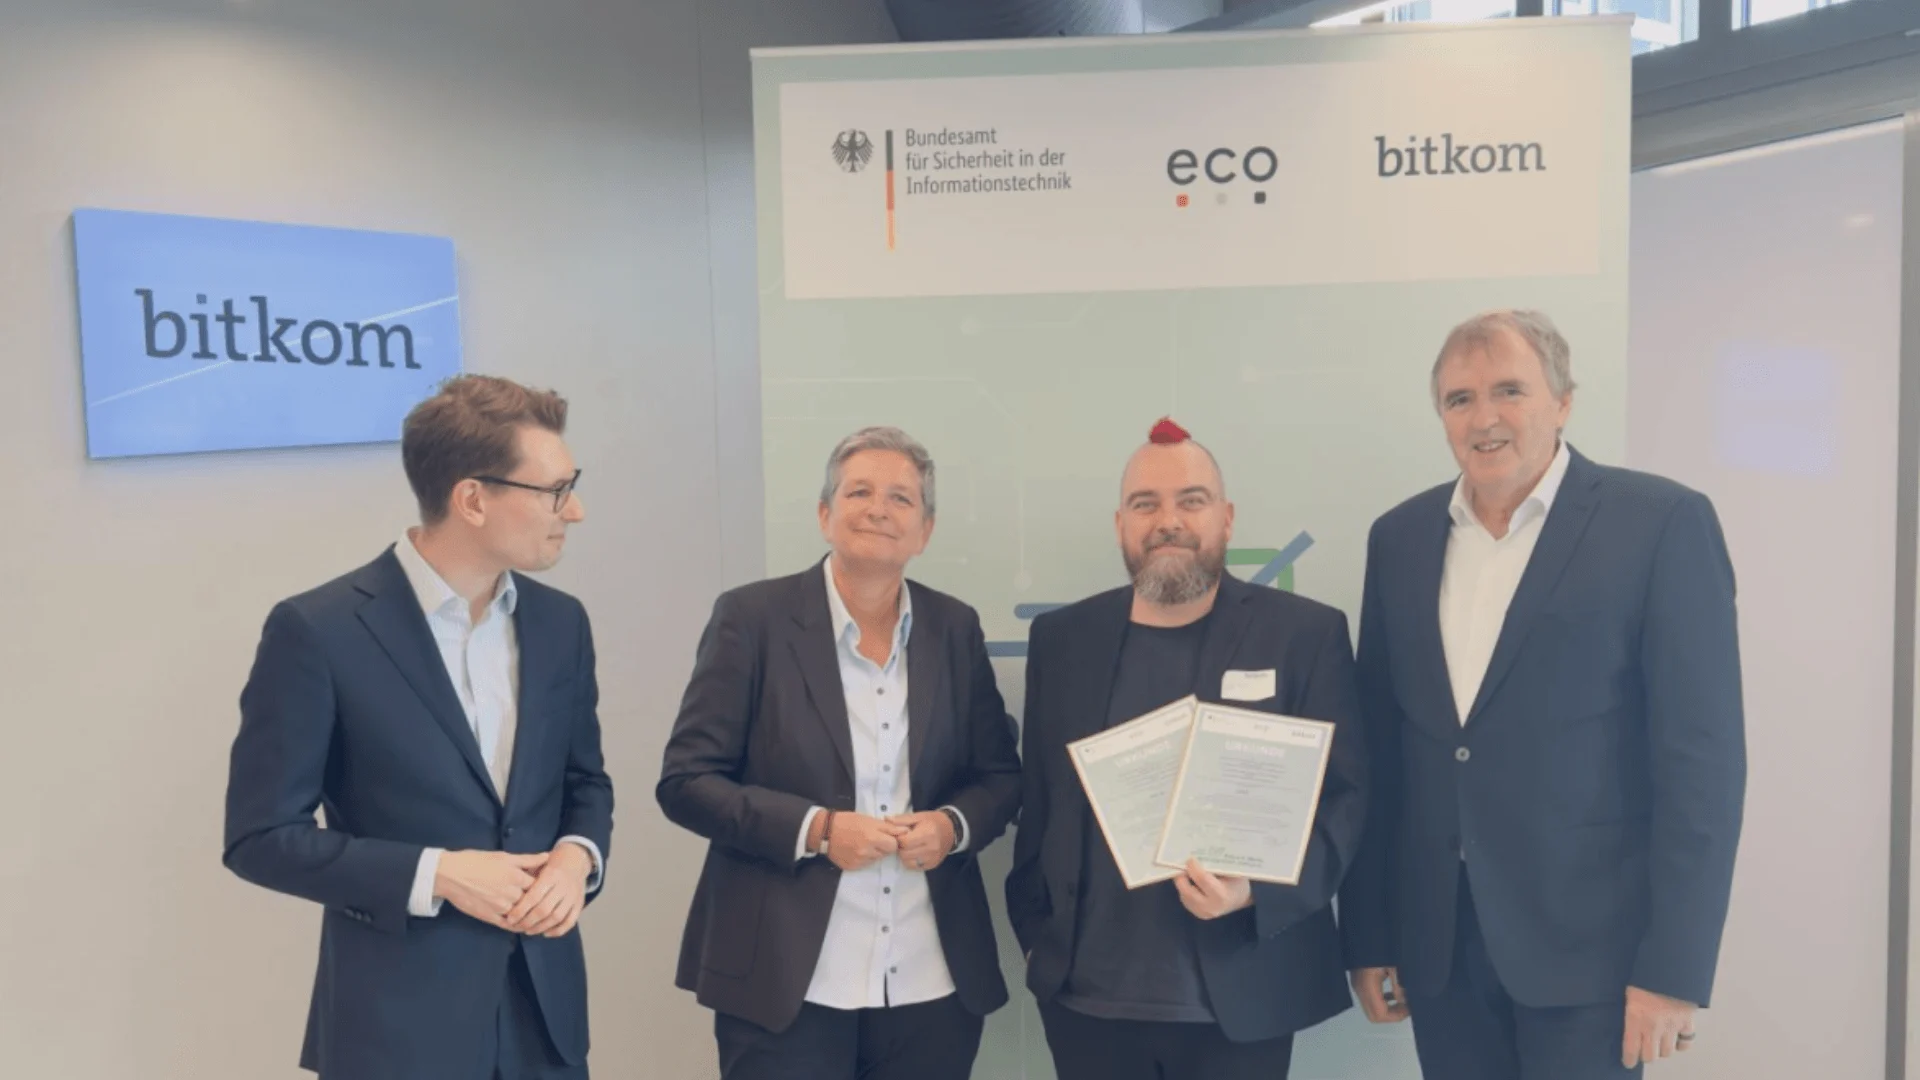
BERLIN — In a major validation of Germany’s digital infrastructure resilience, major email service providers GMX, WEB.DE, and mail.com have officially been inducted into the second round of the Federal Office for Information Security’s (BSI) prestigious Email Security Hall of Fame. The recognition, which marks a significant milestone in the ongoing battle against phishing, spoofing, and unauthorized data interception, was announced on LinkedIn by Tobias Herkula of 1&1 Mail & Media after he accepted the honors on behalf of the company.
The inclusion of these household-name communication platforms underscores a broader, nationwide pivot toward mandatory, verifiable cryptographic standards in European digital communication. As cyber threats grow increasingly sophisticated, the BSI—Germany’s national cybersecurity authority—is moving past voluntary guidelines and shifting toward enforced technological baselines to protect millions of everyday users.
Main Facts: The BSI’s Push for Cryptographic Certainty
The induction of GMX, WEB.DE, and mail.com is not merely an honorary pat on the back; it is a technical audit-backed certification. The BSI’s Email Security Hall of Fame initiative, launched as a centerpiece of the broader "Email Security Year" campaign, aims to overhaul how email providers handle transport encryption, domain authentication, and cryptographic integrity.
To secure their place in the second round of the Hall of Fame, providers could no longer rely on mere policy pledges or future roadmaps. They had to prove compliance through live, verifiable implementations. Specifically, entrants were required to have DNSSEC (Domain Name System Security Extensions) fully live and operational by June 30, 2026—a mandate that the BSI independently verified before granting induction.
The initiative ties directly into the BSI’s rigorous technical guidelines:
- TR-03108: Governs secure transport mechanisms, ensuring data in transit cannot be eavesdropped upon or modified.
- TR-03182: Focuses on sender and domain authentication, preventing malicious actors from forging emails that appear to originate from trusted entities.
When evaluated through the BSI’s public E-Mail-Checker tool, platforms like gmx.de score an impressive seven out of seven on core cryptographic standards, featuring robust deployments of SPF (Sender Policy Framework), DKIM (DomainKeys Identified Mail), DMARC (Domain-based Message Authentication, Reporting, and Conformance), DNSSEC, DANE (DNS-based Authentication of Named Entities), and support for both TLS 1.2 and TLS 1.3.
However, the evaluation also revealed nuances in consumer-facing infrastructure. While core security pillars are rock-solid, certain unweighted extra parameters—such as MTA-STS (Mail Transfer Agent Strict Transport Security), TLS reporting, and the complete deprecation of legacy TLS versions below 1.2—remain unmet. Industry veterans note that disabling legacy TLS entirely remains a persistent hurdle for consumer mailbox services, as forcing strict modern standards can inadvertently lock out users accessing their accounts via antiquated, unpatchable legacy hardware or custom-built embedded mail clients.
Chronology: The Evolution of the Email Security Campaign
The journey toward the second and final round of the BSI’s Hall of Fame has been a carefully orchestrated multi-phase regulatory and industry effort.
2025: The Launch of Email Security Year
The framework began in early 2025 as part of a high-profile national campaign spearheaded by the BSI in close collaboration with German digital industry associations eco and Bitkom. Recognizing that email remains the primary vector for enterprise malware delivery, credential harvesting, and social engineering, the campaign sought to drag legacy mail infrastructure into a modern cryptographic age.
August 2025: The First Round and Gold Accolades
The first phase of the campaign focused on commitment and roadmap alignment. In August 2025, the BSI published an inaugural list featuring approximately 150 organizations that had officially committed to implementing—or were actively working toward—the BSI’s technical guidelines for secure transport and authentication. During this initial milestone, GMX and WEB.DE stood out by securing coveted Gold status, signaling that their technical implementations were already far ahead of the industry average.
Mid-2026: The Hard Deadline and Round Two
Unlike the inaugural phase, which rewarded intention and structured progress, the second round—announced as the final iteration of the scheme—demanded hard proof. The BSI set a strict operational deadline of June 30, 2026, requiring all participating providers to have DNSSEC live in production.
Following independent technical verification by BSI auditors, the final roster of compliant providers was locked in. Tobias Herkula’s LinkedIn announcement officially sealed the induction of GMX, WEB.DE, and mail.com, bringing the campaign to a definitive close. With this second round, the BSI has signaled the end of its structured Hall of Fame campaigns, leaving the ball firmly in the court of the wider market to maintain and build upon these standards.
Supporting Data: Technical Posture and Audit Metrics
Evaluating the technical posture of modern email providers requires looking beyond marketing claims and analyzing core cryptographic layers. The BSI’s public E-Mail-Checker provides an empirical breakdown of how top-tier German providers stack up against international benchmarks.
| Security Feature | Status on GMX / WEB.DE | Technical Objective |
|---|---|---|
| SPF | Implemented | Prevents spoofing by designating authorized sending servers. |
| DKIM | Implemented | Adds a cryptographic signature to verify message integrity and origin. |
| DMARC | Implemented | Uses SPF and DKIM to determine email authenticity and dictates handling policy. |
| DNSSEC | Verified Live (June 2026) | Protects against DNS spoofing and cache-poisoning attacks. |
| DANE | Implemented | Associates TLS certificates with DNS records for secure routing. |
| TLS 1.2 / 1.3 | Implemented | Ensures strong, modern encryption for data in transit. |
| MTA-STS | Unmet (Optional) | Enforces TLS encryption between Mail Transfer Agents. |
| TLS Reporting | Unmet (Optional) | Provides feedback loops on TLS failures. |
| Legacy TLS Deprecation | Pending/Partial | Disabling TLS versions below 1.2 (constrained by consumer legacy client support). |
The inclusion of DANE in this stack holds particular significance for high-volume corporate senders. While standard transport layer security encrypts data between the client and the mail server, DANE leverages DNSSEC to bind a domain’s TLS certificate directly to its DNS records. This allows sending Mail Transfer Agents (MTAs) to cryptographically verify that they are delivering mail to the intended destination server, effectively neutralizing advanced Man-in-the-Middle (MitM) attacks.
Official Responses and Industry Reactions
The formal conclusion of the BSI’s campaign has drawn widespread commentary from industry leaders, technical standard-bearers, and corporate representatives.
Accepting the recognition on behalf of 1&1 Mail & Media, Tobias Herkula took to professional networks to celebrate the milestone, emphasizing the collaborative nature of the achievement. "Securing consumer-scale infrastructure requires balancing uncompromising cryptographic rigor with the accessibility expected by millions of everyday users," industry observers noted regarding the company’s continuous security upgrades.
Representatives from eco (Association of the Internet Industry) and Bitkom—both of whom co-sponsored the Email Security Year initiative—praised the BSI’s pragmatic yet firm regulatory approach. Rather than imposing rigid, unachievable mandates overnight, the multi-phase campaign provided a clear runway, moving organizations smoothly from voluntary policy adoption to hard technical verification.
Cybersecurity analysts have also lauded the BSI for closing the loop with independent technical audits. By actively verifying DNSSEC deployments rather than relying on self-reported questionnaires, the German authority has set a high benchmark for digital sovereignty and consumer protection across the European Union.
Implications: What This Means for Senders and the Broader Market
While the Hall of Fame inductions are a feather in the cap for GMX, WEB.DE, and mail.com, the practical implications extend far beyond corporate PR. The changes ripple directly into how third-party senders, enterprise marketers, and international corporations must interact with German mail infrastructure.
1. No Impact on Content Filtering
It is critical to note that inclusion in the BSI’s Hall of Fame changes nothing regarding spam filtering, reputation scoring, or anti-abuse algorithms. Achieving cryptographic compliance guarantees that a message is transported securely and authenticated properly; it does not exempt commercial senders from rigorous content evaluation, engagement metrics, or anti-spam compliance.
2. The Urgent Imperative for DANE Support
For organizations sending high volumes of email into the German market, the widespread adoption of DANE by major providers like GMX and WEB.DE serves as a subtle yet powerful wake-up call. DANE only protects email transmissions when the sending MTA is configured to check TLSA records.
If an enterprise or bulk sender continues to operate legacy sending infrastructure that fails to validate DANE/DNSSEC records, their outbound communications miss out on an advanced layer of trust. As European mailbox providers tighten security baselines, failure to modernize sending infrastructure risks subtle delivery friction, delayed handshakes, or outright trust degradation. Organizations with significant mailing volume directed toward Germany are strongly advised to audit their outbound MTAs to ensure full compatibility with modern DANE verification protocols.
3. A Blueprint for Global Cybersecurity
As the BSI closes the book on its Email Security Hall of Fame campaign, the initiative stands out as a rare success story in coordinated public-private cybersecurity governance. By leveraging clear technical standards (TR-03108 and TR-03182), public transparency tools (E-Mail-Checker), and time-bound verification audits, Germany has successfully raised the cryptographic floor for millions of everyday consumer mailboxes.
For the global digital community, the German model proves that consumer-scale email security is not an impossible pipe dream—it is an achievable, verifiable reality for organizations willing to commit to technical excellence.