By European Tech & Commerce Desk
Published: September 2024
Main Facts
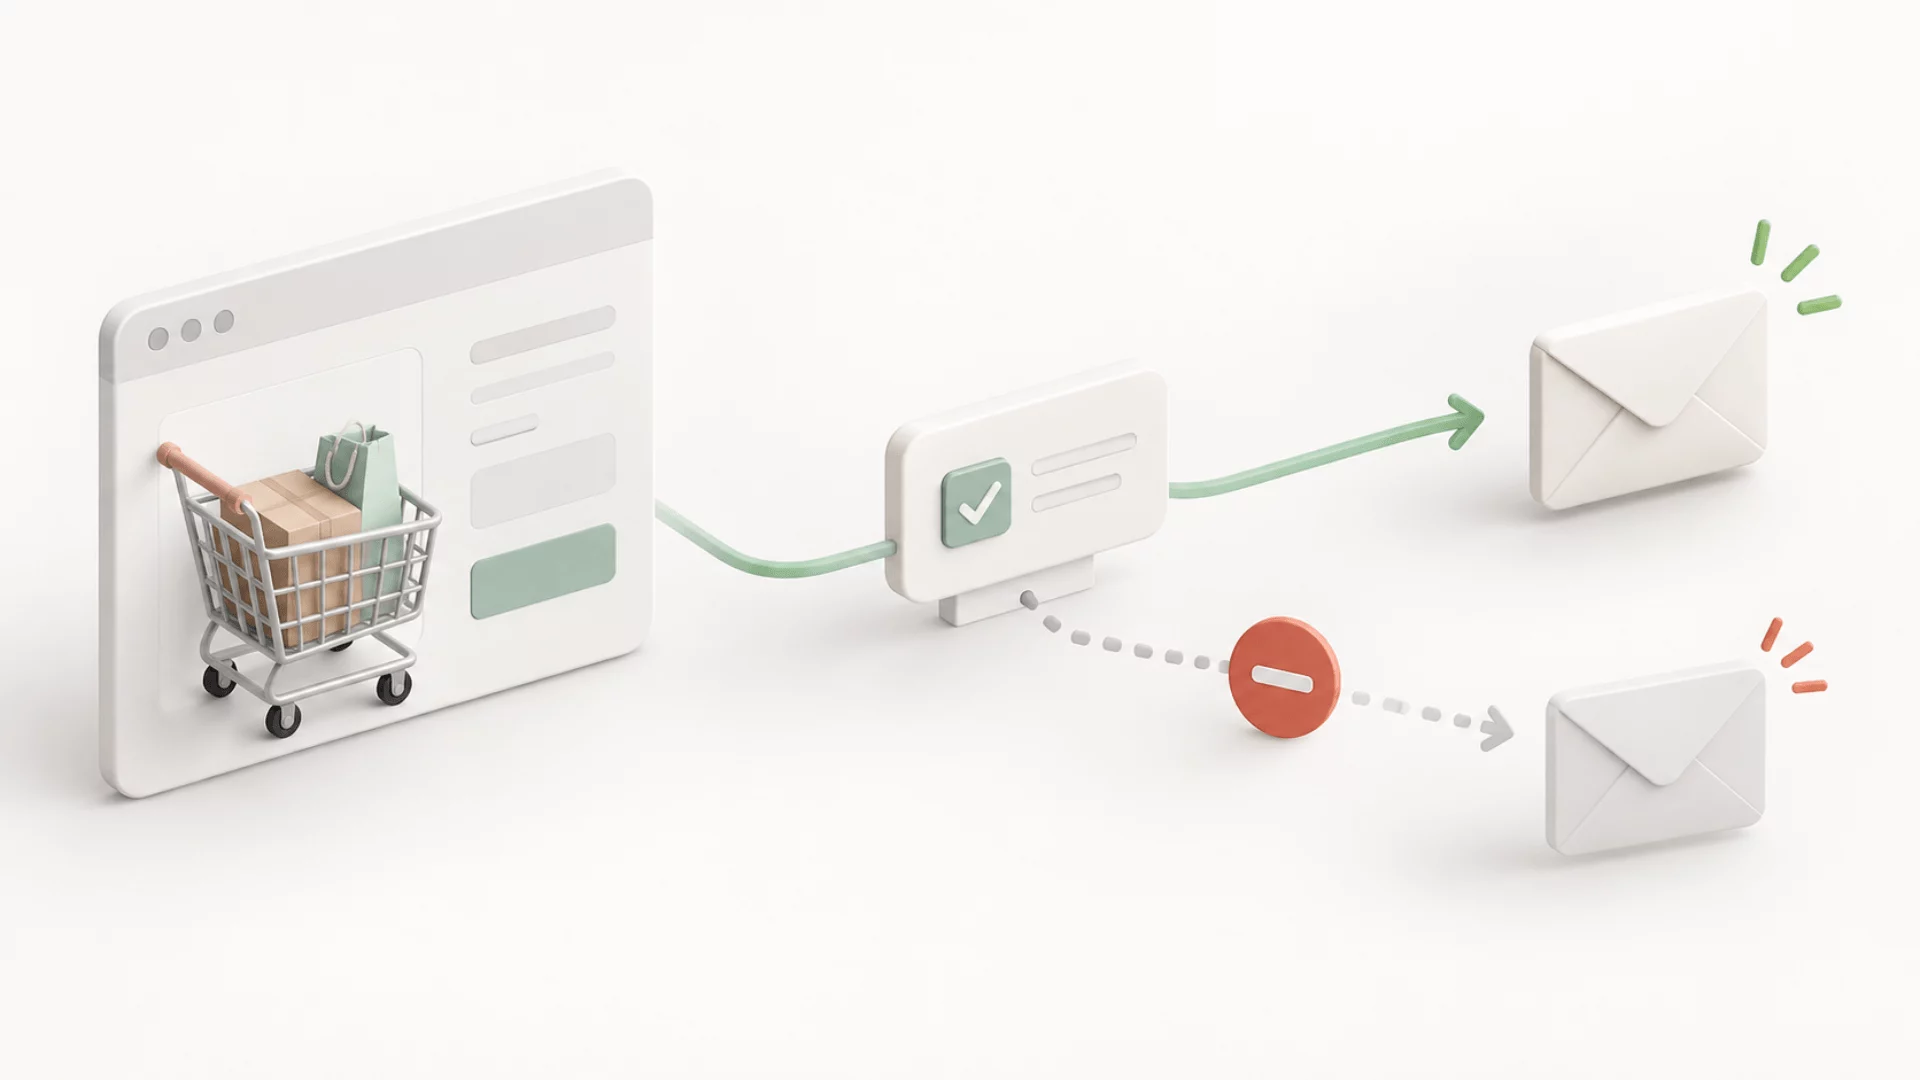
European e-commerce platforms and digital marketing teams are facing a harsh regulatory reckoning over a tactic long considered standard digital housekeeping: the abandoned cart recovery email. Recent legal clarifications from the Netherlands and Germany have reaffirmed a strict interpretation of European privacy laws, establishing unequivocally that automated emails sent to prospective buyers who abandon their shopping carts without completing a purchase violate the European Union’s ePrivacy Directive and General Data Protection Regulation (GDPR).
The core legal bottleneck rests on the definition of direct marketing and the prerequisites for lawful data processing. Under EU law, any communication possessing commercial intent—such as an automated nudge reminding a consumer about items left sitting in a digital basket—is classified as direct marketing. Consequently, such outreach sits firmly behind a mandatory opt-in wall.
While many retailers have leaned on the "existing customer relationship" exception (often referred to as the "soft opt-in") to justify these follow-ups, legal authorities have made it clear that this exception is entirely inapplicable to abandoned carts. A completed transaction is a fundamental prerequisite for the soft opt-in. Because an abandoned checkout represents a transaction that never materialized, and because the browser’s email address was often captured mid-session without explicit, prior consent for marketing purposes, these automated recovery sequences are, under strict legal review, unlawful.
The fallout extends far beyond mere legal compliance. Technical misconfigurations across popular e-commerce platforms—ranging from ignored consent flags in API payloads to aggressive pre-submit data capture scripts—are routinely exposing retailers to regulatory fines. Furthermore, because these unconsented emails frequently trigger high volumes of spam complaints, brands risk damaging their sender reputation, which can critically degrade the deliverability of essential transactional messages like order confirmations and dispatch notices.
Chronology
To understand how the digital marketing landscape arrived at this enforcement crossroads, it is necessary to examine the timeline of regulatory developments, judicial clarifications, and shifting technical standards that have shaped the modern compliance environment.
- May 2018 (GDPR Enactment): The General Data Protection Regulation goes into effect across the European Economic Area (EEA), radically overhauling the legal standards for consent, which must now be freely given, specific, informed, and unambiguous.
- Late 2023 (The Inteligo Media Ruling): The Court of Justice of the European Union (CJEU) delivers its landmark Inteligo Media judgment. The court clarifies that free account registrations can satisfy the requirements of a "sale" context under the ePrivacy Directive, allowing freemium publishers to send newsletters under the soft opt-in framework without requiring a financial transaction. However, the ruling strictly hinges on a completed user registration—a standard that ephemeral, incomplete checkouts fail to meet.
- 2024 (Hessian Data Protection Authority Activity Report): Prompted by a wave of consumer complaints regarding webshops aggressively emailing individuals who had never completed a purchase, the Hessian data protection authority in Germany issues a formal declaration. The authority explicitly targets abandoned shopping cart emails, declaring them illegal in the absence of explicit, prior consent.
- September 16, 2024 (ICTRecht Legal Clarification): Dutch legal consultancy ICTRecht publishes a definitive analysis addressing the question: Can you email someone who filled a basket and left? The answer, echoing the German enforcement position, is a firm no—not without prior, explicit consent or an established customer relationship built on a prior transaction.
- Ongoing (Deliverability and Enforcement Pressure): Major inbox providers, including Google and Yahoo, enforce stringent bulk-sender requirements—mandating spam complaint rates remain strictly below 0.3% (ideally under 0.1%). Retailers running unconsented cart recovery campaigns begin experiencing severe deliverability degradation as flagged messages damage their primary sending domains.
Supporting Data
The operational mechanics of e-commerce platforms reveal a systemic disconnect between technical capabilities and legal execution. An analysis of modern platform infrastructures highlights why compliance failures remain so widespread:
- Platform API Behavior: Major platforms, such as Shopify, natively capture customer information during the checkout flow. Within the Shopify abandoned checkout record, developers have access to a distinct boolean data field:
buyer_accepts_marketing. This field sits directly alongside the captured email address, explicitly indicating whether the user checked the marketing consent box. - Integration Blind Spots: Despite the availability of the
buyer_accepts_marketingflag, third-party marketing automation platforms (such as Klaviyo, Omnisend, and custom-built CRM integrations) frequently ingest raw checkout records without validating the status of the consent boolean. Consequently, leads with afalsevalue are systematically enrolled in automated drip campaigns. - The Pre-Submit Data Capture Phenomenon: Identity resolution vendors and advanced behavioral tracking tags utilize client-side scripts that read the email input field on blur (the moment a user clicks away from the text box, even before hitting "submit"). This allows vendors to capture and store email addresses from anonymous users who abandon their sessions before reaching the final checkout button. In the EEA, this practice operates without a lawful basis for processing, as the data is harvested before explicit consent or submission occurs.
- Deliverability Thresholds: According to modern email infrastructure standards set by major mailbox providers, bulk senders must maintain a spam complaint rate below 0.3%, with a preferred target of under 0.1%. Unsolicited cart recovery emails, by their very nature of targeting users who never expected or consented to the communication, generate disproportionately high rates of spam complaints.
- Infrastructure Risk: Because many retailers deploy their cart recovery workflows through the exact same domain and IP infrastructure used for critical operational messages—such as order receipts, shipping notifications, and password resets—high spam complaint rates can severely impair core business communications.
Official Responses
Regulatory bodies, legal experts, and industry analysts have increasingly aligned on their interpretation of European privacy frameworks as applied to modern e-commerce retargeting.
Data protection authorities across the EEA have adopted a uniform stance: commercial intent triggers the strict requirements of the ePrivacy Directive. In its 2024 activity report, the Hessian data protection authority addressed the complaints of consumers who found themselves targeted by webshops following abandoned sessions. The authority emphasized that an online shopping cart is merely a transitional state, not a contractual relationship. Without a finalized transaction or a distinct, prior opt-in, commercial messaging directed at these transient visitors constitutes an infringement of privacy rights.
Legal scholars at firms like ICTRecht have reinforced this perspective, noting that e-commerce teams have long relied on outdated assumptions regarding consumer engagement. Many digital marketers assumed that the mere entry of an email address into a checkout form constituted an implied invitation to engage. Legal authorities have categorically rejected this assumption, drawing a sharp boundary between operational data processing (necessary to complete an active purchase) and promotional data processing (which requires distinct, unbundled, and affirmative consent).
Meanwhile, privacy advocates point to the CJEU’s Inteligo Media decision as the outer boundary of what is permissible. While the court demonstrated flexibility regarding "freemium" models where no money changes hands, it did so specifically because the user executed a deliberate, complete registration action. An abandoned checkout—characterized by a user abruptly closing a browser tab before final submission—possesses none of the deliberateness or legal finality required to establish a soft opt-in relationship.
Implications
The rigorous enforcement of data protection laws regarding abandoned cart emails carries profound implications for the digital marketing industry, software developers, and e-commerce merchants operating within or targeting the European market.
1. The Death of Automated Retargeting-by-Default
For years, digital marketing agencies have treated abandoned cart sequences as "set-and-forget" revenue generators. Moving forward, deploying these campaigns without a verified, granular opt-in mechanism exposes merchants to severe regulatory scrutiny and substantial financial penalties under the GDPR. Marketing teams must transition from passive email harvesting to active, transparent consent-gathering strategies.
2. Technical Overhauls of Marketing Integrations
E-commerce developers and platform administrators must audit their data pipelines immediately. It is no longer acceptable for marketing automation tools to ingest raw checkout payloads indiscriminately. Platforms must enforce strict filtering logic that cross-references the buyer_accepts_marketing flag before any contact record is synchronized to an email service provider. Furthermore, the use of aggressive pre-submit "blur" capture tags must be eliminated on EEA-facing properties to prevent unlawful data acquisition.
3. Deliverability Preservation and Domain Segregation
The technical intersection of email marketing and domain reputation means that non-compliant cart recovery emails pose an existential threat to everyday business operations. If unconsented recovery emails drive spam complaint rates above the strict 0.3% thresholds mandated by Google and Yahoo, the sender domain’s overall reputation plummets. This degradation directly impacts transactional messaging—meaning customers may stop receiving order confirmations, shipping updates, and password reset links. To mitigate this, brands must either achieve absolute compliance in their consent collection or strongly consider separating their transactional and promotional mailing infrastructures across distinct subdomains.
4. Strategic Pivot Toward On-Site Conversion
As traditional email retargeting faces tighter legal constraints, merchants must refocus their conversion rate optimization (CRO) efforts on on-site strategies. This includes refining exit-intent pop-ups that secure explicit, standalone marketing consent before the user abandons the session, as well as enhancing the overall checkout UX to reduce abandonment rates organically, rather than relying on aggressive post-session digital pursuit.
Ultimately, the tightening regulatory landscape signals the end of frictionless, unconsented data exploitation in European e-commerce. Retailers who adapt their technical stacks and legal frameworks to honor consumer consent will not only avoid costly regulatory penalties but will also build a foundation of trust that protects their brand reputation and email deliverability for the long term.