REDMOND, Wash. — IT administrators managing hybrid messaging infrastructures are facing a high-stakes operational crunch this month, driven by two uncompromising enforcement deadlines enforced by Microsoft. With one deadline having already passed and a second rapidly approaching, organizations utilizing hybrid configurations between on-premises Microsoft Exchange environments and Exchange Online are being forced to accelerate patching schedules and refactor legacy integrations under severe time constraints.
The unfolding situation highlights Microsoft’s increasingly aggressive posture toward legacy software depreciation, security baseline enforcement, and the forced migration of enterprise customers toward modern API standards and subscription-based licensing models. For unprepared organizations, these updates translate directly to sluggish message queues, sudden application outages, and the looming reality of costly extended support agreements.
Main Facts: The Double-Barreled Microsoft Enforcement Wave
The current administrative turbulence centers on two distinct administrative requirements affecting on-premises Exchange servers and Exchange Online tenants:
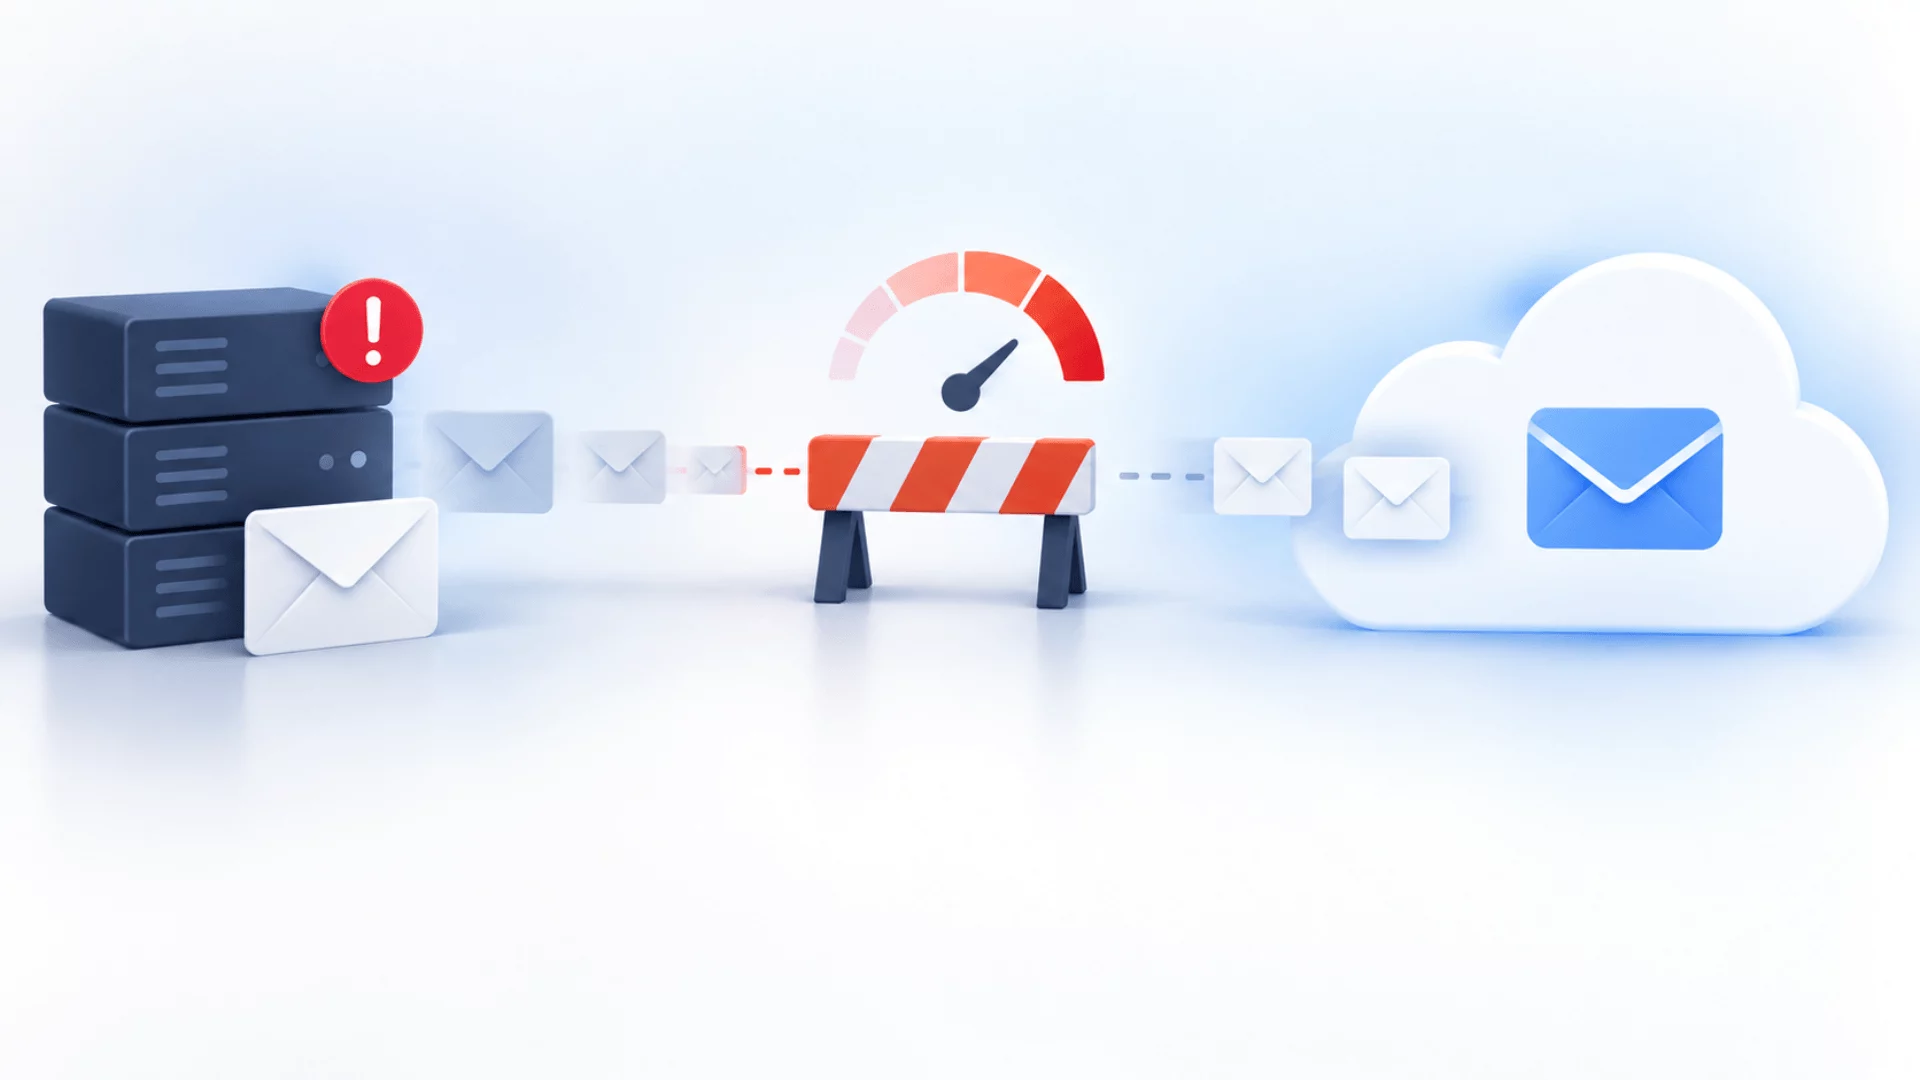
- The Exchange Server Security Update Baseline Enforcement: Beginning in the second week of September, Microsoft initiated automated throttling and subsequent blocking of inbound mail flow originating from legacy on-premises Exchange servers communicating via "OnPremises" type inbound connectors. To evade this automated disruption, servers must be running the specific baseline security update footprint matching the October 2025 release cycle.
- The Exchange Web Services (EWS) Automated Tenant Flip: Scheduled to land at the conclusion of September, Microsoft is executing an automated security baseline adjustment across Exchange Online tenants. Any tenant where the global
EWSEnabledparameter remains left asNullwill see this configuration automatically flipped toFalse, immediately severing EWS access for all associated third-party applications, legacy scripts, and custom integrations.
Neither of these measures constitutes a routine advisory warning. Both represent automated enforcement actions executed directly within Microsoft 365 cloud infrastructure. Consequently, administrative teams experiencing unexpected delivery delays, mail flow bottlenecks, or application-level connectivity failures are advised to audit their infrastructure configurations immediately before troubleshooting local network anomalies or routing bottlenecks.
Chronology: A Timeline of Warnings, Deadlines, and Enforcement Actions
Understanding how the current operational landscape materialized requires reviewing the sequence of announcements and compliance milestones orchestrated by the Microsoft Exchange team.
The Build-Up to September 2025
For years, Microsoft has signaled the eventual sun-setting of older Exchange architectures, paired with progressive tightening of security requirements for mail routed into Exchange Online. Because on-premises Exchange servers represent a notorious vector for vulnerability exploitation—a reality underscored by historically severe zero-day campaigns—Redmond introduced transport-layer restrictions designed to force administrative compliance.
- Late 2023 – Mid 2024: Microsoft introduces initial transport-layer enforcement warnings, signaling that out-of-date on-premises Exchange servers sending hybrid mail would eventually face throttling. Administrators are directed to monitor specific transport logs for warning codes.
- October 2025: The final public update baseline for Exchange Server 2016 and Exchange Server 2019 is released, marking the formal end of standard mainstream support. Organizations face a binary choice: migrate to modern alternatives, subscribe to the paid Extended Security Update (ESU) program, or accept unpatched risk.
- Early September 2025: Enforcement mechanisms activate. Inbound connectors utilizing
OnPremisestypes begin evaluating sending server build numbers. Servers failing to meet the required baseline encounter progressive throttling, characterized by intentional processing delays. - Mid-September 2025: Throttling transitions to active blocking for non-compliant servers, generating specific SMTP error codes within local queues.
- September 30, 2025 (The EWS Threshold): The final window closes for tenants relying on default configurations for Exchange Web Services. Unless explicitly overridden, tenant-wide EWS availability shifts from unconfigured (
Null) to explicitly disabled (False). - April 1, 2027 (The Ultimate Horizon): The absolute sunset date for Exchange Web Services. Even applications granted temporary reprieves via AppID allow lists will have their underlying protocol support permanently retired.
Supporting Data: Identifying Symptoms, Log Entries, and Diagnostic Commands
For systems administrators attempting to diagnose mail flow anomalies or application communication failures, recognizing the precise telemetry generated by Microsoft’s enforcement engine is critical.
Diagnosing Hybrid Mail Flow Throttling
When an on-premises Exchange 2016 or 2019 server falls below the mandated update baseline, messages routed over an inbound connector typed as OnPremises do not simply fail outright at first. Instead, Microsoft employs a progressive enforcement model:
- Initial Throttling: Message acceptance rates are artificially slowed down. To an observer, this mimics ordinary network congestion or high-volume queue backpressure.
- Active Blocking: Once the grace period or threshold is entirely breached, messages are rejected at the transport layer. Crucially, administrators must note that this is a transport enforcement rule, not an authentication failure. A message can pass all modern validation mechanisms—including Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and Domain-based Message Authentication, Reporting, and Conformance (DMARC)—with flying colors, yet still be systematically rejected purely based on the sending server’s software build version.
Key Diagnostic Indicators and Commands
Administrators should immediately run diagnostic tooling to evaluate their exposure:
-
Checking Inbound Connectors: Execute the following PowerShell cmdlet within the Exchange Management Shell to identify whether your organization utilizes vulnerable connector configurations:
Get-InboundConnector | Format-Table Name, ConnectorType, EnabledIf connectors are designated as
OnPremises, they are directly subject to the security baseline check. -
Isolating Error Logs: Look specifically for SMTP response log entries bearing the status codes
4.7.230and5.7.230. These specific numerical identifiers signify transport-layer enforcement actions taken against out-of-date sending infrastructure. -
Requesting a Temporary Pause: Microsoft provides a safety valve for organizations caught mid-migration or facing emergency patching delays. Administrators can request a temporary pause of throttling and blocking behaviors directly through the Mail Flow Report section within the Exchange Admin Center (EAC). However, documentation emphasizes that this is strictly a bridge to allow emergency patching, not a permanent exemption.
Diagnosing EWS Exposure
For applications relying on Exchange Web Services, the diagnostic workflow centers on tenant configuration parameters and usage reporting.
-
Auditing Tenant Status: Check the current global EWS status via PowerShell connected to Exchange Online:
Get-OrganizationConfig | Select-Object EWSEnabledIf this returns
Null(indicating the default, unconfigured state prior to the deadline), the automated Microsoft enforcement script will flip the parameter toFalseon October 1. -
Identifying Dependent Applications: Administrators must not guess which internal scripts, legacy time-tracking tools, or third-party monitoring platforms utilize EWS. Instead, navigate to the Microsoft 365 Admin Center, select Reports, then Usage, and finally Exchange. The EWS usage report provides a granular breakdown of application activity, detailing precisely which AppIDs are actively hammering legacy endpoints and requiring urgent remediation.
Official Responses and Strategic Guidance from Microsoft
Microsoft’s documentation frames these enforcement actions not as punitive measures, but as vital steps in securing the global messaging fabric against systemic compromise. In technical blog posts published via the Exchange Team Blog, Microsoft representatives have reiterated that legacy on-premises servers running unpatched software represent an unacceptable security liability when bridged directly into enterprise cloud tenancies via hybrid configurations.
The Licensing Reality: ESU and SE
Underpinning the current operational crisis is the changing economics of Microsoft Exchange. The October 2025 baseline requirement coincides with the formal cessation of mainstream support for Exchange Server 2016 and 2019.
For organizations unable to migrate off these aging platforms entirely by this milestone, Microsoft points toward two primary pathways:
- The Extended Security Update (ESU) Program: A paid, subscription-based program providing critical security patches for legacy environments past their official end-of-life date.
- Exchange Server Subscription Edition (Exchange SE): The modern, subscription-based architecture designed to replace perpetual licensing models and maintain continuous alignment with Microsoft’s cumulative update cadence.
Official guidance stresses that future security floors will continue to rise. As Microsoft deprecates legacy authentication methods, underlying cryptographic protocols, and outdated APIs, the cost of maintaining static on-premises infrastructure will scale upward sharply.
Implications: What This Means for Enterprise IT Strategy
The twin deadlines of September 2025 serve as a watershed moment for enterprise messaging administrators, carrying profound implications for infrastructure management, budget allocation, and application architecture.
1. The Death of "Set-and-Forget" Infrastructure
For decades, many organizations treated on-premises email servers as stable, permanent appliances: once deployed and configured, they were left to run with minimal intervention beyond routine cumulative updates. The enforcement of strict security baselines for hybrid mail flow shatters this paradigm. On-premises infrastructure deeply integrated with the cloud is now subject to cloud-speed governance. Failing to maintain a rigid patching cadence no longer merely risks internal exploitation; it breaks external mail delivery to Microsoft 365 recipients entirely.
2. Accelerated Cloud Migration and API Modernization
The EWS deprecation timeline—culminating in total shutdown on April 1, 2027—forces a hard reckoning with legacy codebases. Many enterprise software vendors built integrations on EWS over a decade ago and have been slow to rewrite their data connectors for Microsoft Graph, the unified API endpoint for Microsoft 365.
While configuring an AppID allow list provides a temporary safety net past the initial autumn cutoff, it represents a stay of execution rather than a strategic solution. IT leaders must audit software supply chains immediately, demanding that third-party vendors certify compatibility with Microsoft Graph well in advance of the 2027 hard stop.
3. Budgetary Pressures on IT Departments
The convergence of end-of-support milestones, mandatory ESU subscriptions, and urgent software refactoring initiatives places unprecedented strain on IT operating budgets. Organizations that delayed moving mailboxes to Exchange Online are now discovering that the financial penalties of stagnation—manifested in consultant fees, emergency licensing costs, and potential operational downtime—far outweigh the capital expenditure of a planned migration.
Action Plan for Administrators
To survive the current enforcement window and safeguard future operations, IT teams must execute a four-point checklist immediately:
- Verify Build Numbers: Check all hybrid-connected Exchange 2016 and 2019 servers to ensure they match or exceed the required security update baseline.
- Inspect Mail Flow Logs: Review transport queues for
4.7.230and5.7.230error codes, utilizing the Exchange Admin Center to request an emergency pause if throttling is actively disrupting business operations. - Audit EWS Dependency: Access the Microsoft 365 Admin Center usage reports to catalog all applications utilizing Exchange Web Services.
- Implement Temporary Allow Lists: Explicitly define AppID allow lists and set
EWSEnabledtoTruewhere necessary before the automated transition occurs, while simultaneously launching projects to migrate all dependent tools to Microsoft Graph before April 2027.
The message from Redmond is unequivocal: the era of unmanaged or lagging on-premises Exchange integration with the cloud has officially ended. Adapting to the new baseline is no longer optional for maintaining operational continuity.