BERLIN — In a major milestone for European digital sovereignty and cryptographic hygiene, Germany’s Federal Office for Information Security (Bundesamt für Sicherheit in der Informationstechnik, or BSI) has officially inducted three of the nation’s most prominent consumer email providers—GMX, WEB.DE, and mail.com—into the final round of its prestigious Email Security Hall of Fame.
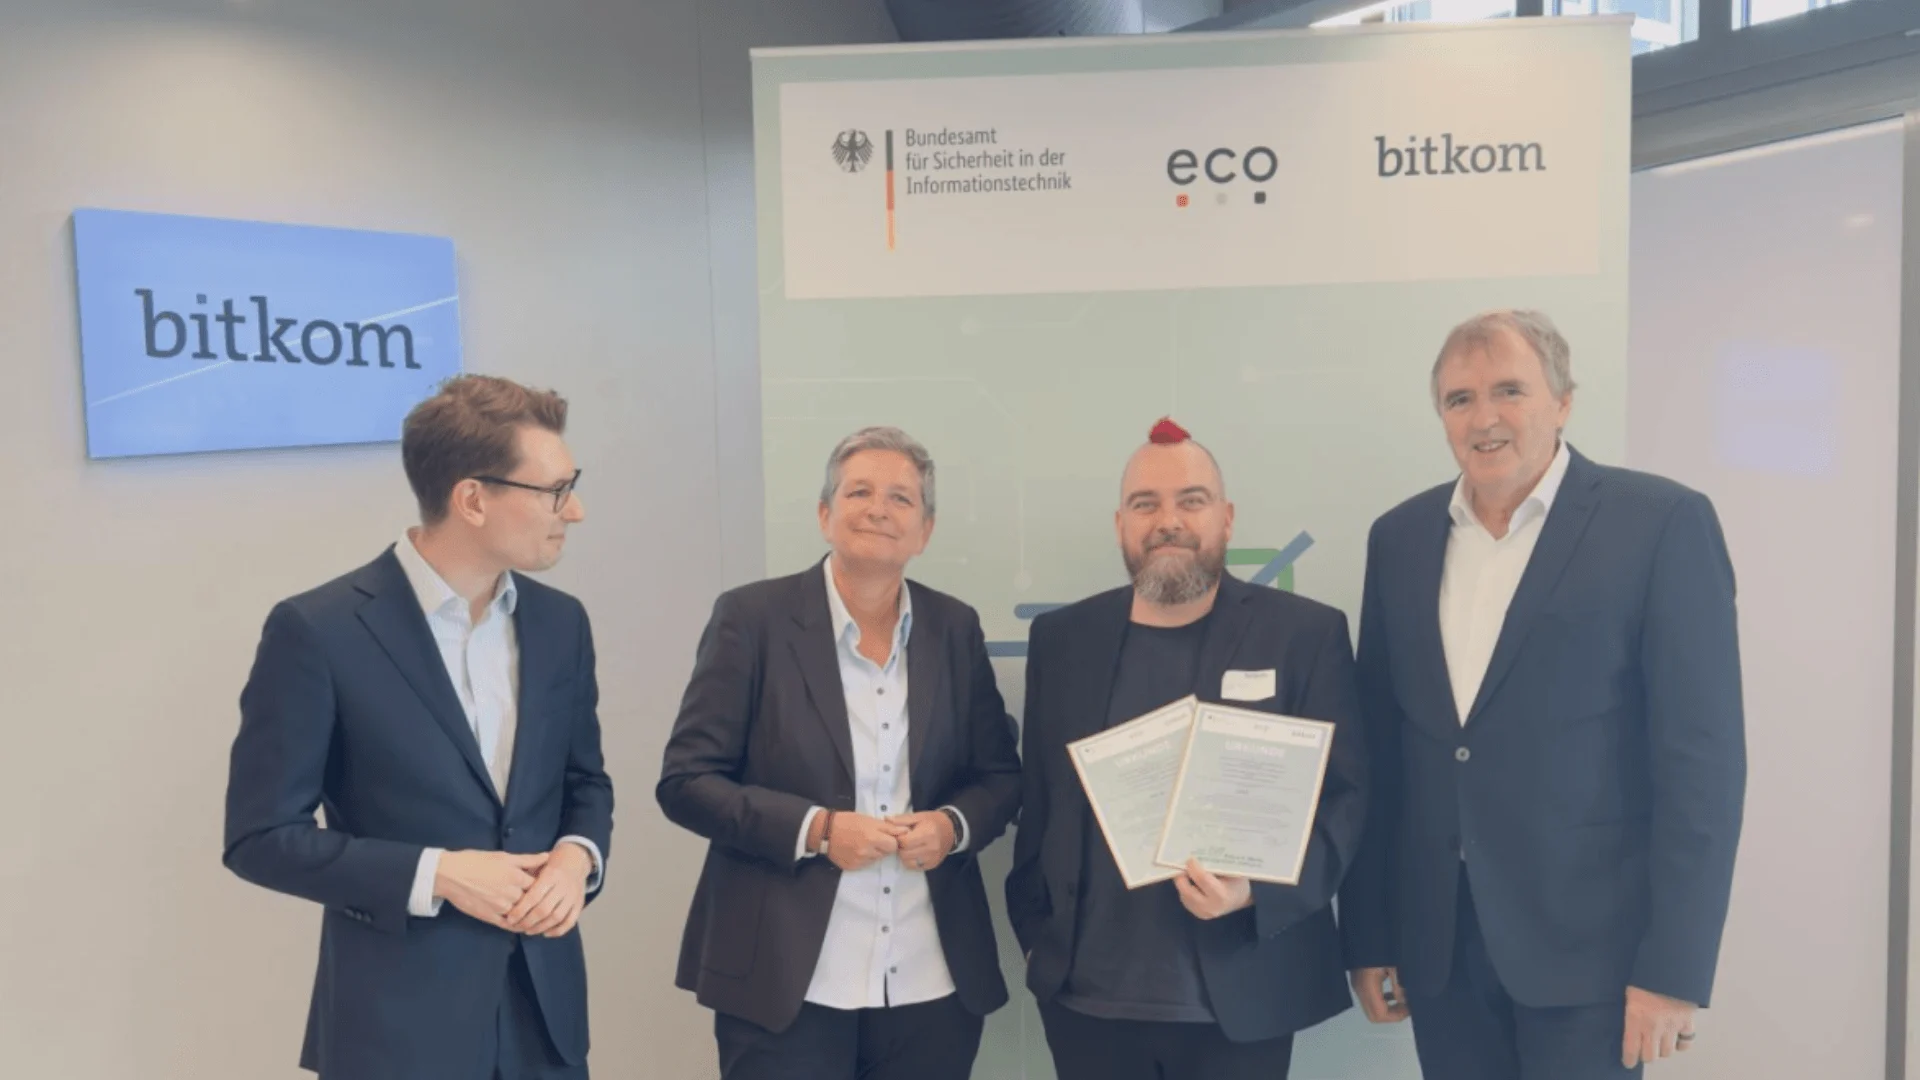
The announcement, which underscores a multi-year national campaign to harden Germany’s digital infrastructure against sophisticated cyber threats, was shared publicly on LinkedIn by Tobias Herkula of 1&1 Mail & Media. Herkula accepted the high-profile recognition on behalf of the parent company, marking the culmination of rigorous technical evaluations designed to separate security leaders from the rest of the pack.
While the inclusion in the Hall of Fame does not alter day-to-day spam filtering or anti-malware mechanics, the underlying technical mandates carry profound implications for institutional senders, multinational enterprises, and third-party mail transfer agents (MTAs) dispatching high-volume traffic into the German market.
Main Facts
The BSI’s recognition of GMX, WEB.DE, and mail.com is not merely an honorary badge; it is an official validation of compliance with rigorous national security standards. The overarching initiative is anchored in two foundational technical guidelines published by the BSI:
- TR-03108 (Secure Transport): Governs the encrypted transit of data across networks, ensuring that electronic mail cannot be easily intercepted or eavesdropped upon in transit.
- TR-03182 (Authentication): Establishes stringent frameworks to verify the identity of senders and domains, dramatically cutting down the viability of spoofing, phishing, and business email compromise (BEC).
In this second and final round of the Hall of Fame, the BSI raised the bar significantly. Unlike the initial phase—which relied heavily on organizational roadmaps, declarations of intent, and pledges to implement security roadmaps—the second round demanded concrete, verifiable technical proof. Most notably, entrants were required to have DNSSEC (Domain Name System Security Extensions) fully live and operational by June 30, 2026. The BSI independently verified these deployments, establishing a zero-tolerance policy for empty promises.
The Scorecard Breakdown
A closer look at the BSI’s public E-Mail-Checker diagnostic tool reveals the exact security posture of these platforms. GMX.de, for instance, achieved a stellar seven-out-of-seven rating across core cryptographic metrics:
- SPF (Sender Policy Framework): Fully operational.
- DKIM (DomainKeys Identified Mail): Fully operational.
- DMARC (Domain-based Message Authentication, Reporting, and Conformance): Fully operational.
- DNSSEC: Fully operational (the hard requirement for round two).
- DANE (DNS-based Authentication of Named Entities): Fully operational.
- TLS 1.2: Supported.
- TLS 1.3: Supported.
Interestingly, the public checker also flags three unweighted supplementary metrics as currently unmet: MTA-STS (Mail Transfer Agent Strict Transport Security), TLS reporting (TLS-RPT), and the complete decommissioning of legacy TLS versions older than 1.2.
For industry veterans who have operated consumer-grade mailbox services at scale, the lingering presence of legacy TLS support comes as little surprise. Consumer ecosystems are inextricably bound to legacy hardware, older mobile operating systems, and obsolete third-party clients that cannot handshake using modern cryptographic protocols. Forcing a hard cutoff on older TLS versions risks locking millions of everyday consumers out of their accounts, forcing providers to balance state-of-the-art security with absolute accessibility.
Chronology of the Initiative
The journey toward the Email Security Hall of Fame dates back to early 2025, a landmark period that the BSI officially designated as the "Email Security Year." Recognizing that electronic mail remains the lifeblood of business and personal communication—yet simultaneously one of the most vulnerable vectors for cybercrime—the German government partnered closely with major industry associations, specifically eco (Association of the Internet Industry) and Bitkom (Federal Association for Information Technology, Telecommunications and New Media).
Phase One: The Pledge and the Gold Standard (August 2025)
The campaign kicked off in earnest on August 22, 2025, when the BSI published its initial list of participants in the Email Security Hall of Fame.
- The First Wave: Approximately 150 organizations across Germany committed to implementing, or actively working toward, the BSI’s technical guidelines on secure transport (TR-03108) and authentication (TR-03182).
- Early Honors: During this initial rollout, consumer giants GMX and WEB.DE distinguished themselves by achieving Gold status, proving that their internal security roadmaps were already well ahead of the national curve.
Phase Two: Verification and the Final Curtain (2026)
As the campaign progressed into its second and final phase, the BSI transitioned from voluntary compliance to strict technical audits.
- The June 30 Deadline: Entrants were given a hard deadline of June 30, 2026, to bring complex infrastructure like DNSSEC live. The BSI conducted active audits to verify that these systems were functioning correctly in production environments.
- The Finale: With the conclusion of this second round, the BSI has officially closed the Email Security Hall of Fame program, declaring it the final chapter of this specific targeted awareness campaign. Going forward, these standards are expected to transition from special initiative markers to baseline operational expectations for the German digital market.
Supporting Data & Technical Architecture
To fully appreciate the weight of the BSI’s recognition, one must examine the underlying protocols that secured GMX, WEB.DE, and mail.com their spots in the Hall of Fame. Email, by design, is an inherently insecure protocol born in an era of academic trust. Modern secure email relies on an intricate stack of cryptographic safeguards to establish authenticity and confidentiality.
| Protocol / Standard | BSI Requirement Status | Function in Modern Email Security |
|---|---|---|
| SPF | Mandatory (TR-03182) | Lists authorized IP addresses permitted to send mail on behalf of a domain. |
| DKIM | Mandatory (TR-03182) | Adds a cryptographic signature to emails, verifying that the content was not altered in transit. |
| DMARC | Mandatory (TR-03182) | Uses SPF and DKIM to determine email authenticity, specifying instructions on how to handle failures. |
| DNSSEC | Mandatory (Round 2) | Protects DNS records from man-in-the-middle attacks and cache poisoning by digitally signing DNS data. |
| DANE | Core Metric (7/7 Score) | Associates X.509 certificates with DNS records using DNSSEC, preventing fraudulent TLS certificates. |
| TLS 1.2 / 1.3 | Core Metric (7/7 Score) | Encrypts data in transit between mail servers, preventing eavesdropping and tampering. |
The Significance of DANE for Senders
For everyday users, the implementation of these protocols translates to a safer inbox with significantly fewer phishing scams slipping through the cracks. However, for corporate senders, marketing platforms, and transactional email service providers, the widespread adoption of DANE (DNS-based Authentication of Named Entities) by German heavyweights carries a direct operational directive.
DANE bridges the gap between DNS and transport-layer encryption. When a sending Mail Transfer Agent (MTA) attempts to deliver a message to a DANE-enabled receiving domain like GMX or WEB.DE, the sending MTA must be capable of inspecting and validating the receiving domain’s TLSA records via DNSSEC.
If an organization dispatches high-volume traffic into Germany and its sending infrastructure does not support or check DANE/DNSSEC validation paths, delivery friction can occur. As the German digital ecosystem hardens its borders, legacy mail servers configured with weak or outdated cryptographic setups risk delayed delivery, routing failures, or outright rejection. Implementing robust outbound DANE verification is no longer an optional "nice-to-have" for international senders—it is rapidly becoming a cost of doing business in Europe.
Official Responses and Industry Stakeholder Perspectives
The inclusion of 1&1 Mail & Media’s flagship brands in the BSI Hall of Fame drew enthusiastic reactions from corporate leadership, who framed the award as validation of years of heavy engineering investments.
Posting on professional networking platform LinkedIn, Tobias Herkula of 1&1 Mail & Media expressed immense pride upon accepting the recognition on behalf of the company:
"We are thrilled to see GMX, WEB.DE, and mail.com recognized in the final round of the BSI’s Email Security Hall of Fame. This milestone reflects our unwavering commitment to protecting our users’ privacy and raising the bar for cryptographic security across the European email landscape. Securing millions of consumer mailboxes requires continuous, rigorous engineering, and this acknowledgment from the BSI validates our team’s relentless dedication."
From the regulatory side, representatives from the BSI emphasized that the campaign was designed to mobilize the private sector into closing security gaps that malicious actors routinely exploit. By setting unambiguous benchmarks—such as the mandatory deployment of DNSSEC by mid-2026—the German government has sought to create a rising tide that lifts the security posture of the entire national internet infrastructure.
Industry analysts note that while government-backed initiatives like the Email Security Hall of Fame do not carry direct punitive fines for non-compliance, they exert powerful market pressure. Consumer awareness in Germany regarding data privacy and cybersecurity is notoriously high. Brands that fail to meet these gold standards risk losing consumer trust, while certified providers like GMX and WEB.DE solidify their competitive edge as trusted guardians of personal data.
Implications for the Future of European Digital Communication
The conclusion of the BSI’s Email Security Hall of Fame marks the end of a unique regulatory campaign, but it signals the acceleration of a broader trend: the mandatory hardening of digital communications infrastructure across the European Union.
1. Pressure on International Senders
For global enterprises sending marketing newsletters, transactional notices, or customer service emails into Germany, the writing is on the wall. With domestic giants enforcing strict cryptographic standards backed by the national cybersecurity authority, foreign senders must audit their email infrastructure. Companies operating obsolete mail transfer agents or neglecting DNSSEC and DANE implementations will find their deliverability rates steadily degrading in the German market.
2. The Privacy and Trust Dividend
In an era dominated by automated phishing campaigns, credential stuffing, and state-sponsored cyber espionage, consumer trust is fragile. By aligning their technical architectures with BSI guidelines, providers like GMX, WEB.DE, and mail.com reinforce their value proposition to privacy-conscious European consumers who are increasingly skeptical of foreign tech monopolies.
3. A Blueprint for Global Regulation
The BSI’s methodology—combining voluntary industry partnerships (with eco and Bitkom), clear technical guidelines (TR-03108 and TR-03182), public diagnostic tools (E-Mail-Checker), and hard verification deadlines—serves as a compelling blueprint for other national cybersecurity agencies worldwide. Rather than relying solely on heavy-handed legislation, the German model successfully gamified and incentivized cybersecurity excellence, culminating in a transparent Hall of Fame that clearly distinguishes secure operators from laggards.
As the digital landscape evolves, the bar set by GMX, WEB.DE, and mail.com will no longer be considered an elite achievement, but rather the absolute minimum baseline for secure electronic communication in the 21st century.