In the ever-escalating arms race between cybersecurity defenders and threat actors, a worrying paradigm shift is underway. Three distinct pieces of threat intelligence research published during the first fortnight of September exposed a new generation of sophisticated phishing campaigns.
While their execution methods vary widely—ranging from invisible Unicode manipulations and ephemeral memory-based phishing pages to advanced phishing-as-a-service platforms—these attacks share a singular, highly effective strategy: they completely bypass traditional authentication hurdles by routing through channels, infrastructure, and endpoints that the recipient and automated filters already inherently trust.
By weaponizing legitimate cloud services, exploiting the architecture of modern web browsers, and tricking text-parsing security filters, these campaigns highlight critical vulnerabilities in the modern enterprise security stack. This in-depth report breaks down the anatomy of these attacks, the chronology of their discovery, supporting technical data, official responses, and the profound implications for organizations and service providers alike.
Main Facts: The Anatomy of Modern Evasion
Modern phishing has evolved past obvious spelling errors, sketchy foreign domains, and easily blockable IP addresses. Today’s threat actors rely heavily on "living off the cloud" and exploiting the blind spots of automated text analysis and security scanners.
The recent research highlights three primary vectors of concern:
- ASCII and Unicode Smuggling: Threat actors are splicing invisible Unicode tag characters into email text. This tricks automated keyword filters into seeing benign words while rendering human-readable phrases that successfully lure victims.
- Serverless Phishing (Blob URLs): Attackers are utilizing legitimate enterprise services (such as Microsoft OAuth and Teams) combined with browser-native features (Blob URLs) to render credential-harvesting pages dynamically inside the victim’s local memory. No static phishing site ever exists on a remote server for security scanners to index or block.
- Phishing-as-a-Service (PaaS) with Active Malleable Defenses: Operations like the "BigBear 2.0" framework are democratizing advanced attacks. Leveraging platforms like Evilginx2, these kits actively target and disable robust authentication methods, such as FIDO2 security keys, forcing users back onto weaker, interceptable factors.
Crucially, in all three scenarios, email authentication protocols like SPF, DKIM, and DMARC remain entirely intact. Because the messages originate from reputable, legitimate cloud infrastructure, traditional reputation-based filters struggle to separate malicious traffic from legitimate business correspondence.
Chronology of the September Disclosures
The first two weeks of September delivered a masterclass in coordinated threat disclosure, mapping out an interconnected ecosystem of sophisticated cyberattacks.
September 3: Microsoft Exposes ASCII Smuggling
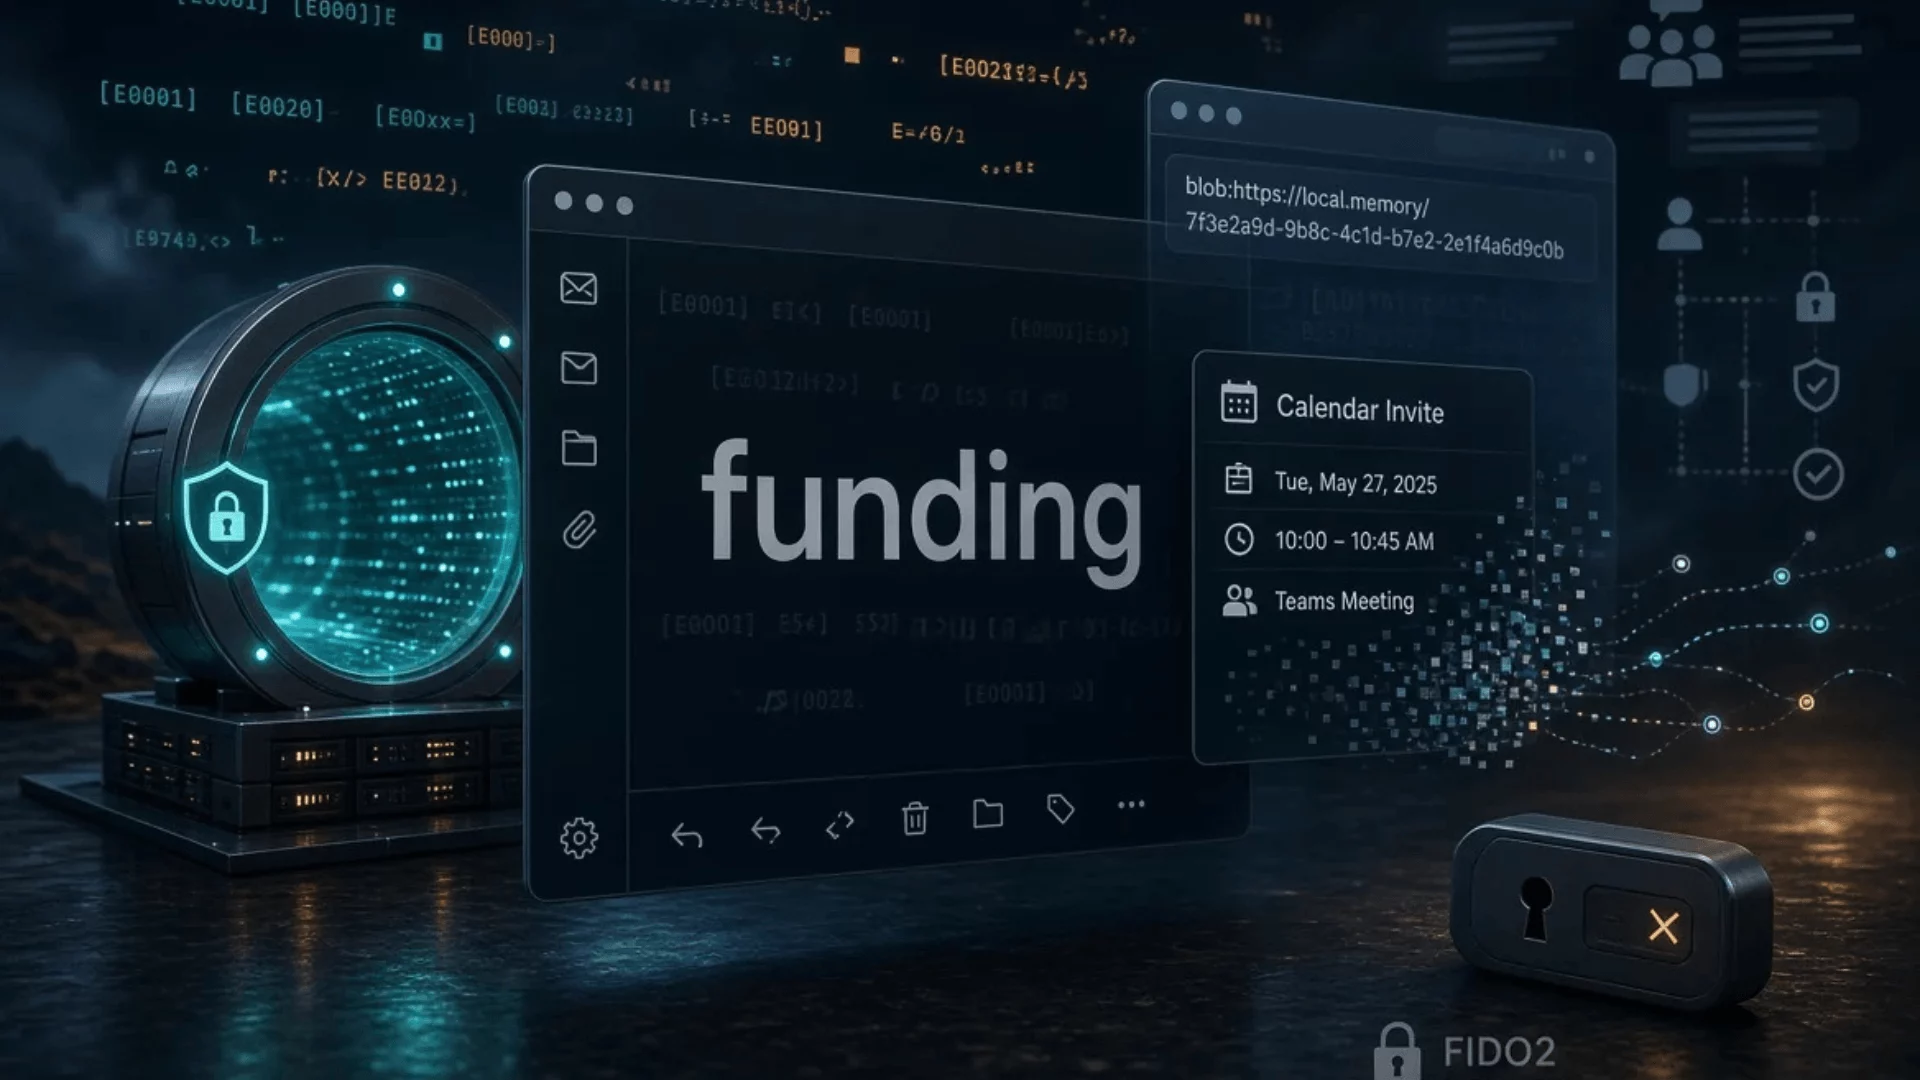
Microsoft’s security research team published an advisory detailing a novel evasion technique dubbed "ASCII smuggling" (crossing over from AI prompt-injection research into real-world phishing). The campaign systematically leveraged invisible Unicode tag characters (specifically code points U+E0000 to U+E007F) embedded within email subject lines and body copy. Routed through the legitimate marketing automation platform ActiveCampaign, the campaign demonstrated a calculated, weekday-heavy sending schedule that peaked in late February.
September 7: CloudSEK Uncovers "BigBear 2.0"
Following Microsoft’s disclosure, threat intelligence firm CloudSEK published findings regarding "BigBear 2.0," a turnkey Phishing-as-a-Service (PaaS) platform built on top of the Evilginx2 framework. Having gained administrative access to a BigBear panel, CloudSEK researchers exposed an operation featuring thousands of harvested credentials, active MFA bypasses, and custom scripts designed specifically to degrade user authentication standards. This infrastructure served as the backend monetization engine for lures distributed via trusted messaging channels.
September 9: Barracuda Discloses Memory-Only Phishing
Rounding out the fortnight, Barracuda Networks revealed a campaign that bypassed traditional URL blocking entirely. Utilizing a DocuSign lure embedded with a calendar invite, the attack chained Microsoft OAuth and Teams redirects to load an external resource. The victim’s browser converted this resource into a temporary Blob URL, rendering the phishing interface entirely within local memory.
Supporting Data and Technical Mechanics
To understand why these attacks are proving so devastatingly effective, one must examine the underlying mechanics and empirical data gathered by security researchers.
The Numbers Behind ActiveCampaign’s Lures
Microsoft’s telemetry on the Unicode-smuggling campaign revealed a highly organized, industrial-scale operation:
- Volume: Weekday message volumes consistently ranged between 1 million and 2.37 million messages, experiencing a sharp peak on February 26.
- Cadence: The campaign went nearly silent on weekends, mirroring standard corporate business hours—a hallmark of automated, scheduled bulk-sending infrastructure.
- Sender Spoofing: On February 9 alone, researchers identified 148 distinct finance-themed sender domains. These domains were synthetic recombinations of a narrow vocabulary (e.g., variations of guardiangrowthfunding).
- Infrastructure Footprint: Envelope senders followed a predictable pattern (
em-<digits>.<brand-domain>), with a small pool of reused account numbers fanned out across hundreds of unique brand domains. Links were automatically wrapped in ActiveCampaign’s legitimate tracking domains. - IP Concentration: Approximately 92% of the measured message volume originated from a single
/24network block belonging to the ActiveCampaign platform.
The Mechanics of ASCII Smuggling
The brilliance—and danger—of ASCII smuggling lies in the discrepancy between how machines and humans process text.
If an attacker wants to bypass a security filter flagging the word "funding," they can split the word in the raw HTML source code using invisible Unicode tag characters:
- Raw input:
fun+[TAG SPACE]+ding - Machine reading (naive parser): Flags the unexpected control characters or misses the pattern entirely.
- Human reading: The browser renders the string seamlessly as "funding".
Microsoft noted that while the evasion technique was clever, it ultimately had a narrow success rate against layered defenses. Over 99% of the malicious messages were caught by subsequent layers within Microsoft Defender. However, organizations relying solely on basic signature or keyword filters were routinely blinded.
The Ghost in the Machine: Blob URLs
Barracuda’s disclosure highlighted a terrifying leap forward in evasion: the phishing page that never exists on a server.
When a victim clicked the link in the DocuSign-themed calendar invite, they were routed through legitimate Microsoft OAuth and Teams infrastructure. This directed the browser to load an external resource (cdn.bloom[.]io).
Instead of downloading a traditional HTML file from a malicious server, the browser converted the payload into a Blob URL—a Uniform Resource Identifier that points to data stored locally in the browser’s volatile memory. Because no physical file or static landing page ever touched a web server, traditional web crawlers, URL scanners, and static blocklists were rendered completely useless. Once loaded, the page registered a service worker, turning the victim’s own browser into an interactive proxy controlled by the attacker’s backend.
Official Responses and Industry Guidance
As these sophisticated techniques came to light, affected platforms and security vendors moved quickly to issue guidance and clarify their positions.
ActiveCampaign’s Response
ActiveCampaign engaged with Microsoft prior to the publication of their research. In an official statement, the platform noted that it continuously tests emerging evasion techniques against its internal content moderation engines. ActiveCampaign stated that messages utilizing invisible Unicode receive the same automated verdicts as their plain-text equivalents, and that anomalous, heavy reliance on such formatting is flagged as suspicious behavior.
Furthermore, security experts have issued a stern warning regarding defensive overreaction. Because the tracking domains and /24 IP blocks utilized in these campaigns are shared by every legitimate customer on the ActiveCampaign platform, security teams are strongly advised not to implement blanket IP or domain blocks. Doing so would inadvertently sever critical legitimate newsletters, transactional alerts, and business communications.
Defensive Recommendations from Microsoft and Barracuda
Security architects have outlined several critical hardening steps to counter these multi-layered threats:
- Filter Normalization: Organizations running their own email security gateways must implement text normalization before running detection signatures. Security filters should automatically strip tag-block and zero-width characters from subject lines and email bodies. The presence of these characters should then be treated as an immediate anomaly signal. (Note for rule writers: Care must be taken, as legitimate emoji encodings for regions like England, Scotland, and Wales utilize tag characters and can trigger false positives).
- Full Click-Path Link Inspection: Traditional email filters that merely check the initial URL destination are no longer sufficient. Enterprise email security solutions must follow the complete redirect chain, analyzing OAuth grants and cloud-app integrations.
- Phishing-Resistant MFA: Given that advanced PaaS kits like BigBear 2.0 explicitly employ custom JavaScript to disable or downgrade FIDO2 security keys, organizations must enforce mandatory, hardware-token-based phishing-resistant Multi-Factor Authentication (MFA) that cannot be bypassed via token-hijacking or adversary-in-the-middle (AitM) proxies.
Implications for the Cybersecurity Landscape
The convergence of AI-derived evasion tactics, trusted cloud delivery networks, and memory-based execution has profound implications for the future of digital defense.
First, the erosion of reputation-based filtering is accelerating. For decades, security teams relied on the foundational assumption that mail originating from reputable platforms (like ActiveCampaign, Salesforce, or Microsoft 365) with valid SPF, DKIM, and DMARC records was inherently trustworthy. Threat actors have weaponized this trust, transforming legitimate SaaS infrastructure into automated delivery vehicles for malicious payloads. Security systems must evolve beyond simple sender reputation scoring toward granular behavioral analytics and content inspection.
Second, the perimeter has dissolved entirely into the endpoint. When a phishing page materializes out of thin air inside a browser’s local memory via a Blob URL, network-level perimeters and static web filters become obsolete. Defense must shift toward the browser itself—implementing enterprise browser isolation, strict content security policies (CSPs), and real-time behavioral monitoring of client-side script execution.
Finally, the democratization of attacks through platforms like BigBear 2.0 proves that cybercrime is operating with enterprise-grade efficiency. As long as threat actors can lease sophisticated infrastructure, bypass multi-factor authentication, and hide behind the digital exhaust of legitimate cloud providers, organizations must adopt a zero-trust posture that questions not just the sender, but the very medium through which trust is established.