Executive Summary
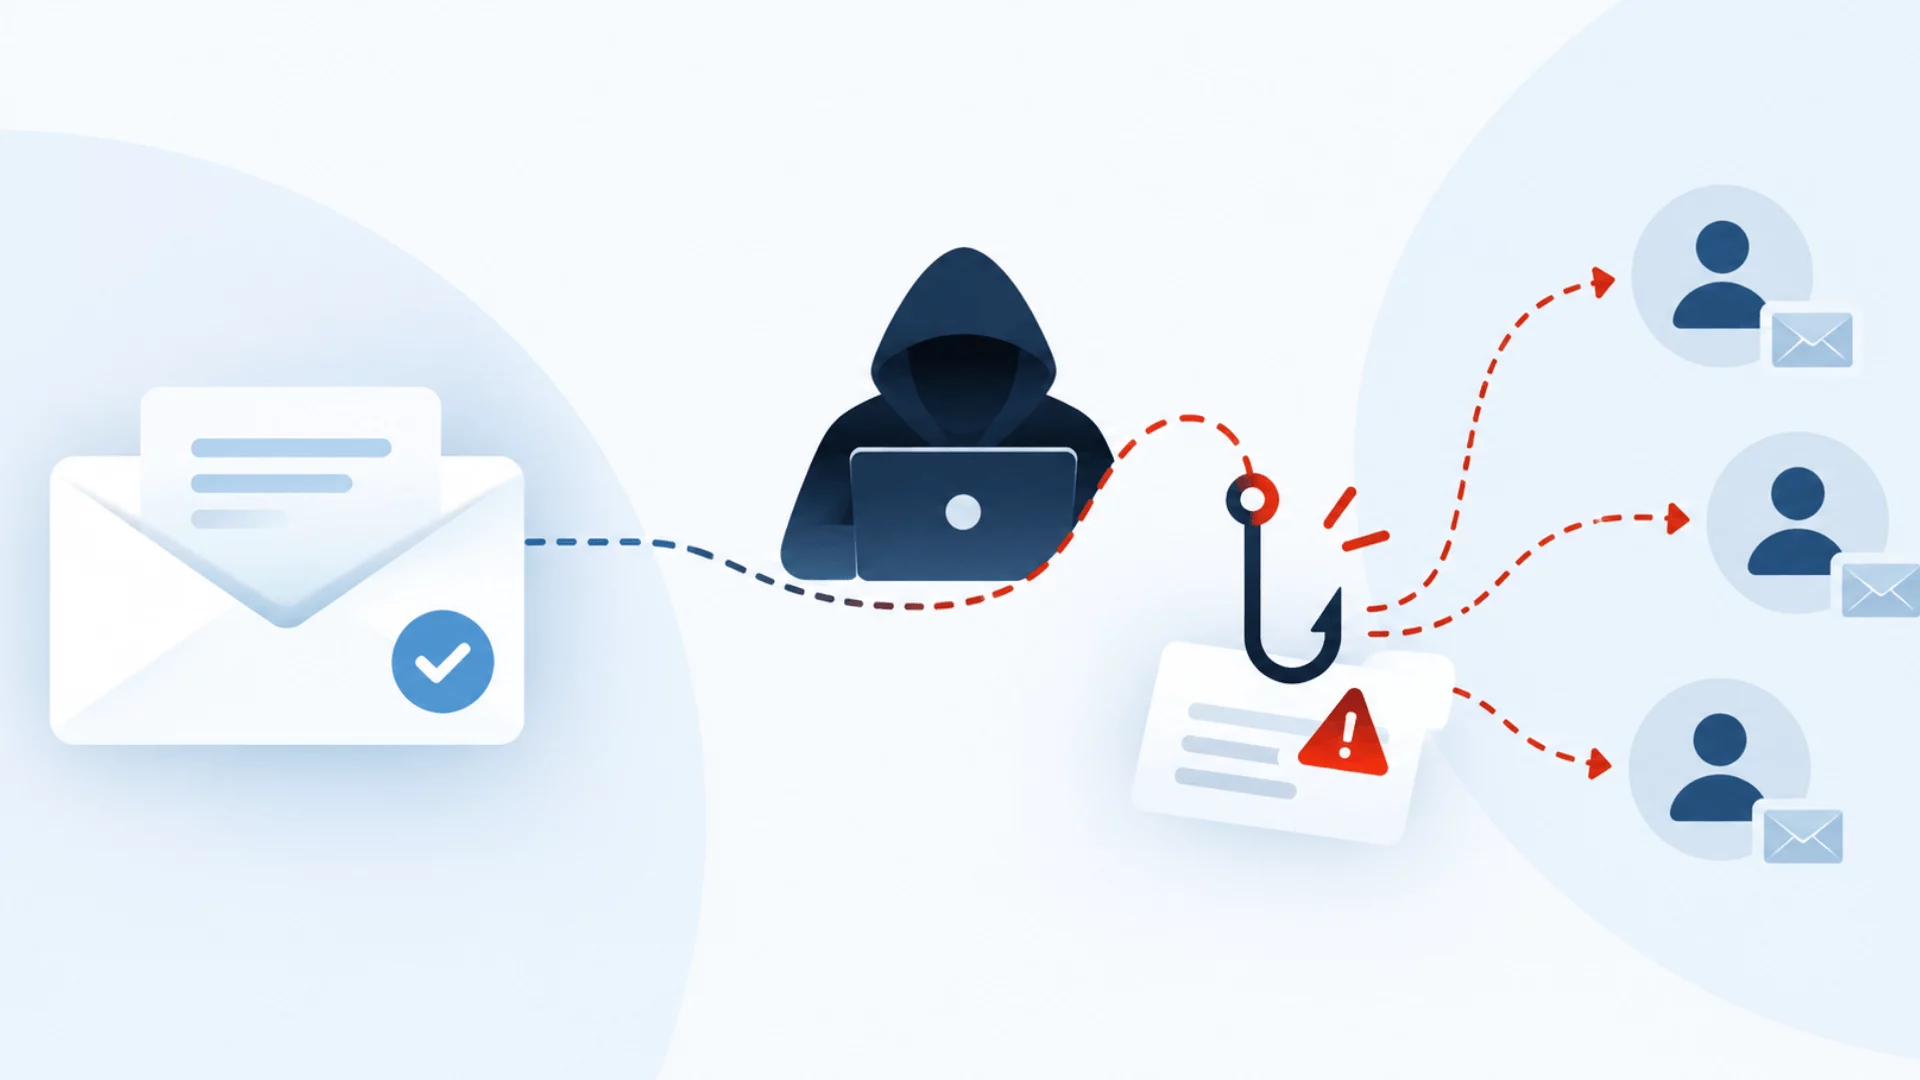
In an alarming security breach that underscores the profound limitations of modern email authentication protocols, customer engagement platform Brevo has disclosed a cyberattack affecting 138 customer accounts. The incident, stemming from a critical authorization flaw in the company’s handling of Security Assertion Markup Language (SAML) single sign-on (SSO), allowed malicious actors to hijack corporate sending infrastructure. By bypassing traditional perimeter defenses entirely, the attackers weaponized trusted communication channels to distribute convincing phishing campaigns targeting high-profile cryptocurrency and hardware wallet communities, including prominent industry players Trezor and CoinTracking.
While Brevo acted swiftly to neutralize the vector within two hours of detection, the incident serves as a stark wake-up call for the cybersecurity and digital marketing sectors. It illustrates a worst-case scenario: when authentication mechanisms validate the message pipeline rather than the user’s intent, legitimate infrastructure becomes the ultimate Trojan horse.
Main Facts: The Anatomy of the Brevo Compromise
The security incident at Brevo—formerly known as Sendinblue—revolves around a fundamental architectural oversight in multi-tenant identity federation. Rather than exploiting a traditional malware vector, zero-day operating system vulnerability, or brute-force credential stuffing attack, the threat actor executed a logic abuse exploit targeting SAML SSO configurations.
The Attack Vector: SAML Authorization Flaw
According to Brevo’s post-incident technical write-up, the attacker initiated the sequence by establishing a standard, legitimate account on the Brevo platform. They subsequently configured this rogue account to utilize SAML single sign-on via an identity provider (IdP) completely under their administrative control.
The critical vulnerability, however, lay not in the creation of the IdP, but in the post-authentication scoping mechanism. When the attacker invited legitimate, unaffiliated Brevo users into their organization environment, those users authenticated via standard corporate credentials. Because Brevo’s access control logic failed to properly isolate permissions to the specific organization where the SSO had been established, successful authentication granted the attacker unauthorized lateral reach. Specifically, the threat actor gained access to every other distinct organization that the invited, unsuspecting users already had administrative or operational privileges over.
Scope of the Breach
Brevo’s formal disclosures indicate that the compromise directly impacted 138 customer accounts. A granular breakdown provided by the company outlines the following telemetry:
- Active Phishing Deployment: Exactly 6 accounts were actively utilized to orchestrate and dispatch unauthorized, malicious emails using Brevo’s legitimate outbound messaging infrastructure.
- Data Exfiltration: Contact and subscriber lists were systematically exported from 43 accounts.
- Dormant Access: The remaining 93 accounts showed no meaningful attacker activity or data exfiltration, though they remained technically accessible during the breach window.
Data Reconciliation Discrepancies
Industry analysts and security researchers have noted mathematical inconsistencies within Brevo’s official figures. When summing the subsets provided by the company—6 accounts used for phishing, 43 accounts subjected to data export, and 93 accounts showing no activity—the total reaches 142. This exceeds Brevo’s stated aggregate of 138 affected accounts by four.
This discrepancy strongly implies an administrative overlap, where specific accounts experienced both data export and active phishing manipulation, or where multi-faceted exploitation occurred. Compounding these reporting variances, hardware wallet manufacturer Trezor published an independent assessment citing 120 affected accounts within its internal post-mortem. These divergent metrics highlight the inherent forensic complexities organizations face when attempting to scope multi-tenant cloud compromises in real time.
Chronology of the Incident: A Two-Hour Window of Exposure
Understanding the precise timeline of the Brevo security incident demonstrates how rapidly modern cyberattacks unfold, as well as the efficacy of rapid-response mitigation protocols when automated telemetry triggers alert mechanisms.
September 10: Detection and Remediation
- 06:30 UTC: Brevo’s security monitoring and anomaly detection systems identified unauthorized behavioral patterns and anomalous SSO manipulation. Incident response protocols were immediately initiated to triage the scope of the breach.
- 08:30 UTC: Exactly two hours after initial detection, Brevo engineering and security teams deployed an emergency mitigation that effectively closed the exploit vector. Concurrently, the platform forced the termination of all active user sessions globally, requiring all customers to re-authenticate and severing the attacker’s persistent footholds.
- Post-Remediation Status: Brevo reports zero subsequent attacker activity or persistent unauthorized access following the 08:30 UTC session revocation. Concurrently, the company initiated the deployment of a permanent structural fix designed to enforce strict permission boundaries, ensuring that SAML SSO access rights are immutably tied exclusively to the organization owning the specific configuration.
Supporting Data and Real-World Impact: The Trezor and CoinTracking Breaches
The most visible and damaging fallout from the Brevo compromise manifested through targeted attacks on high-value cryptocurrency ecosystems. Because the threat actors leveraged Brevo’s authenticated sending infrastructure, they bypassed the exact security filters that protect users from fraudulent communications.
Trezor: The STM32 Entropy Vulnerability Campaign
Hardware wallet pioneer Trezor confirmed that its third-party Brevo account was successfully compromised during the incident. Utilizing Trezor’s legitimate infrastructure, the attackers launched a highly targeted phishing campaign aimed at the company’s opt-in newsletter subscriber base, which totaled 347,149 email addresses.
- The Phishing Lure: The malicious correspondence was cleverly disguised under the heading, "Critical Security Alert: STM32 Entropy Vulnerability." The email directed recipients to a meticulously crafted, fraudulent application interface designed to trick users into divulging their cryptographic wallet backup phrases (seed phrases).
- Mitigation and Metrics: Trezor’s internal security operations center detected the anomalous outbound volume and successfully blacklisted the malicious campaign domain at the DNS level within 20 minutes of deployment. Despite this rapid containment, telemetry indicates that approximately 2,500 individuals clicked the fraudulent link before DNS propagation completed.
- Collateral Safety: Trezor explicitly confirmed that no proprietary Trezor products, physical hardware wallets, or backend account management systems were accessed, compromised, or impacted by the incident.
CoinTracking: The API Key Refresh Ploy
Cryptocurrency portfolio manager and tax reporting service CoinTracking also fell victim to the infrastructural hijacking. The platform confirmed that unauthorized actors dispatched a fraudulent notification bearing the subject line, "Data Breach Notice: Please refresh API Keys as soon as possible."
Similar to the Trezor campaign, the email was designed to induce panic and manipulate users into handing over sensitive account credentials or API tokens that could grant third-party access to exchange portfolios. CoinTracking verified that while the email originated from their legitimate Brevo delivery pipeline, all internal systems, customer passwords, user API keys, and private portfolio datasets remained entirely secure and uncompromised.
Official Responses and Remediation Efforts
Both the service provider and the affected enterprise clients have issued detailed public statements regarding the incident, emphasizing transparency and institutional hardening.
Brevo’s Corrective Measures
Brevo’s engineering leadership moved quickly to reassure its broader customer base. Beyond terminating all active sessions at the time of discovery, the company instituted sweeping internal audits of its authentication pipelines.
The permanent architectural patch deployed in the wake of the incident fundamentally redesigns how SAML SSO assertions are evaluated. Under the new parameters, identity provider sessions cannot inherit cross-organizational privileges. Even if a user account holds administrative access across multiple distinct corporate tenants within Brevo, an SSO session initialized via one IdP is strictly sandboxed to prevent lateral movement or administrative privilege escalation into secondary environments.
Enterprise Accountability
Affected organizations like Trezor and CoinTracking utilized their respective corporate blogs to communicate directly with their user bases, providing clear educational guidance on how to spot the fraudulent communications and reiterating foundational security hygiene—such as never entering seed phrases or private keys into web-based applications. Both entities praised the relative speed with which Brevo communicated the breach, while noting the discrepancies in account tallying as a reminder of the complex data forensics required during third-party cloud incidents.
Implications: The Death of Traditional Email Authentication Trust
The Brevo security incident serves as a profound case study for the email deliverability, cybersecurity, and zero-trust architecture communities. It exposes a foundational philosophical and technical limitation in how organizations evaluate digital trust.
Authenticated Does Not Mean Safe
For decades, the information security community has trained users, email administrators, and automated spam filters to rely on cryptographic authentication protocols to verify message legitimacy:
- SPF (Sender Policy Framework): Verifies which mail servers are authorized to send email on behalf of a domain.
- DKIM (DomainKeys Identified Mail): Adds a cryptographic signature to emails, proving the message was not altered in transit and genuinely originated from the claimed domain.
- DMARC (Domain-based Message Authentication, Reporting, and Conformance): Unifies SPF and DKIM to provide instructions on how receiving mail servers should handle failures.
While these protocols are vital for blocking spoofing, phishing, and domain impersonation, the Brevo incident demonstrates that they are utterly blind to intent.
When an advanced threat actor successfully compromises a legitimate user account and gains authorized access to an authenticated outbound mail server, every single trust signal remains fully intact. SPF checks pass seamlessly because the sending server is officially listed in the domain’s DNS records. DKIM signatures are mathematically valid because the infrastructure itself signs the message. DMARC policies register a "pass" because the cryptographic alignment is technically flawless.
To a receiving mail server, a mailbox provider, and an end-user security gateway, the malicious phishing email is indistinguishable from a legitimate marketing campaign or password reset notification sent by the company itself.
The Rise of Identity-Centric Supply Chain Attacks
As perimeter defenses, endpoint detection and response (EDR) agents, and advanced email gateways (AEGs) become increasingly sophisticated at blocking external threats, malicious actors are pivoting toward identity-based supply chain attacks.
By exploiting logic flaws in single sign-on frameworks—which are widely adopted by enterprises to streamline access and enhance security—attackers can bypass traditional vulnerability scanning altogether. They do not need to exploit a software bug; they simply abuse authorized administrative pathways.
Lessons for the Enterprise
The Brevo breach offers vital takeaways for organizations relying on cloud-based marketing and customer engagement platforms:
- The Need for Strict Tenant Isolation: Multi-tenant SaaS providers must implement rigorous, least-privilege scoping for single sign-on implementations, ensuring that federated credentials can never bridge distinct organizational boundaries.
- Behavioral Monitoring Beyond Perimeters: Security teams must monitor not just how a message is authenticated, but who is driving the pipeline. Unusual export volumes, sudden spikes in contact list downloads, and anomalous sending patterns from administrative accounts must trigger automated interlocks.
- End-User Awareness: Because authenticated phishing bypasses technical filtering, the final line of defense remains the critical thinking of the end recipient. Organizations must continue educating users that even emails passing all standard cryptographic checks can originate from compromised corporate channels.
Conclusion
The security incident at Brevo is much more than a routine disclosure of a software bug; it is a clinical demonstration of the vulnerability inherent in modern cloud ecosystems. As threat actors continue to weaponize trusted infrastructure against enterprises and their customers, platform providers must adopt uncompromising zero-trust architectures that treat every authentication token, identity federation, and cross-organization permission with maximum skepticism. Until then, legitimate infrastructure will remain one of the most dangerous weapons in an attacker’s arsenal.