By Cybersecurity Desk
Published: August/September 2026
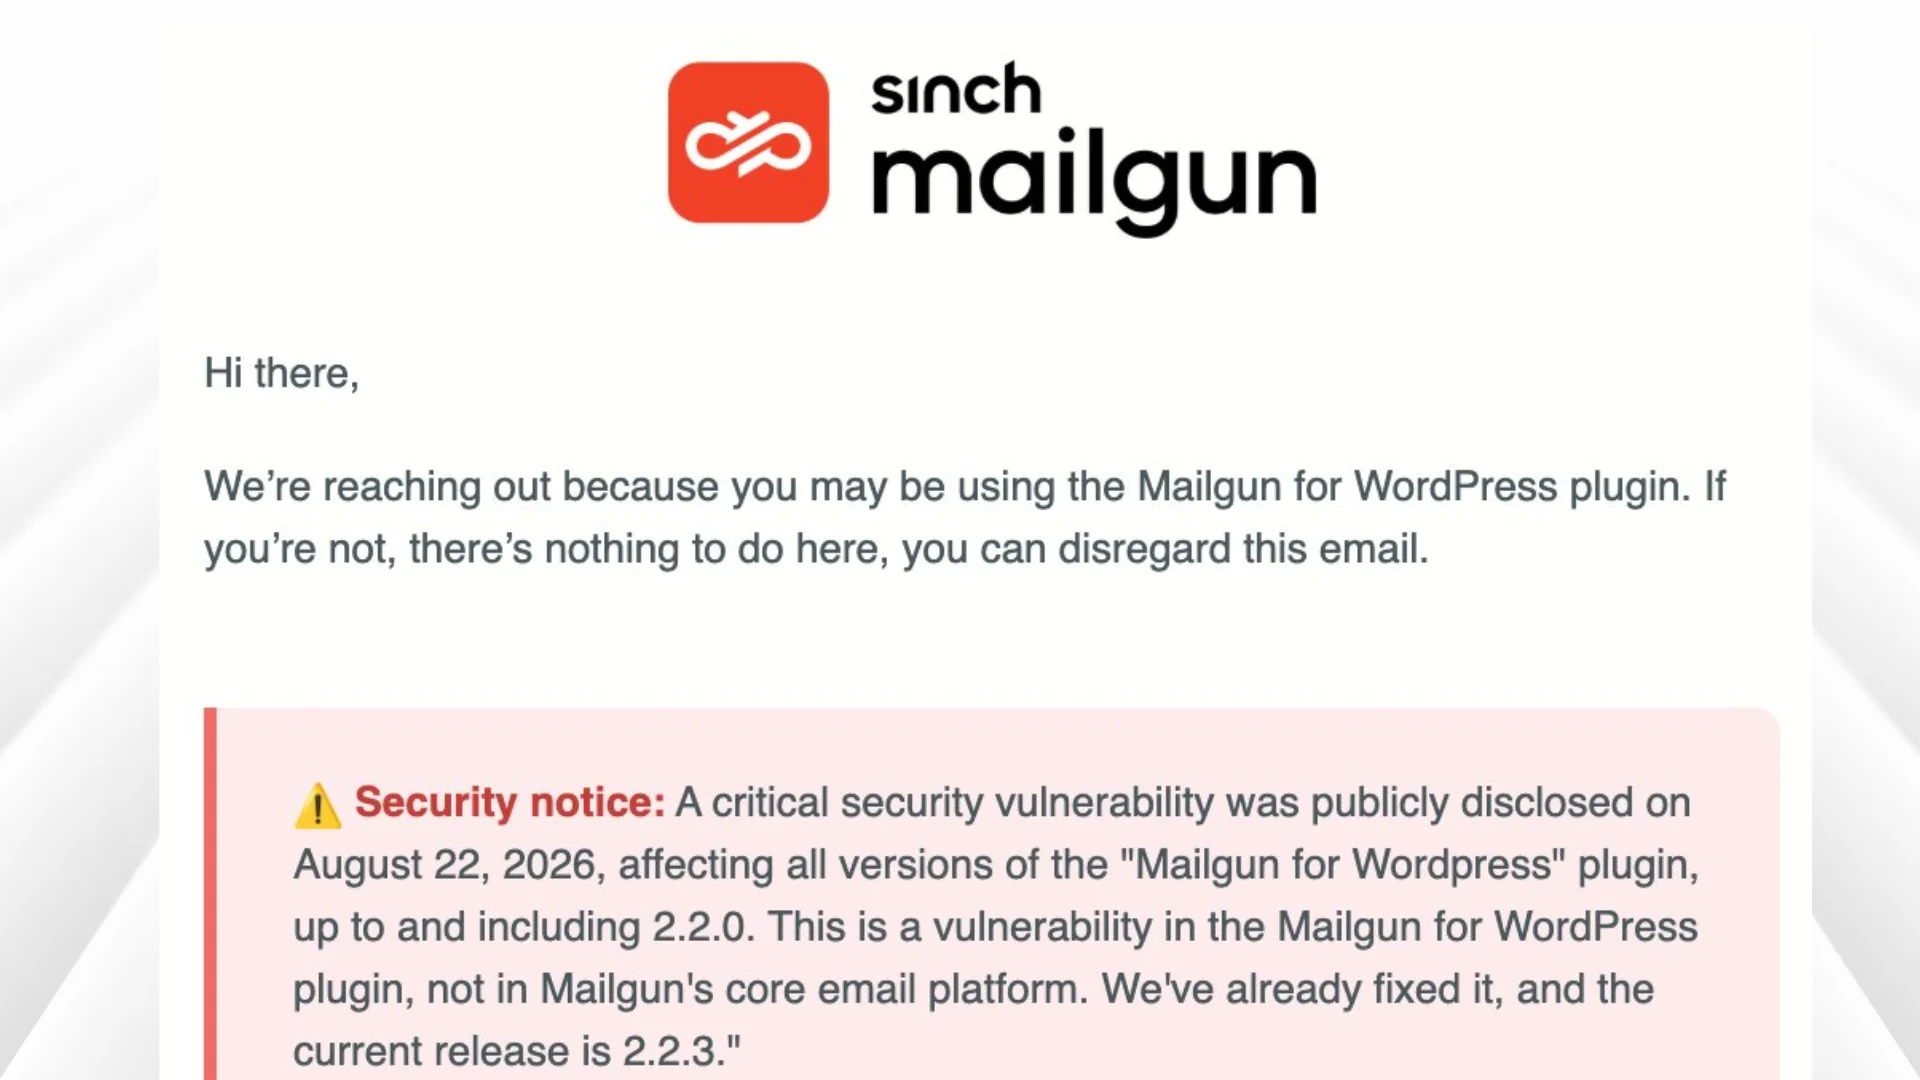
Website administrators running the popular Mailgun for WordPress plugin are being urged to verify their installations immediately following the disclosure of a critical Server-Side Request Forgery (SSRF) vulnerability. Tracked as CVE-2026-78003, the flaw carries a near-maximum Common Vulnerability Scoring System (CVSS) rating of 9.8 out of 10, signaling extreme severity.
The security hole allows unauthenticated remote attackers to weaponize a victim website’s stored Mailgun API key, directing it toward arbitrary Mailgun API endpoints. Because the plugin requires API permissions that often extend to routing and domain management, successful exploitation can lead to mail interception, inbound route manipulation, and ultimately, complete administrative account takeovers across affected WordPress platforms.
With more than 80,000 active installations worldwide, the potential surface area for exploitation is vast. While a patch has been available since July, security researchers warn that ambiguous changelog notes may have caused many webmasters to deprioritize the update, leaving thousands of sites dangerously exposed.
Main Facts: The Anatomy of CVE-2026-78003
The core of the issue lies in how the Mailgun for WordPress plugin handles data submitted through its mailing list subscription features.
Specifically, the add_list() function—responsible for processing newsletter or mailing list sign-ups—fails to properly validate incoming array keys. While the developers utilized WordPress’s built-in sanitize_text_field() function to clean visitor-supplied data, this sanitization routine is completely ineffective against path traversal sequences.
How the Exploit Works
An unauthenticated attacker can craft a malicious HTTP request featuring manipulated array keys. Because the input is not sanitized against path traversal, the crafted key tricks the plugin into routing the request to any arbitrary destination within the Mailgun API framework.
Crucially, because the request is processed by the plugin itself, it is automatically signed using the victim website’s stored Mailgun API key.
- No Authentication Required: Attackers do not need an account, a login session, or any prior interaction with the target WordPress site.
- Scalable Automation: Because the attack vector relies on standard HTTP requests, malicious actors can easily script and automate exploitation at scale, scanning and compromising thousands of sites within minutes.
- Wordfence Classification: Leading WordPress security firm Wordfence formally classifies the bug as a severe Server-Side Request Forgery (SSRF) vulnerability.
The Attack Chain: From API Abuse to Admin Takeover
The most immediate and damaging abuse vector involves manipulating Mailgun’s inbound routing features. An attacker who successfully redirects API commands can configure custom inbound routes to quietly forward all incoming mail from the compromised domain directly to an attacker-controlled inbox.
Why is this devastating? Modern websites rely heavily on email for core security workflows—most notably, password reset requests.
Once an attacker intercepts inbound mail:
- They trigger a password reset for the WordPress site’s administrative account.
- The password reset link, generated by WordPress, is sent via email.
- Because the inbound route is compromised, the email goes straight to the attacker.
- The attacker uses the token to set a new password, achieving full administrative takeover of the WordPress backend.
Chronology of the Vulnerability and Patch Release
The discovery, patching, and public disclosure of the bugs associated with this incident followed a staggered timeline that has raised concerns regarding vulnerability communication transparency.
- July 9, 2026 (Version 2.2.1 Release): Mailgun quietly shipped version 2.2.1 of the WordPress plugin. This update closed two distinct security holes. The first, tracked as CVE-2026-14834, carried a CVSS score of 6.5 and allowed unauthenticated users to add arbitrary email addresses to a site’s mailing lists (list spam). The critical SSRF flaw was also patched in this release, though it was not publicly disclosed at the time.
- The Changelog Ambiguity: The official plugin changelog for version 2.2.1 merely noted that it prevented "unauthenticated arbitrary list subscription." It made no mention of API key exposure, SSRF vectors, or the risk of account takeover. Consequently, administrators who reviewed the update notes assumed the patch only mitigated minor spam nuisance, leading many to delay updating.
- August 22, 2026: Six weeks after the silent patch, CVE-2026-78003 (the high-severity SSRF flaw) was officially published and assigned its 9.8 CVSS score, alerting the broader security community to the true gravity of the July update.
- August 28, 2026: Threat intelligence firm VulnCheck reported observing active exploitation attempts targeting the vulnerability in the wild.
Supporting Data: Versions, Key Types, and Discrepancies
Understanding the scope of the vulnerability requires a closer look at plugin versions, the nature of Mailgun API keys, and conflicting reports regarding active exploitation.
Affected Versions
- Vulnerable: Versions up to and including 2.2.0.
- Patched: Versions 2.2.1 through 2.2.3 (with 2.2.3 serving as the current stable release).
- Mitigation Status: Sites utilizing automatic background updates are already protected. However, sites managed manually—especially those that skipped the July update due to the vague changelog—remain at high risk.
The API Key Dilemma
A critical factor in assessing the damage potential is the type of Mailgun API key stored within the WordPress plugin configuration:
- Primary Account Keys: These keys hold absolute, full control across every sending domain tied to the Mailgun account. If a site uses a primary key and is compromised, the attacker gains leverage over the entire Mailgun account, not just the single WordPress domain.
- Domain Sending Keys: These keys are restricted in scope, permitting mail dispatch for only one specific domain. While an attacker utilizing a sending key could spoof emails originating from the domain, they would lack the permissions required to create new inbound routes.
The Catch: Many WordPress site owners would prefer to use restricted sending keys for safety. However, because the plugin’s mailing list sign-up and management features require broader access rights, administrators often cannot downgrade their keys without breaking core site functionality. Whatever permissions the stored plugin key possesses, the attacker inherits.
Discrepancies Over Active Exploitation
Security vendors have expressed slightly varying assessments regarding whether widespread active exploitation was underway immediately upon disclosure:
- VulnCheck publicly documented exploitation attempts occurring as early as August 28, 2026.
- CISA (Cybersecurity and Infrastructure Security Agency) assessments, conducted slightly prior to VulnCheck’s findings, initially indicated no widespread exploitation.
- Industry groups such as emailexpert maintained monitoring positions while awaiting definitive confirmation of large-scale automated campaigns.
Regardless of differing intelligence timelines, security analysts emphasize that a 9.8-rated exploit with published proof-of-concept mechanics rarely remains unexploited for long.
Official Responses and Industry Reactions
The handling of the initial patch has drawn criticism from cybersecurity analysts who advocate for radical transparency in software updates.
When software vendors issue security patches without fully disclosing the underlying risk, they inadvertently gamble with user security. By framing the July 9 update as a fix for "unauthenticated arbitrary list subscription," Mailgun minimized the perceived urgency. In the fast-paced ecosystem of WordPress administration, where thousands of plugins demand weekly updates, system administrators naturally triage patches based on changelog descriptions. A fix for mailing list spam easily falls to the bottom of a busy webmaster’s to-do list.
Independent security researchers and threat intelligence platforms have used this incident to reiterate best practices for software supply chain management, urging plugin developers to explicitly tag security fixes with CVE identifiers and transparent severity warnings in their changelogs.
Implications and What Administrators Must Do Now
The fallout from CVE-2026-78003 extends far beyond Mailgun users, serving as a cautionary tale for any WordPress site utilizing Email Service Provider (ESP) integrations.
Broader Implications for WordPress Security
- The Danger of Stored Credentials: Plugins that interface with external cloud APIs via stored, high-privilege credentials represent prime targets for malicious actors. If a plugin is compromised, the external service account falls with it.
- The Cost of Silent Patches: Security through obscurity in patch notes fails to protect users. When vendors hide critical vulnerabilities behind vague release notes, they handicap the defensive response time of system administrators.
Actionable Remediation Steps
If you manage WordPress sites running the Mailgun plugin, take the following steps immediately:
- Verify and Update the Plugin: Ensure your Mailgun for WordPress plugin is updated to version 2.2.3 (or the latest available release). If your site has automatic updates enabled, verify that the upgrade successfully processed.
- Audit Mailgun API Logs: Check your Mailgun dashboard for any unusual API activity, unexpected route creations, or unfamiliar IP addresses accessing your account logs around late July and August 2026.
- Review Inbound Routes: Inspect your Mailgun account settings to ensure that no unauthorized inbound forwarding routes have been established—especially routes pointing to external or unrecognized email addresses.
- Rotate API Keys: As a preventative security hygiene measure, regenerate your Mailgun API keys within the Mailgun control panel and update them within your WordPress dashboard. This invalidates any stolen or cached keys that may have been harvested via the exploit.
- Inspect Administrative Users: Audit the WordPress user roster for any newly created administrator accounts or unauthorized modifications to existing admin credentials.