AMSTERDAM — In a series of sweeping decisions that could reshape how European courts view the intersection of data privacy and litigation tactics, a Dutch court has dismissed General Data Protection Regulation (GDPR) access claims brought by a serial litigant against four prominent retailers.
The District Court of Noord-Holland ruled in late July that the plaintiff’s systematic barrage of data access requests was not a genuine exercise of fundamental privacy rights, but rather a manufactured legal strategy designed explicitly to extract financial compensation. By weaponizing corporate anxieties surrounding compliance penalties and legal exposure, the individual sought to turn statutory transparency rights into a lucrative profit center.
The rulings mark the first time Dutch jurisprudence has officially integrated a landmark March 2026 European Court of Justice (CJEU) precedent, establishing a robust defense for businesses targeted by predatory data requests. Legal experts suggest the decisions offer a vital roadmap for retailers and other data controllers navigating bad-faith litigation, while simultaneously underscoring the high evidentiary bars required to successfully counter such schemes.
Main Facts of the Case
The legal showdown centers on four parallel rulings handed down by the District Court of Noord-Holland, targeting four distinct commercial entities: apparel retailer Suitable, footwear chain Scapino, lifestyle brand At Home, and interior design businesses Wolters Wonen and Fundesign.
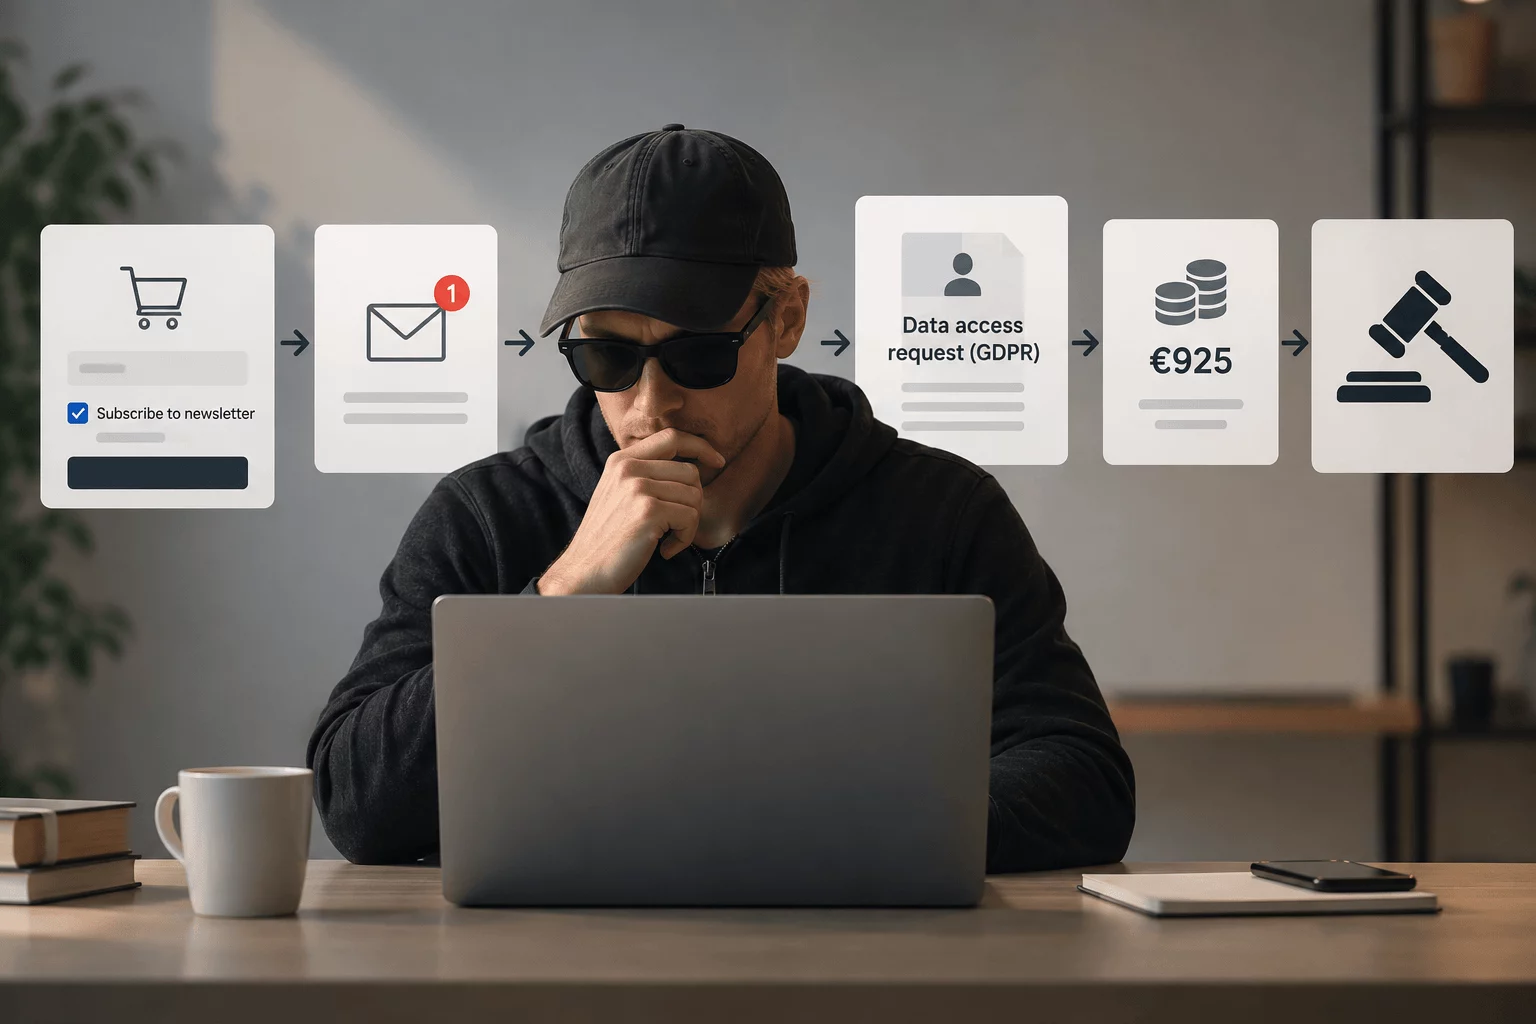
In each instance, the district court declared the applicant’s GDPR Article 15 access claims entirely inadmissible. The court found that the plaintiff had knowingly and artificially engineered situations—such as placing minor online orders or subscribing to promotional newsletters—solely to trigger a paper trail. This manufactured interaction formed the predicate for subsequent legal maneuvers.
According to a detailed analysis of the judgments published by legal platform ICTRecht, the mechanics of the scheme followed a rigid, predictable playbook:
- The Trigger: The individual created a consumer profile by making a minor purchase or opting into a marketing newsletter.
- The Hook: Shortly after establishing this digital touchpoint, the applicant submitted a formal GDPR Article 15 request, demanding comprehensive access to their personal data.
- The Escalation: Within weeks of the initial request, the retailer received a demand for €925 in extrajudicial collection costs.
- The Ultimatum: This demand was quickly followed by a settlement proposal delivered under the immediate threat of a formal court summons.
- The Bait-and-Switch: The subsequent summons typically claimed substantial damages alongside procedural costs. However, just hours before court hearings commenced, the plaintiff abruptly slashed the claim back to a demand for data access alone, offering no coherent legal justification for the sudden pivot.
During proceedings, the plaintiff admitted to a staggering volume of litigation, testifying that he had filed approximately 90 distinct access requests across an 18-month window. At the time of the Noord-Holland hearings, roughly 20 of these cases were actively pending within that specific district, while parallel litigation was winding its way through courts in Rotterdam and Midden-Nederland.
Compounding the court’s skepticism were glaring procedural anomalies. Judges openly questioned the legitimacy of the legal representatives named in the plaintiff’s filings, noting that these purported representatives never once materialized at a hearing.
Ultimately, the District Court of Noord-Holland ruled that the litigant was engaging in an abuse of rights. The bench asserted that the plaintiff had exploited businesses’ widespread unfamiliarity with the nuances of GDPR compliance and their paralyzing fear of substantial statutory damages or regulatory fines.
Chronology of the Legal Battle
To understand the broader implications of the Noord-Holland rulings, legal analysts have traced the timeline from initial consumer interaction to the courtroom showdown, highlighting how corporate vigilance transformed a potential liability into a landmark legal victory.
The Inception Phase (2024–2025)
Over an 18-month span, the individual systematically targeted dozens of Dutch and international retailers. By deploying automated scripts or manual sign-ups, the plaintiff established a footprint across various e-commerce platforms. The strategy relied on the fact that modern retail systems automatically log user data upon newsletter registration or checkout—data that subsequently forms the mandatory scope of a GDPR Article 15 response.
The Escalation and Extortion Window (Early 2026)
Once the data access requests were dispatched, the plaintiff’s legal proxies initiated rapid-fire secondary demands. Retailers, many lacking dedicated in-house compliance teams or sophisticated legal counsel, faced an unenviable choice: invest significant resources in investigating and responding to complex data requests, or pay a relatively modest "settlement" fee of €925 to make the legal threat disappear.
The CJEU Intervenes (Brillen Rottler v TC, March 19, 2026)
Crucially, the timing of the Dutch court’s late July rulings directly intersects with a critical European-level decision. On March 19, 2026, the European Court of Justice (CJEU) delivered its judgment in Brillen Rottler v TC (Case C-526/24).
Like the Dutch cases, the Brillen Rottler dispute originated from a seemingly innocuous newsletter signup followed immediately by a formal access request. The CJEU squarely addressed the issue of bad faith, ruling that even a first-time access request can be deemed "manifestly excessive" under Article 12(5) of the GDPR if the data subject has artificially created the underlying conditions solely to secure a financial advantage.
The Noord-Holland Hearings (Mid-2026)
Armed with the fresh Brillen Rottler precedent, the District Court of Noord-Holland became the first in the Netherlands to apply the CJEU doctrine. Even though one of the defendants—Scapino—failed to explicitly argue "abuse of rights" in its initial defense, the court exercised its judicial prerogative to raise the issue sua sponte (of its own motion), recognizing the broader societal harm posed by the litigation scheme.
Supporting Data and Procedural Outcomes
While the retailers successfully defeated the core access claims, the financial and procedural outcomes varied significantly depending on the diligence of each company’s legal defense team. The judgments offer a masterclass in civil procedure regarding how corporate defendants recover costs in bad-faith litigation.
Cost Recovery and Legal Budgets
The court’s approach to legal fees underscores the critical importance of meticulous administrative and financial accounting during litigation:
- Suitable: Secured a comprehensive cost award of €7,047.97 covering actual legal expenses. This favorable outcome was achieved because Suitable’s legal counsel submitted a detailed, itemized budget of their legal costs to the court.
- Wolters Wonen / Fundesign: Received a cost award of €2,230. However, because these entities failed to submit a formalized legal budget, the court awarded costs strictly at the standard, baseline liquidation rate rather than compensating for actual expenditure.
- Scapino and At Home: Navigated similar dismissals, though specific cost determinations hinged on their respective evidentiary submissions.
The Failure of Counterclaims
Interestingly, while the defendants successfully fended off the plaintiff’s primary claims and recovered legal costs, their counterclaims for compensatory damages largely collapsed. The court noted that none of the retailers had successfully quantified their financial or operational losses resulting from the abusive litigation. This evidentiary gap prevented the bench from awarding punitive or compensatory damages back to the harassed businesses, serving as a reminder that courts require hard figures—such as hours diverted from business operations or quantifiable administrative expenses—to justify counter-damages.
Official Responses and Legal Analysis
Legal professionals and privacy advocacy groups have hailed the Noord-Holland rulings as a watershed moment for regulatory enforcement, drawing a sharp line between legitimate data privacy rights and opportunistic legal maneuvers.
The View from ICTRecht
Analysts at ICTRecht, who provided a comprehensive breakdown of the August 2026 jurisprudence, emphasized that the rulings dismantle the misconception that data controllers are entirely helpless against serial litigants.
"The court has made it abundantly clear that the GDPR is a shield for personal data protection, not a sword for financial extortion," noted legal commentators in the ICTRecht privacy blog. "When a requester manufactures their own data footprint solely to generate a legal dispute, the protections of Article 15 fall away under the weight of Article 12(5)."
Balancing Act: A Narrow Interpretation Required
Importantly, legal experts are urging data controllers not to overcorrect in the wake of these decisions. The court explicitly stressed that the legal bar for proving an "abuse of rights" remains exceptionally high.
The plaintiff’s pattern in these specific cases—characterized by dozens of identical summonses, rapid-fire cost demands, and coordinated automated behavior—was described by the bench as "extreme." Consequently, data controllers cannot use the Noord-Holland rulings as a blanket excuse to ignore or dismiss awkward, difficult, or critical data access requests from genuine consumers.
A single, unanticipated access request from an unknown subscriber still requires a thorough, good-faith response under GDPR guidelines. Dismissing a request without concrete, provable indicators of bad faith exposes a company to severe regulatory penalties from data protection authorities (DPAs).
Implications for Businesses and Data Controllers
For compliance officers, legal counsels, and e-commerce operators across Europe, the Noord-Holland rulings provide both a powerful defensive framework and a stark operational warning.
1. The Necessity of Robust Record-Keeping
To successfully replicate the defense mounted by Suitable and other retailers, data controllers must maintain pristine internal logs. The court relied heavily on objective indicators to establish the plaintiff’s abusive pattern, including:
- Source and Timestamp: Exact records of how and when a user opted into a newsletter or created an account.
- Consent Logs: Verifiable proof of marketing consent or transactional history.
- Communication Trails: A chronologically organized audit log tracking how each individual access request was received, processed, and responded to.
Without these foundational data points, proving that a requester "artificially created the conditions" for a dispute becomes nearly impossible.
2. Spotting the Red Flags
Compliance teams are now better equipped to identify potential serial litigants early in the lifecycle of a request. Key warning signs highlighted by the Dutch litigation include:
- Immediate submission of an Article 15 request directly following a low-friction interaction (e.g., a free newsletter subscription).
- Rapid escalation to monetary demands or extrajudicial cost recovery within a matter of weeks.
- Standardized, copy-pasted legal language across multiple claims.
- A sudden, unexplained modification of claims immediately preceding a scheduled court appearance.
3. Precision in Defense and Cost Submissions
The disparity between Suitable’s cost recovery (€7,047.97) and Wolters/Fundesign’s standard award (€2,230) serves as an urgent lesson for corporate legal teams. When defending against abusive GDPR claims, companies must proactively submit detailed, itemized budgets of their legal expenditures rather than relying on standard court-calculated minimums. Furthermore, businesses seeking counter-damages must invest the analytical effort required to rigorously quantify the operational disruption caused by bad-faith actors.
Conclusion
The District Court of Noord-Holland’s late July rulings—anchored by the European Court of Justice’s Brillen Rottler framework—strike a crucial blow against the financialization of privacy law. By confirming that the GDPR cannot be exploited as an extortion tool, the Dutch judiciary has reinforced the integrity of European data protection regulations while offering a vital shield to businesses operating in the digital economy.