WELLINGTON — In the modern legal ecosystem, client confidentiality is the bedrock upon which the entire profession is built. Whether it is sensitive family court proceedings, high-stakes corporate mergers, or confidential property transactions, clients entrust law firms with some of the most intimate and vulnerable details of their lives. When a breach occurs, the expectation of swift transparency is paramount.
However, a newly released regulatory decision has laid bare a systemic organizational failure that left clients in the dark for half a year after an unauthorized party infiltrated a New Zealand law firm’s email system.
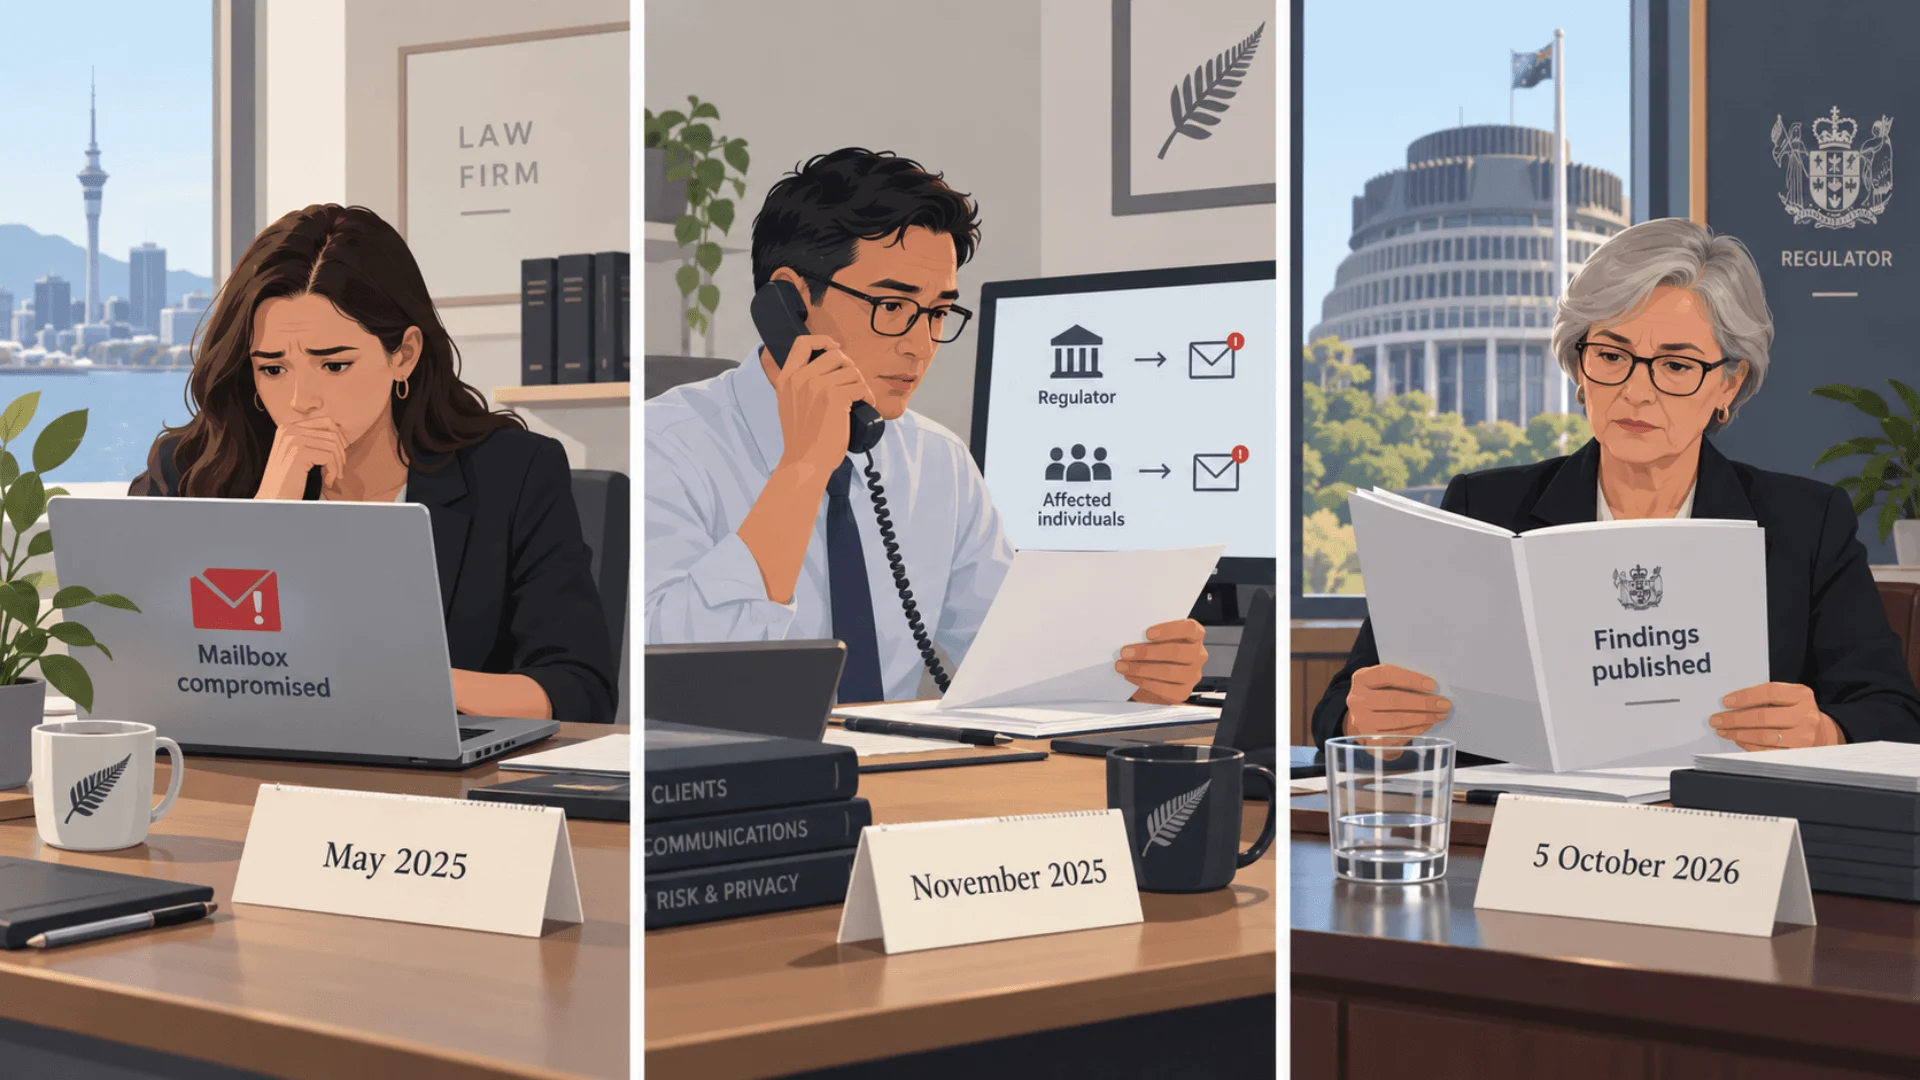
According to an official decision note published on October 5, 2026, by New Zealand’s Office of the Privacy Commissioner (OPC), an unnamed law firm suffered an email account compromise in May 2025. Despite having digital forensic evidence in hand confirming the unauthorized intrusion that same month, the firm failed to notify either its affected clients or the privacy regulator until November 2025.
The six-month information blackout has emerged as the central point of contention for the regulator, exposing critical vulnerabilities in how professional services firms handle the intersection of cyber security incidents and statutory privacy obligations.
Main Facts
The incident centers on a compromised email account that granted an unknown third party deep, unfettered access to sensitive personal and confidential information belonging to the firm’s clients. While cyber security breaches of this nature are an escalating reality for modern businesses, the catastrophic failure in this case was not the intrusion itself, but the organizational paralysis that followed.
Key elements of the case established in the OPC’s decision note include:
- The Timeline Gap: An unauthorized actor accessed a firm email account in May 2025. Forensic findings confirming the intrusion were delivered to the firm the same month. Clients and the Privacy Commissioner were left uninformed until November 2025—a delay of approximately six months.
- The Categorization Error: The firm’s leadership treated the incident strictly as an IT "cyber security issue" rather than a legal "privacy breach." Consequently, the necessary statutory assessments required under New Zealand privacy law were never initiated.
- Internal Structural Deficiencies: The firm operated without a formalized incident response plan for privacy breaches. Responsibility for handling privacy matters was delegated to an office manager who lacked adequate training to recognize, evaluate, and escalate a data privacy violation.
- Regulatory Scrutiny: While the OPC’s decision note outlines the severe timeline failures, it explicitly omits the identity of the law firm, the identity of the email service provider, the exact mechanism of the compromise, and the precise number of clients whose data was exposed.
The case serves as a stark reminder that in the digital age, a cybersecurity defense failure is inherently a privacy failure, demanding immediate multidisciplinary coordination rather than isolated IT remediation.
Chronology of Events
Understanding how a major privacy breach can remain hidden in plain sight for nearly half a year requires a detailed examination of the timeline between discovery and disclosure.
- May 2025 (The Intrusion and Discovery): An unauthorized third party gains access to a staff member’s email account at the law firm. Recognizing unusual activity, the firm engages digital forensics professionals to investigate. The resulting forensic report confirms that the mailbox has indeed been accessed without authorization, exposing sensitive client correspondence and data.
- May to October 2025 (The Operational Blind Spot): The forensic report is delivered to the firm. However, because the incident is narrowly framed as a technical IT problem, the report is filed away or handled purely from a system-recovery standpoint. The firm takes steps to secure the compromised account but fails to evaluate the contents of the mailbox against privacy legislation. No privacy breach assessment takes place, and no notifications are triggered.
- November 2025 (Delayed Disclosure): For reasons not fully detailed in the public decision note, the firm finally recognizes the broader implications of the May forensic findings, or belatedly applies privacy protocols, prompting late notifications to the OPC and impacted clients.
- October 5, 2026 (Regulatory Judgment): Following its investigation into the delayed disclosure, the OPC publishes Decision Note PBN4406 (2026 NZPrivCmr 2), publicly rebuking the firm for its six-month reporting delay while utilizing the case as an educational warning for the broader legal and commercial sectors.
Supporting Data and Legal Framework
The legal framework governing this incident is anchored in the Privacy Act 2020, specifically regarding the mandatory reporting of notifiable privacy breaches. The regulatory expectations are rigorous, leaving little room for ambiguity regarding when and how organizations must act.
The Notifiable Privacy Breach Threshold
Under Section 112 of the Privacy Act 2020, an organization must treat a privacy breach as "notifiable" if it has caused, or is likely to cause, serious harm to any affected individuals.
Once an organization determines that a breach crosses this threshold, it has a statutory duty to notify both the Privacy Commissioner and the affected individuals "as soon as practicable" after becoming aware of it. The OPC interprets this standard tightly, explicitly stating that organizations are expected to make initial contact within 72 hours of realizing that a breach is notifiable. Recognizing that facts take time to uncover during an active investigation, the Act allows for phased notifications under section 117(5) as new information emerges.
The Doctrine of Imputed Knowledge
One of the most vital legal principles reinforced in the OPC’s decision note addresses corporate awareness. The regulator made it abundantly clear that information known to an organization’s employees, contractors, or third-party service providers is legally imputed to the organization as a whole.
In this case, the moment the forensic investigators finalized their report confirming the mailbox compromise, the organization was legally "aware" of the incident. The firm cannot defend its delay by arguing that upper management, partners, or privacy officers had not personally read or digested the technical report. Furthermore, the OPC advises that organizations should explicitly contract with third-party IT and forensic providers to ensure they have immediate, structured obligations to report identified breaches directly back to the client.
Legal Penalties and Defenses
Failing to notify the Privacy Commissioner of a notifiable breach without a reasonable excuse is a criminal offense under New Zealand law, carrying a potential fine of up to NZ$10,000.
The statute establishes clear boundaries regarding what constitutes a legal defense:
- Remediation is not a defense: Taking subsequent technical steps to patch a vulnerability, reset passwords, or secure an IT environment does not excuse an organization from its duty to notify.
- Reasonable belief is a defense: An organization has a valid defense if it can demonstrate that it held a reasonable belief at the time that the breach did not meet the threshold of causing serious harm.
In this specific instance, the decision note records no formal punitive enforcement action or prosecution taken against the firm, focusing instead on public regulatory guidance and systemic correction.
Official Responses and Regulatory Perspective
The Office of the Privacy Commissioner has used this case to drive home a broader cultural message regarding organizational accountability. Privacy Commissioner representatives emphasize that data governance cannot be siloed within a technical IT department or relegated to an untrained administrative assistant.
When organizations fail to notify individuals promptly, they rob those people of their agency. Instant notification allows victims of data breaches to take self-protective measures—such as updating compromised credentials, freezing financial accounts, altering security questions, and remaining vigilant against targeted phishing scams that leverage leaked correspondence. When individuals are kept in the dark for months, their window of vulnerability remains wide open, heightening the risk of secondary victimizations like identity theft or financial fraud.
Furthermore, individuals who discover they were victims of an unreported or excessively delayed breach retain the right to lodge formal complaints with the OPC. This exposes the negligent organization to extended regulatory investigations, reputational damage, and potential enforcement actions.
The regulator’s stance is uncompromising: when a mailbox is compromised, the privacy clock starts ticking immediately. Ignorance of the law, absence of internal training, or administrative oversight do not reset that clock.
Implications for Businesses and the Legal Sector
While the decision note shields the identity of the specific law firm involved, the operational lessons reverberate across the entire corporate and professional services landscape—particularly for businesses that store confidential client data within cloud-based email environments, databases, and document management systems.
1. The Necessity of an Incident Response Plan (IRP)
Every modern organization, especially law firms handling privileged data, must possess a comprehensive, written Privacy Breach Response Plan. This plan cannot be a static document gathering dust on a shelf; it must be actively understood by leadership, administrative staff, and IT contractors alike. The plan must clearly outline:
- Who is responsible for evaluating incidents.
- How IT security incidents are escalated to privacy compliance officers.
- The exact internal workflows required to assess the risk of "serious harm."
2. Training and Empowerment
Delegating privacy compliance to an office manager without providing adequate, ongoing training is a recipe for regulatory disaster. Frontline administrative staff, IT personnel, and executive leadership must receive regular education on how to spot a privacy breach, understand statutory obligations under the Privacy Act 2020, and initiate mandatory reporting protocols.
3. Leveraging Regulatory Resources
Organizations do not have to navigate the complex world of data compliance in isolation. The OPC provides extensive public resources designed to help businesses build resilient frameworks:
- The Poupou Matatapu Toolkit: A comprehensive guide provided by the OPC to help organizations establish robust privacy frameworks and effective breach management strategies.
- Free Online Privacy Training: Accessible modules offered directly through the Privacy Commissioner’s website, empowering staff at all levels to identify, assess, and properly escalate potential privacy breaches.
Conclusion
The six-month information blackout documented in Decision Note PBN4406 stands as a cautionary tale for New Zealand businesses. Cybersecurity defenses will always face sophisticated threats, and intrusions, while regrettable, can happen to any organization. However, the true test of an enterprise’s integrity is not whether it can prevent every cyber attack, but how swiftly, honestly, and transparently it responds when the perimeter is breached. For the legal sector, where trust is the ultimate currency, treating a data breach as merely an IT problem rather than a profound privacy violation is a risk no firm can afford to take.